 Do Son
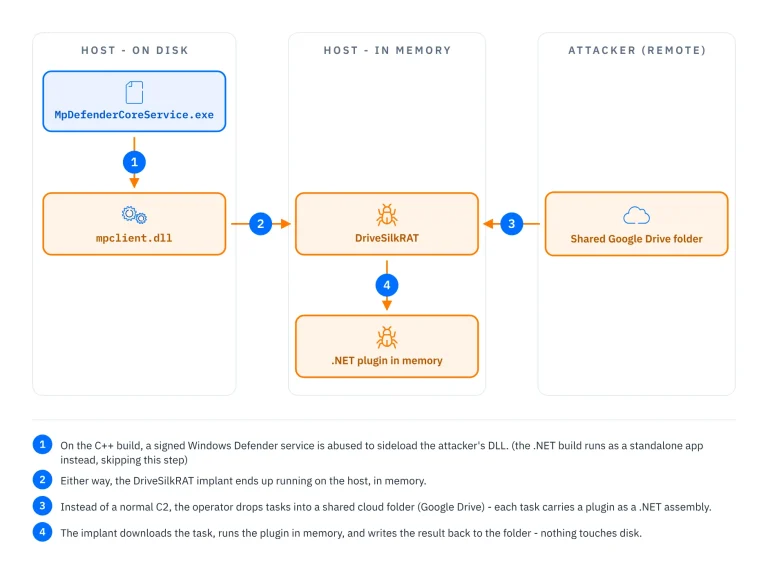
SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.
China-nexus
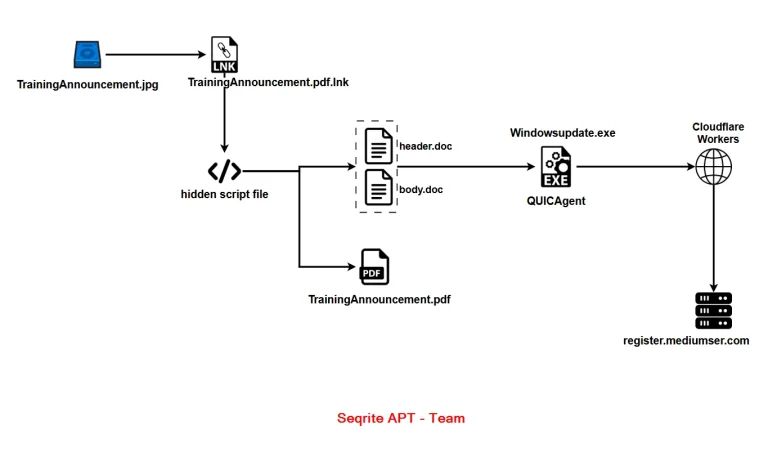
Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.

UAT-7810, a China-nexus APT, grows its LapDogs ORB network with new router malware including LONGLEASH, DOGLEASH, and JARLEASH. Cisco Talos reports.
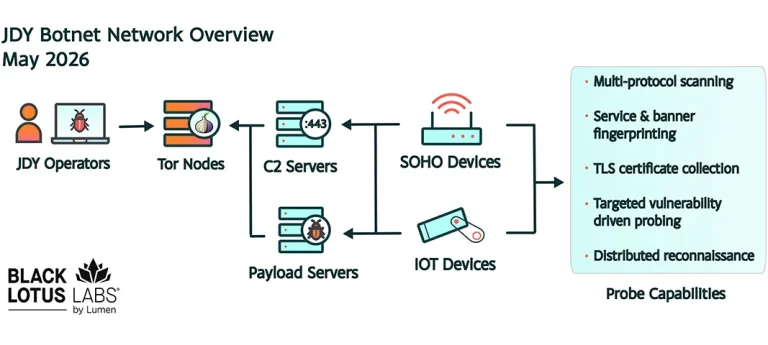
The JDY botnet, a China-nexus IoT network tied to Volt Typhoon, now spans 1,500+ devices and scans for new bugs like CVE-2026-35616 within hours.
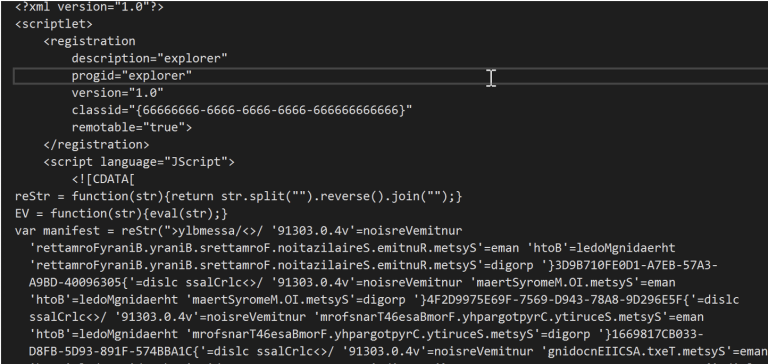
A stealthy Twill Typhoon RAT campaign targets APJ organizations. Discover how this threat exploits DLL side loading tradecraft to evade security.
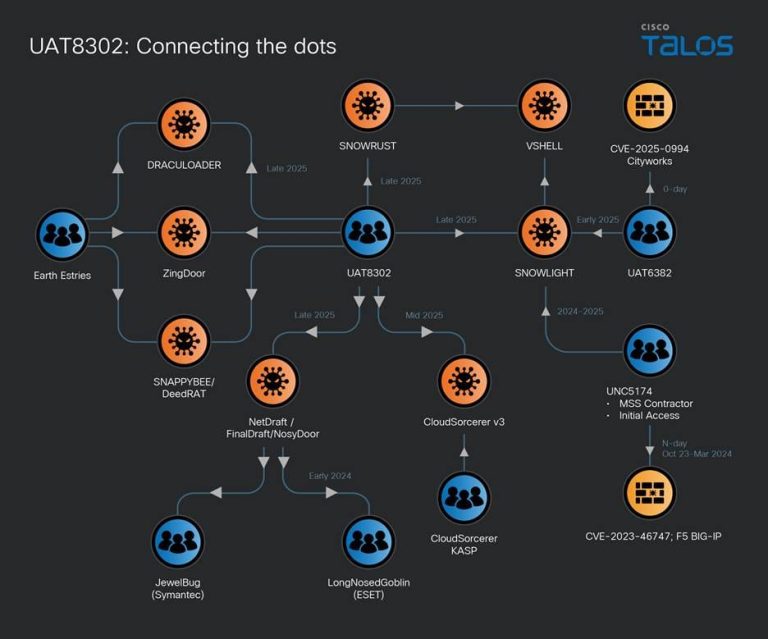
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.
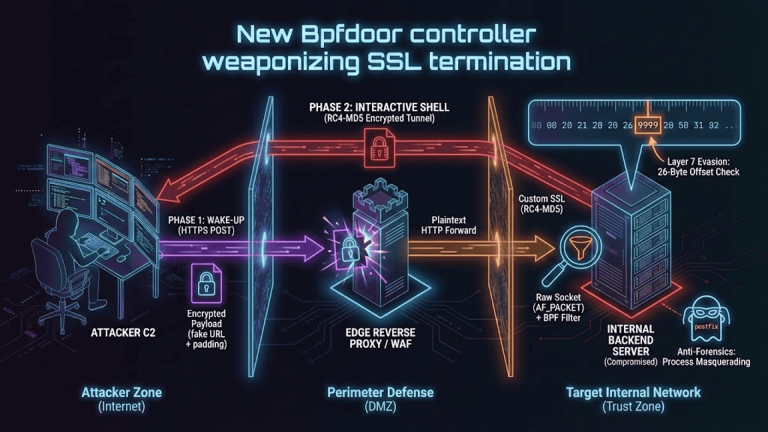
Rapid7 uncovers Red Menshen’s BPFdoor backdoor in global telecom cores. Learn how this China-nexus actor uses kernel-level stealth for mass surveillance.
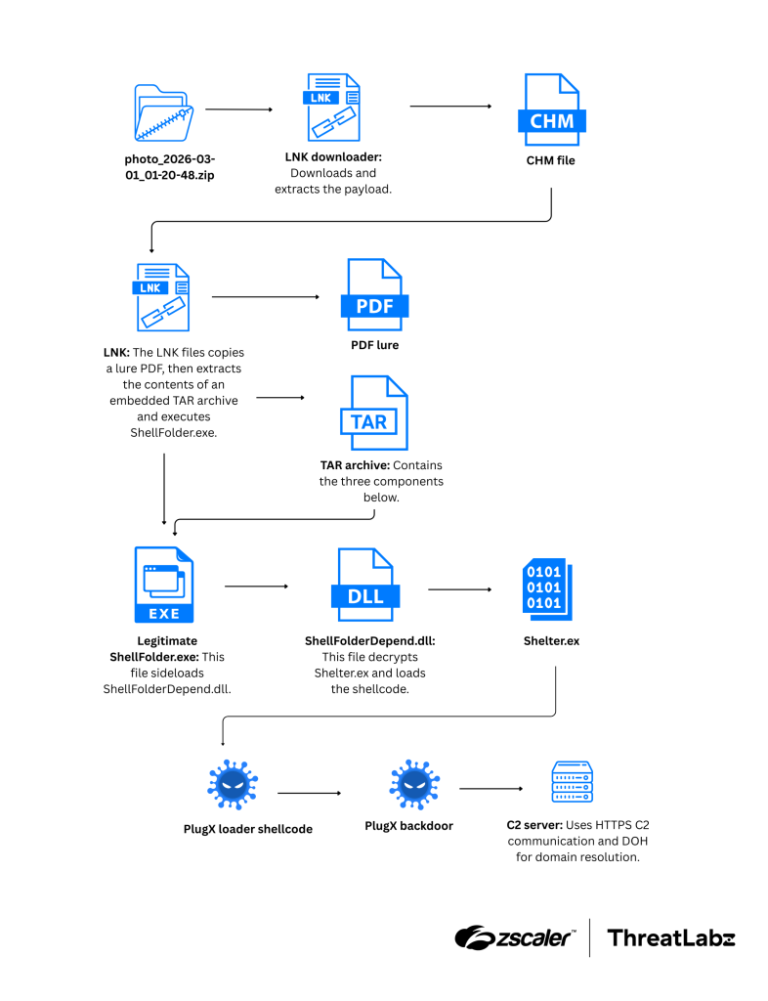
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.
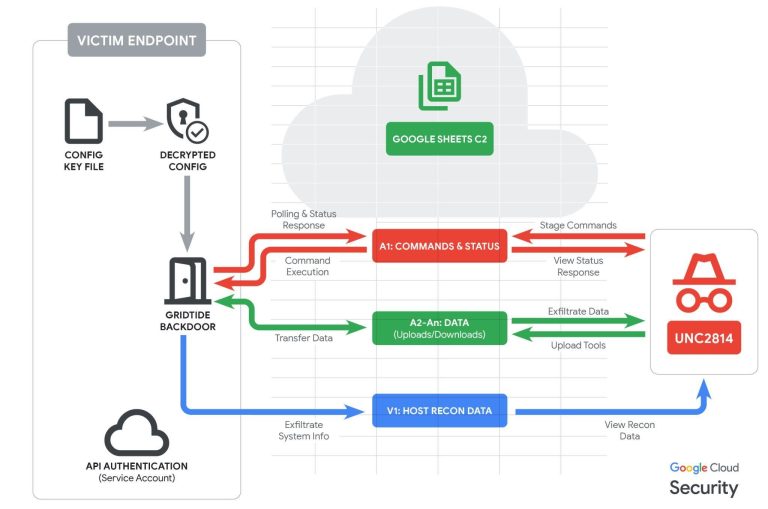
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

Cisco Talos warns: China-linked UAT-8837 targets North American infrastructure using zero-days (CVE-2025-53690) & open-source tools.

GOLD SALEM (Storm-2603) is exploiting SharePoint via ToolShell then abusing the Velociraptor DFIR tool as a ransomware precursor. The group deploys Warlock and LockBit 3.0 variants, often targeting critical infra.

Huntress exposed a covert campaign using log poisoning on exposed phpMyAdmin to deploy a web shell and the Nezha monitoring tool, ultimately delivering the Ghost RAT backdoor to 100+ victims in Asia.
GTIG reveals BRICKSTORM, a stealthy Go backdoor linked to China-nexus UNC5221, targeting US legal/SaaS firms to steal IP and establish long-term espionage access.

SecurityScorecard's STRIKE team exposes "LapDogs," a covert China-Nexus ORB network with 1,000+ infected SOHO devices, using the custom ShortLeash backdoor for cyberespionage.

SentinelLABS exposes China-nexus APTs (ShadowPad, PurpleHaze) targeting SentinelOne and over 70 organizations in extensive cyber-espionage.