 Do Son
CISA warns of 11 Ebyte NE2-D11 vulnerabilities, four rated 9.8, that allow full device takeover. No patch is confirmed available yet.
CISA advisory
CISA warns of a Gardyn IoT Hub flaw. CVE-2026-13768 (CVSS 10) enables unauthenticated remote code execution on smart garden devices. Update now.
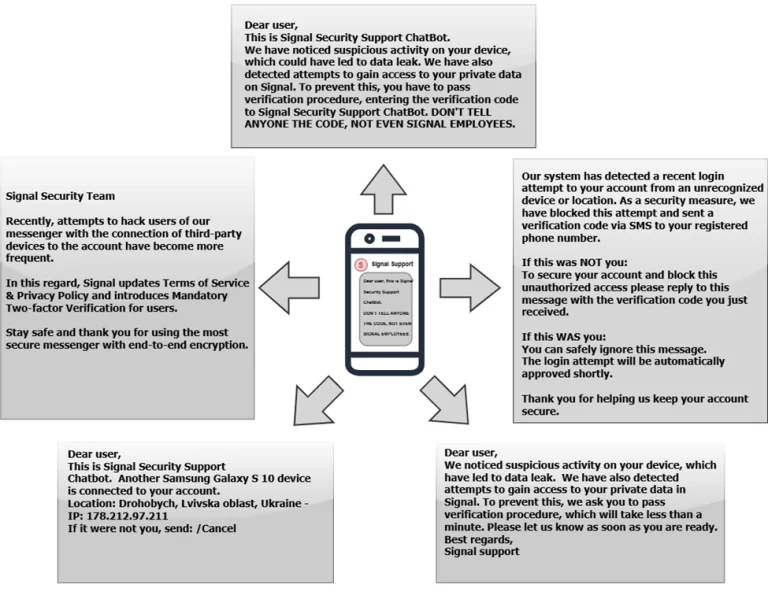
The FBI and CISA warn that Russian Intelligence is using sophisticated phishing to hijack Signal and other messaging apps via linked device features.

CISA issues an urgent ICS advisory (ICSA-26-057-04) for the EV2GO charging platform. Critical 9.4 severity flaws allow for session hijacking and station impersonation.
CISA warns of critical flaws (CVE-2025-29631) in Gardyn Home Kits allowing unauthenticated RCE and admin access. Update your app and firmware immediately!

CISA warns of critical flaws in EOL USR-W610 IoT servers. CVE-2026-25715 allows full admin control via blank passwords. No patches planned; isolate now.
CISA warns of critical CVSS 9.8 flaws in Vertiv Liebert devices allowing RCE and auth bypass—patch now to protect OT environments.

CISA warns of critical flaws in KUNBUS Revolution Pi that allow remote code execution, authentication bypass, and XSS attacks in industrial systems.

CISA warns of critical vulnerabilities in Planet Technology products, including command injection and hardcoded credentials, allowing attackers to manipulate devices.