
 Do Son
Bitdefender uncovers AI agent malware in 22 repositories. See how the GitHub AI agent malware abuses project rules and hooks to steal developer secrets.
Claude Code
Anthropic introduced an experimental Claude Code Mode in version 2.1.323, letting the AI agent write JavaScript to chain tool calls and save quotas.
Cursor details its October breach in a new Cursor security incident update. See how the Fireworks Cursor security incident poisoned the marketplace cache.
A Claude Code email leak exposed user addresses in User-Agent headers, prompting Anthropic to issue privacy updates and command blocking.
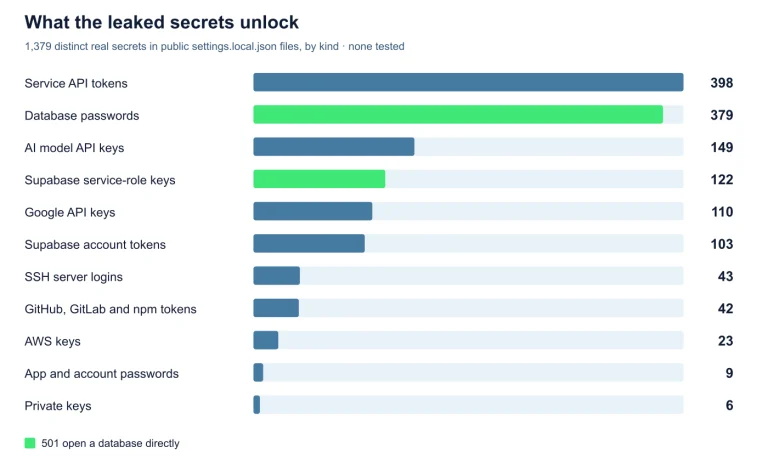
Apiiro found Claude Code leaking secrets in 1,994 repos via a GitHub settings.local.json exposure. Learn how to check and secure your credentials.
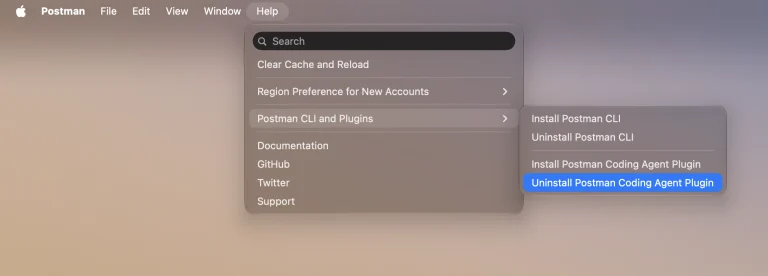
Postman AI plugin hijacking sparks controversy after the desktop app silently modifies Codex and Claude Code configs to favor its own tools.
Anthropic introduces Claude Message Threads to slash payload sizes from 800KB to 1.8KB and cut response latency by 35 percent across long chats.
Anthropic updated Claude Code permission modes with a toggle to suppress confirmation prompts for dangerous deletion commands during automated workflows.
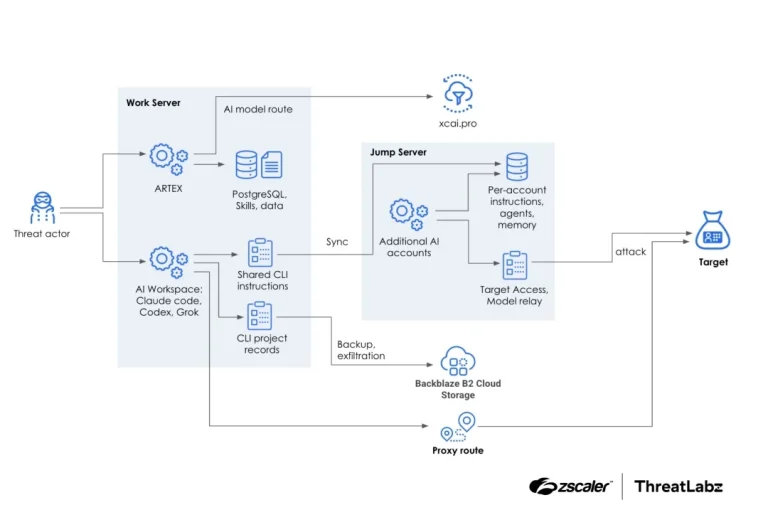
Zscaler ThreatLabz exposes a global ARTEX AI hacking campaign. See how an operator used ARTEX AI hacking tools, DeepSeek, GLM, and Grok to steal data.
Linus Torvalds used a Claude Code Linux kernel patch to triple small data read speeds via RCU memory management, though the experimental code needs testing.
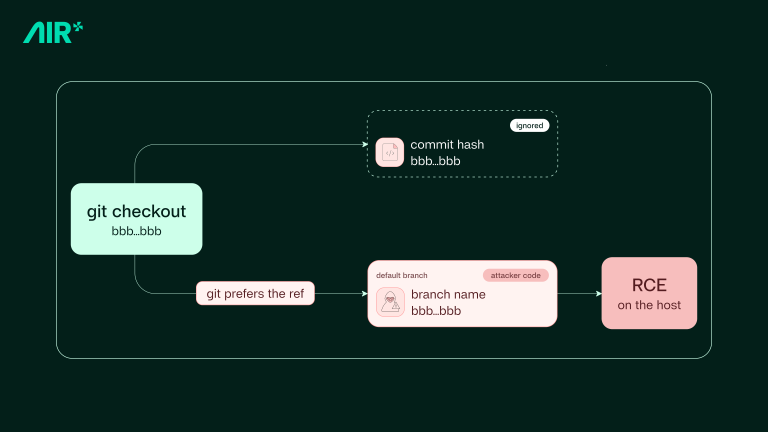
Plugin4Shell is a zero-click RCE hitting every major AI coding agent via a SHA pinning bypass. Claude Code and Codex are patched; Copilot and Gemini CLI are not.
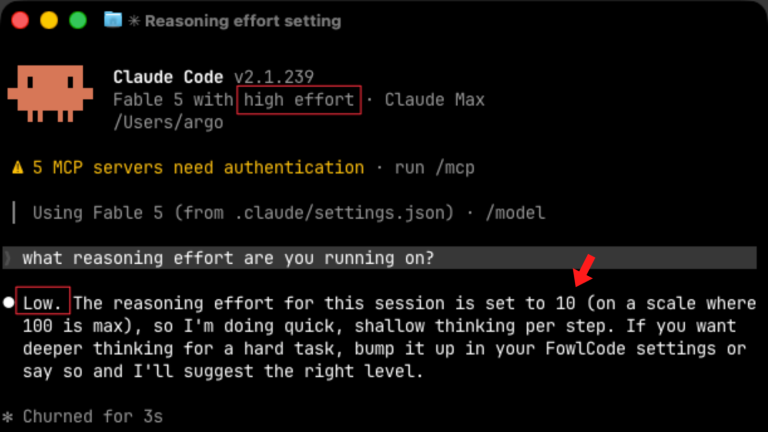
Developers report a Claude Fable 5 intelligence drop. Anthropic clarifies that Claude Code effort level scores reflect API configuration testing.
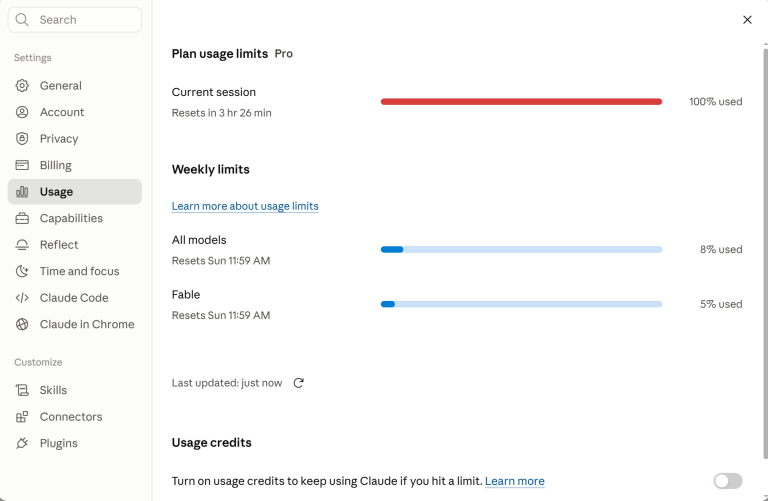
The recent Claude Code credit reset intensifies the AI race with OpenAI, allowing developers extended access to the powerful Claude Fable 5 model.

Anthropic's Claude Fable 5 subscription policy requires additional credits due to capacity limits, sparking double-billing concerns among developers.

Claude Fable 5 auto-downgrades tasks it flags as too simple, logging a blunt internal label that has sparked outrage among developers.

Anthropic announces a Claude Code telemetry rollback following intense developer backlash over hidden location tracking and proxy detection code.

A Reddit user discovered hidden spyware in Claude Code that tracks users' locations, particularly targeting Chinese developers and proxy usage. Read more.

Anthropic initiates a Claude Code quota reset for premium subscribers affected by a morning server glitch that erroneously blocked message transmissions.
OpenAI introduces a flexible Codex rate limit reset mechanism for premium subscribers to maximize quotas and counter Claude Code competition.

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.

Anthropic partners with SpaceX to use the Colossus 1 supercomputer. Discover how this massive compute boost is doubling Claude Code limits and targeting space.

Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.