 Do Son
TP-Link patched 5 TP-Link router vulnerabilities in ISP-managed mesh, router, and modem lines, including auth bypass and command injection.
Command Injection
Dell VSI for VMware vSphere Client has a critical unauthenticated RCE flaw (CVE-2026-67261) rated CVSS 9.8. Patch now.
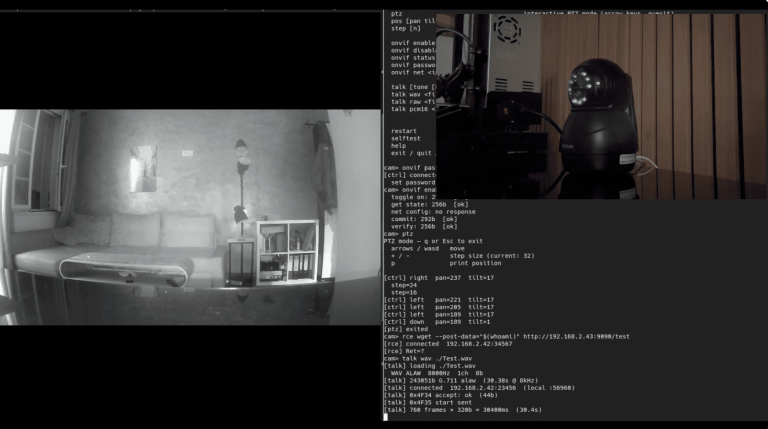
PoC exploit code is public for CVE-2026-61515, an unauthenticated command injection in Puwell IP Camera firmware. CVSS 9.3. Details inside.
CVE-2026-9044 is a command injection flaw in TP-Link Archer AXE75 OpenVPN, CVSS 8.5. Update to firmware 1.5.6 Build 20260623 now.
Cisco IOS XE vulnerability CVE-2026-20272 hits CVSS 9.8 and CVE-2026-20267 scores 9.0. Cisco urges customers to patch now.
Mitel patched a MiCollab command injection flaw rated CVSS 9.8 and an OpenScape UC vulnerability rated CVSS 8.0. No CVE IDs are assigned yet.
A Network UPS Tools RCE (CVE-2026-54161) lets a malicious upsd trigger upsmon command injection as root. No patch exists yet, so mitigate now.
BMC patches Control-M command injection flaw CVE-2026-10539, an unauthenticated remote command injection bug rated CVSS 9.5.
Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.
A critical IBM Power HMC vulnerability (CVE-2026-12943) allows unauthenticated attackers to execute commands. Patch your systems immediately.
Five StoneFly Storage Concentrator flaws include two CVSS 10 command injection bugs allowing unauthenticated root RCE. Update to 8.0.4.29 now.
Attackers now target the Kemp LoadMaster RCE vulnerability (CVE-2026-8037) using a public PoC. Patch to 7.2.63.2 or 7.2.54.18 immediately.
A CVSS 8.7 TP-Link router command injection flaw allows unauthenticated remote code execution. Patch CVE-2026-11834 to stop this DHCP option vulnerability.
Mitel patched 12 critical MiCollab vulnerabilities, several at CVSS 10.0. Unauthenticated command injection and SQL injection flaws need urgent updates.
QNAP patched 14 NAS vulnerabilities in QTS, QuTS hero, and QVP, including command injection and credential-theft flaws. Update your QNAP NAS now.

A critical Fortra BoKS vulnerability (CVE-2026-9862) enables remote OS command injection via the autoregistration service. Mitigate now.
Three NVIDIA NeMo vulnerabilities (CVE-2026-24155, CVE-2026-24252, CVE-2026-24228) enable code execution. Update NeMo Framework to v2.7.3 now.
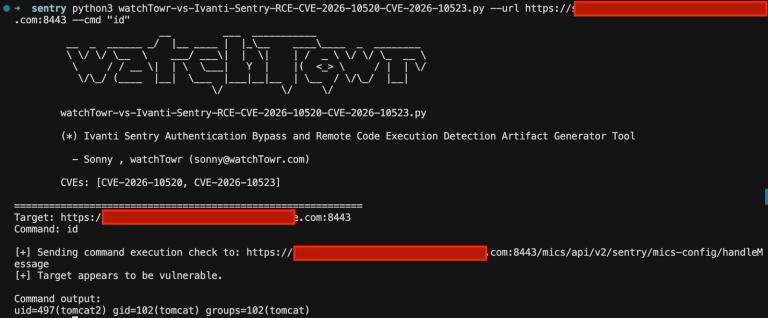
Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.
The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

New Ivanti EPMM security updates address high-severity flaws that could allow a remote authenticated attacker to achieve remote code execution.

An urgent patch fixes the critical CVE-2026-25089 FortiSandbox bug. Attackers can execute remote commands, so update your systems immediately.

A critical Archer MR600 command injection vulnerability surfaces within the WireGuard client configuration. Update your TP-Link firmware now.