 Do Son
Mitel OpenScape 4000 fixes two CVSS 10.0 flaws, an authentication bypass and a command injection, in V11 R2.14. OpenScape 4000 Manager is affected too.
Command Injection
MiCollab vulnerabilities fixed: MTLVULN-1864 (CVSS 10.0) command injection and a 9.0 XML injection allow unauthenticated attacks. Patch 10.3.0.18.
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
3DEXPERIENCE vulnerability CVE-2026-93664 (CVSS 10) allows unauthenticated RCE, and CVE-2026-77033 adds command injection in Station Launcher.
Zenitel vulnerabilities fixed: CVE-2026-95377 gives root on intercoms via DHCP, and a CVE-2026-95615 chain roots Zenitel Connect. Update to 1.11.0.
Mitel fixes three MiVoice MX-ONE vulnerabilities, including a CVSS 9.4 authentication bypass and command injection. Apply 8.2 SP1 HF2 now.
Zoho fixes eight ManageEngine vulnerabilities in DDI Central and ADAudit Plus, including Cisco router command injection and SQL injection flaws.
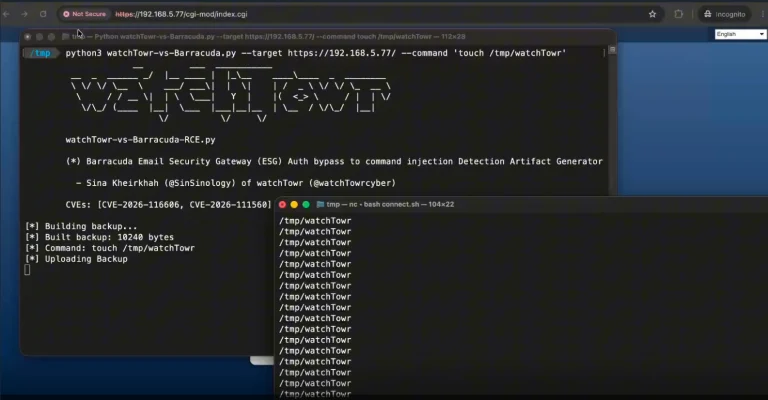
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
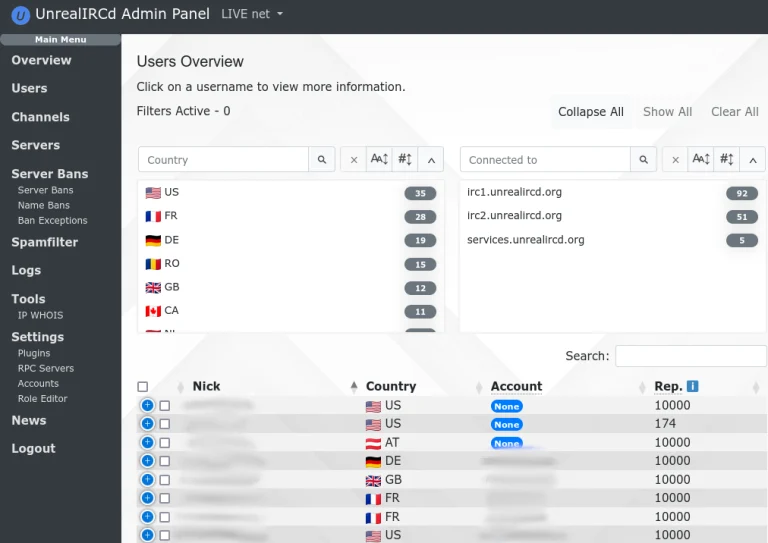
UnrealIRCd vulnerability CVE-2026-114713 is exploited in the wild, letting users run IRCOp commands. Hot-patch or upgrade to 6.2.7.1 now.
SolarWinds Dameware 2026.3.1 fixes Dameware command injection flaw CVE-2026-28336 (CVSS 9.9), plus a buffer overflow and DLL hijacking bug.
Patch two Barracuda vulnerabilities, CVE-2026-116606 and CVE-2026-111560, that allow attackers to gain Barracuda root access across multiple appliances.
CISA warns of nine Kiloview E3 vulnerabilities in the NDI encoder, including CVSS 9.9 flaws CVE-2026-107861 and CVE-2026-110243. Update to V1.30.
Six Apache CouchDB vulnerabilities, including CVSS 9.3 CVE-2026-86471, are fixed in 3.5.3. Retired Apache Cocoon gets four unpatched flaws.
Patch two high-severity SonicWall NSM On-Prem vulnerabilities (CVE-2026-96540, CVE-2026-100232) allowing admin privilege escalation and OS command RCE.
Attackers are actively exploiting CVE-2026-110447 (CVSS 9.2), a critical Nextcloud Collabora Online RCE flaw in richdocumentscode, to deploy PHP webshells.
Patch CVE-2026-110005 (CVSS 9.9), a critical Komodo Periphery vulnerability allowing authenticated users to run arbitrary OS commands as root on the host.
Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
Digi DAL OS vulnerability CVE-2026-75937 (CVSS 9.4) lets attackers run root commands on Digi Accelerated Linux devices. Patch now.
Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
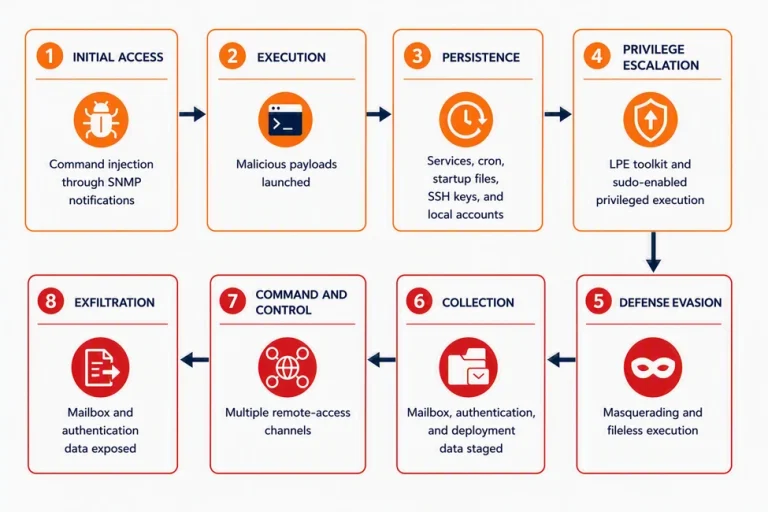
Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
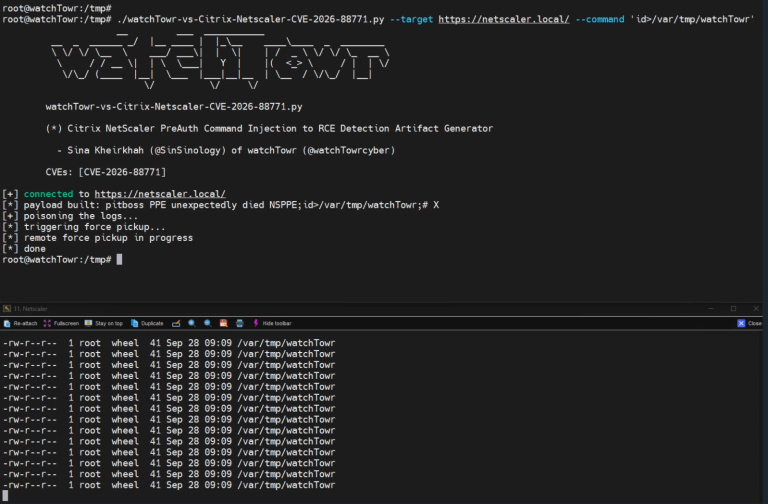
CVE-2026-88771 is a Citrix NetScaler command injection exploited in the wild. Details and a PoC are public. Patch NetScaler to 14.1-73.37 now.
Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately.