 Do Son
Attackers now target the Kemp LoadMaster RCE vulnerability (CVE-2026-8037) using a public PoC. Patch to 7.2.63.2 or 7.2.54.18 immediately.
Command Injection
A CVSS 8.7 TP-Link router command injection flaw allows unauthenticated remote code execution. Patch CVE-2026-11834 to stop this DHCP option vulnerability.
Mitel patched 12 critical MiCollab vulnerabilities, several at CVSS 10.0. Unauthenticated command injection and SQL injection flaws need urgent updates.
QNAP patched 14 NAS vulnerabilities in QTS, QuTS hero, and QVP, including command injection and credential-theft flaws. Update your QNAP NAS now.

A critical Fortra BoKS vulnerability (CVE-2026-9862) enables remote OS command injection via the autoregistration service. Mitigate now.
Three NVIDIA NeMo vulnerabilities (CVE-2026-24155, CVE-2026-24252, CVE-2026-24228) enable code execution. Update NeMo Framework to v2.7.3 now.
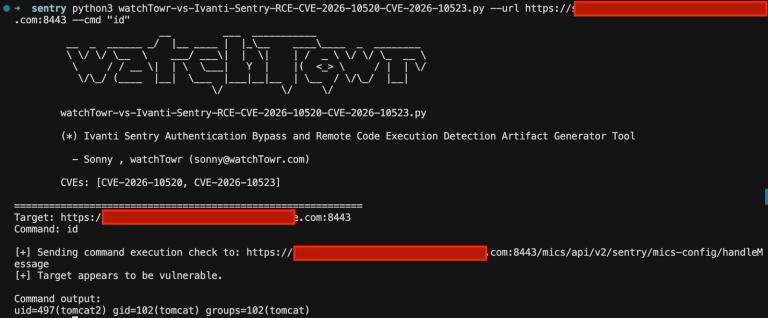
Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.
The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

New Ivanti EPMM security updates address high-severity flaws that could allow a remote authenticated attacker to achieve remote code execution.

An urgent patch fixes the critical CVE-2026-25089 FortiSandbox bug. Attackers can execute remote commands, so update your systems immediately.

A critical Archer MR600 command injection vulnerability surfaces within the WireGuard client configuration. Update your TP-Link firmware now.
A critical Cisco SD-WAN vulnerability is actively exploited in the wild. Learn how to inspect logs and secure your deployment immediately.
A dangerous Acer router flaw allows a critical authentication bypass. Install the latest firmware patch to secure your network now.
Severe InHand router flaws expose industrial networks to command injection vulnerabilities. Update your industrial firmware immediately to patch these bugs.

Multiple critical Rancher security flaws allow widespread cluster privilege escalation. Patch your Kubernetes container environments immediately.
A critical TP-Link router vulnerability affects Archer models. Download the latest CVE-2026-5509 patch immediately to secure your network environment.

CVE-2026-9277 (CVSS 9.2) lets attackers inject commands via the shell-quote npm package. Check your dependencies and upgrade now.
Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

Technical details and a functional Python PoC exploit have been released for CVE-2026-4802, a critical Cockpit flaw giving low-privilege users root.
Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

Critical Root RCE (CVE-2026-6644) hits ASUSTOR ADM. With PoC code now public, 19,000 NAS devices are at risk. Update to ADM 5.1.3.RGO1 immediately.