
 Do Son
Akamai SIRT warns of a new Mirai campaign weaponizing EOL D-Link routers via CVE-2025-29635. Protect your network from zombie botnets—retire old hardware now.
Command Injection

ASUSTOR issues an urgent fix for CVE-2026-6644, a critical 9.4 CVSS flaw in ADM's VPN client allowing full NAS takeover. Patch to ADM 5.1.3.RGL1 now.

Dolibarr ERP faces a critical 9.4 CVSS RCE flaw (CVE-2026-23500) in its PDF conversion logic. Unsanitized commands allow full system takeover. Upgrade to 23.0!

Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.

Python patches a critical 9.1 UAF flaw in decompressors and a browser command injection bypass. Protect your infrastructure—audit your CPython code today!
Ubiquiti fixes critical 9.8 CVSS RCE flaws in UniFi Play PowerAmp and Audio Port. Don't let attackers control your sound—update your firmware immediately.

TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!
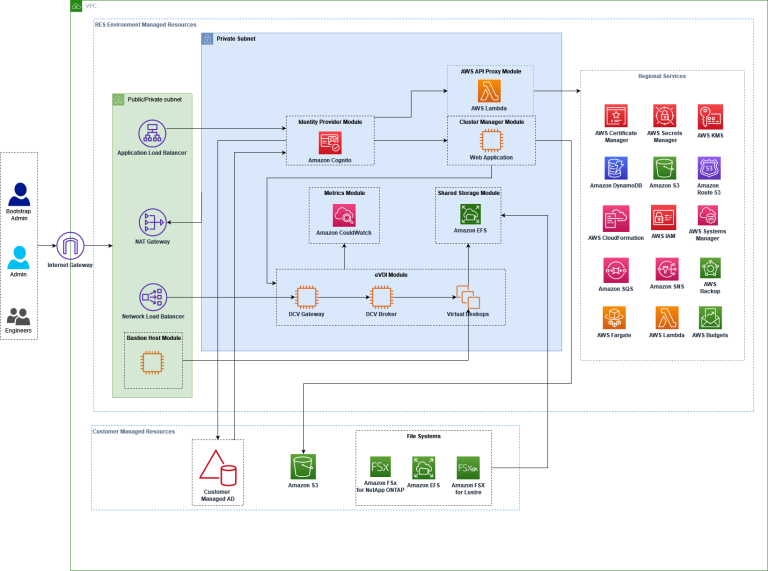
AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.
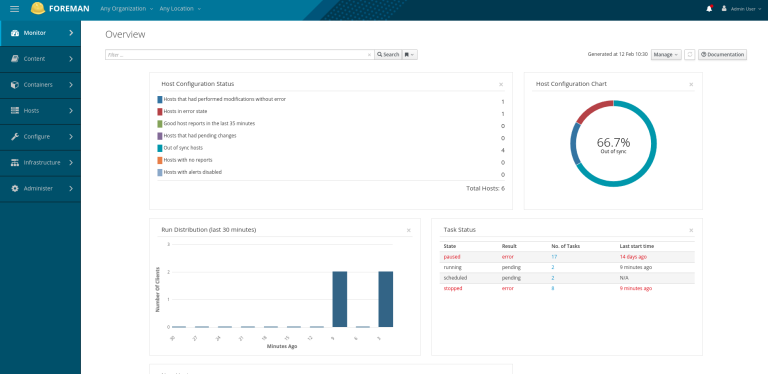
Foreman patches a critical 8.0 CVSS command injection flaw (CVE-2026-1961). Malicious hostnames can trigger RCE via WebSocket proxies. Update to 3.18.1 now!

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.

Critical flaws (CVE-2025-41709) in Janitza and Weidmueller energy meters allow remote code execution and full system takeover. Update to firmware 3.14 now.
A critical 8.5 CVSS command injection flaw (CVE-2025-15568) in TP-Link Archer AXE75 routers allows complete root-level network takeover. Patch immediately.

A critical 9.8 CVSS flaw (CVE-2026-29058) in AVideo-Encoder allows unauthenticated remote attackers to execute arbitrary system commands. Patch now.

An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.

OneUptime 10.0.7 patches a critical 10.0 CVSS vulnerability (CVE-2026-27728). Attackers can use traceroute probes to execute root commands and steal data.

NVIDIA warns of three high-severity vulnerabilities (CVE-2025-33179, 33180, 33181) in Cumulus Linux. Low-privileged users can escalate to admin control.
CISA warns of critical flaws (CVE-2025-29631) in Gardyn Home Kits allowing unauthenticated RCE and admin access. Update your app and firmware immediately!

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

Broadcom warns of a high-severity RCE flaw (CVE-2026-22719) in VMware Aria Operations. Attackers can execute commands during system migrations. Patch now!