 Do Son
Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
Confluence
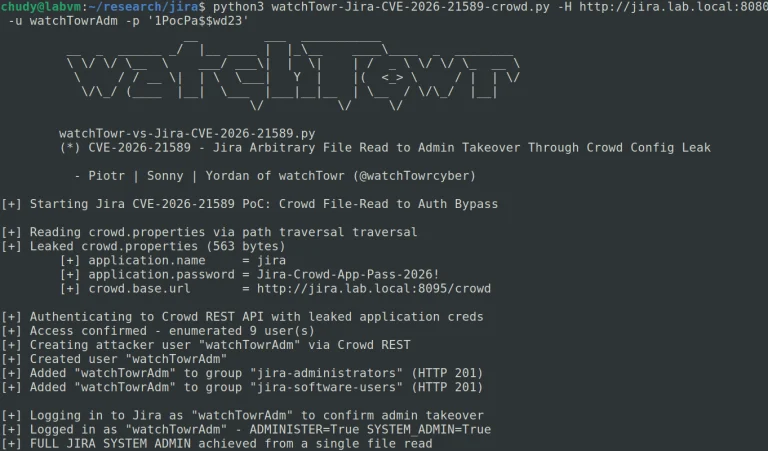
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.
A Confluence vulnerability, CVE-2026-21580, is a stored XSS flaw (CVSS 8.6) allowing unauthenticated attacks. A Jira flaw also patched. Update now.

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.
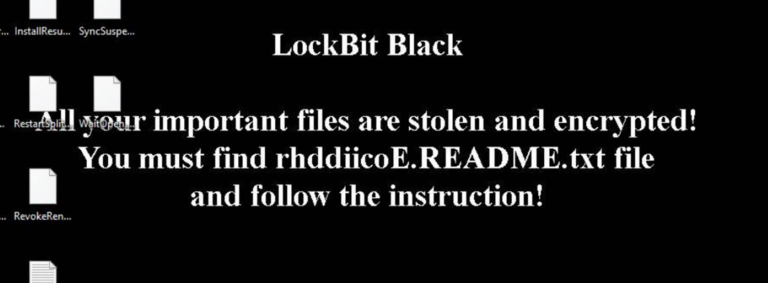
Uncover the details of the LockBit encryption attack using remote code execution vulnerabilities in Confluence. Learn more.

Learn about the critical vulnerability CVE-2023-22527 in Atlassian Confluence. Find out how attackers exploit the flaw for cryptocurrency mining.
CVE-2024-21687, and CVE-2024-21686 have the potential to compromise sensitive data and disrupt operations for organizations
At present, Ubisoft is reluctant to disclose detailed information about this data breach. Several days have elapsed since the incident