 Do Son
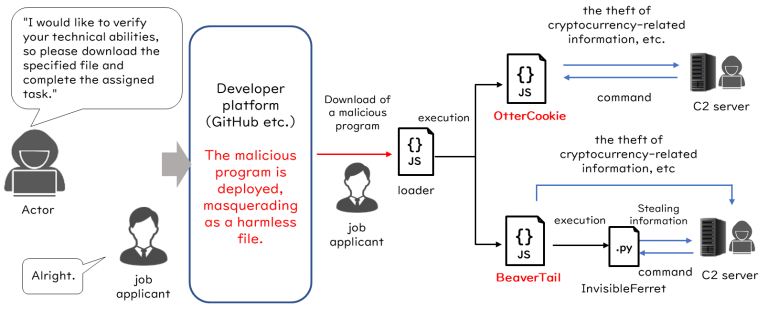
Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.
Contagious Interview
Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.
North Korean hackers are now targeting AI tools like Cursor and Claude. The OtterCookie malware steals API keys and conversation logs. Is your dev environment safe?
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.
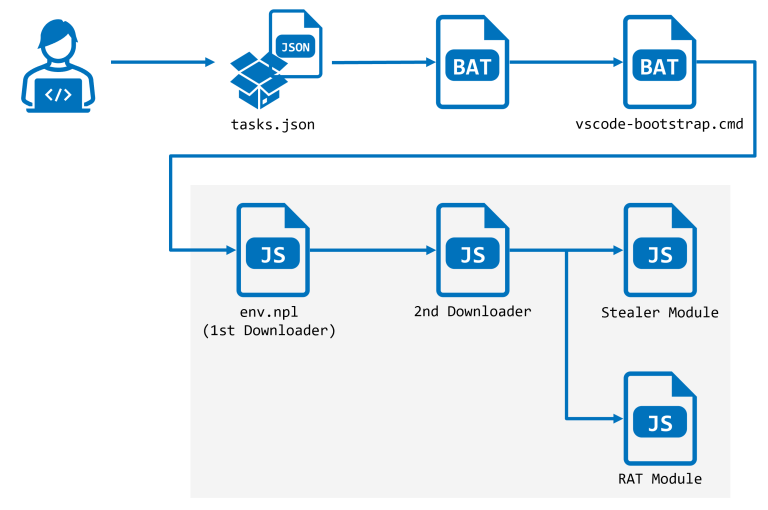
Researchers uncovered StoatWaffle, a new Node.js malware by North Korean hackers targeting developers via malicious VSCode repositories to steal data.
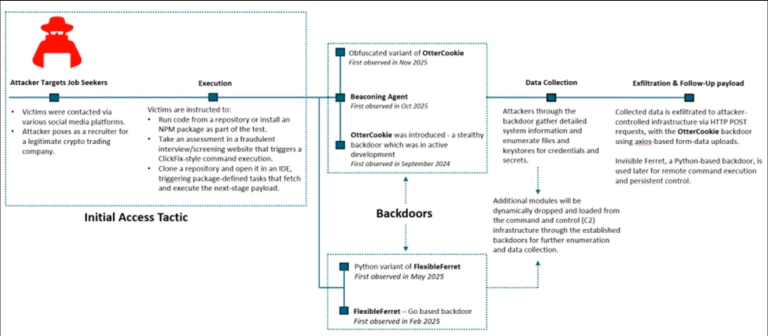
Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
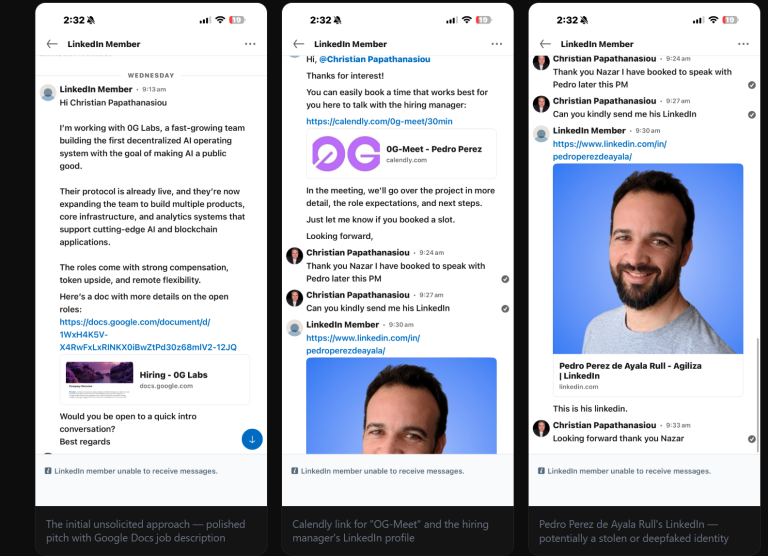
A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.

GitLab reveals how North Korean fake IT workers use 'Contagious Interview' scams to bypass hiring, steal data, and hijack executive digital identities.

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.
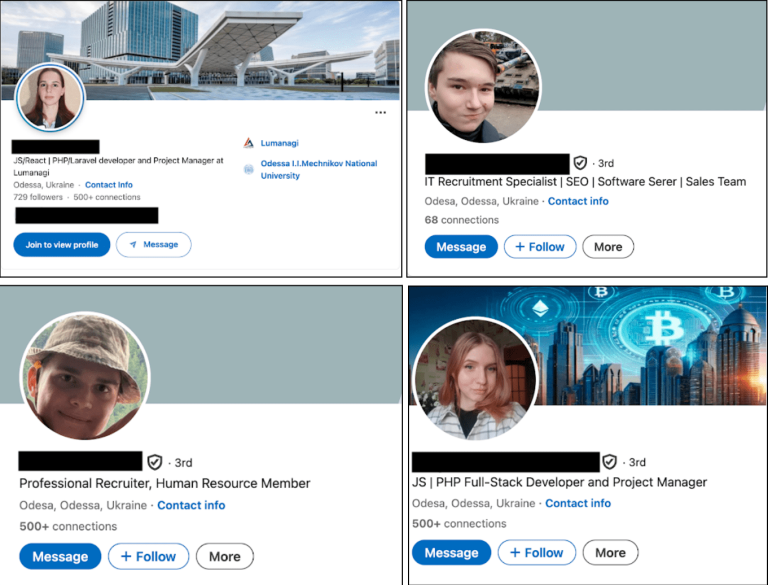
North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!
North Korean APTs added 197 malicious npm packages to the "Contagious Interview" campaign. The operation uses fake crypto job assignments to deploy the OtterCookie/BeaverTail hybrid to steal credentials cross-platform.
NVISO exposed the Contagious Interview APT using JSON Keeper and npoint.io as covert C2 channels. The North Korean group uses fake job lures on GitLab to deploy BeaverTail to steal Web3 credentials.
NTT exposed WaterPlum APT's multi-platform OtterCandy RAT (v2), which uses Node.js for remote control, targets 7 browser extensions, and now includes anti-forensic trace deletion.
North Korean actors launched "Contagious Interview," flooding npm with 338 malicious packages to deliver BeaverTail/InvisibleFerret. The campaign targets Web3 developers via fake job offers.

GitLab Threat Intelligence reveals a new North Korean malware campaign using "ClickFix" social engineering to target new industries like crypto and retail.

A new report reveals that the Lazarus Group is actively monitoring CTI platforms to evade detection and sustain a ClickFix phishing campaign against the cryptocurrency sector.