 Do Son
The Vite development server vulnerability CVE-2026-39364 is exploited in mass scanning for credential harvesting. F5 Labs logged 32,000 events. Patch now.
Credential Harvesting
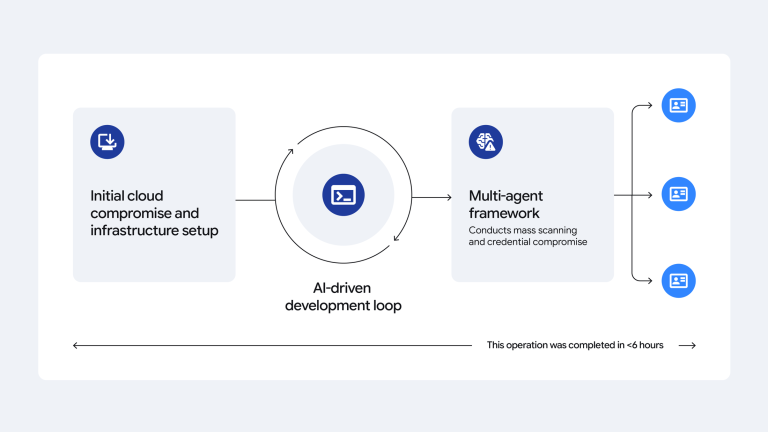
Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.

A sophisticated phishing campaign uses redirect chains to abuse Google infrastructure. Learn how attackers abuse Google infrastructure to steal credentials.

The leaked DarkSword iOS exploit now spreads across 100+ sites, dropping the GHOSTBLADE implant. Censys maps the operator panels. Update to iOS 26 now.

The GitBait phishing campaign abuses GitHub Pages and the SheetBest API to steal banking credentials from at least 12 Mexican financial institutions.
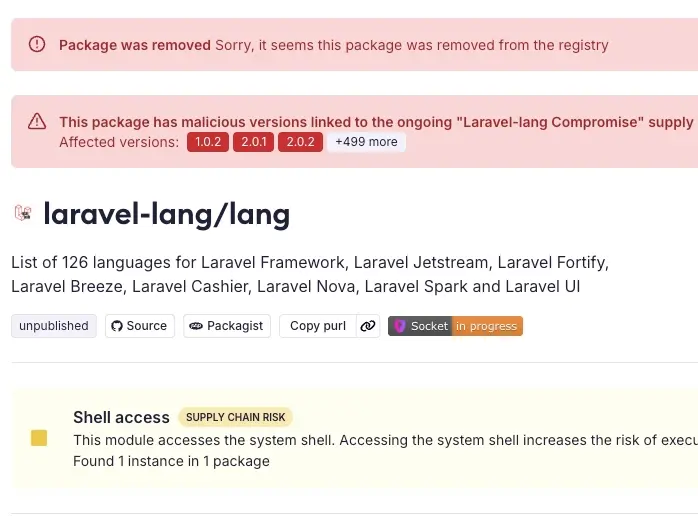
DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.

TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.
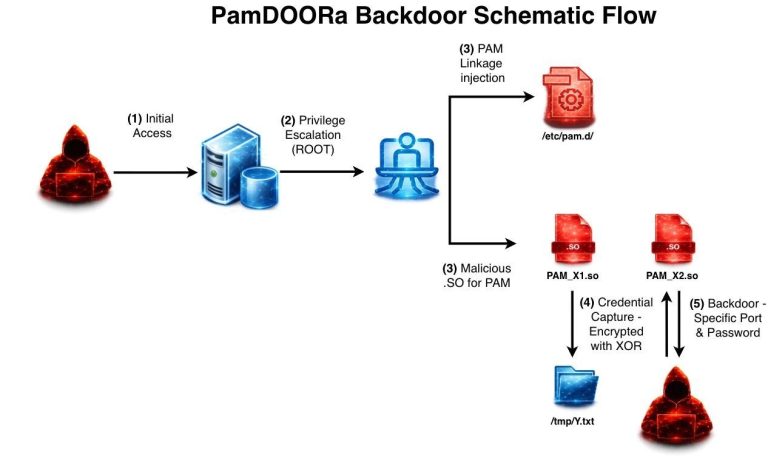
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.

Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.
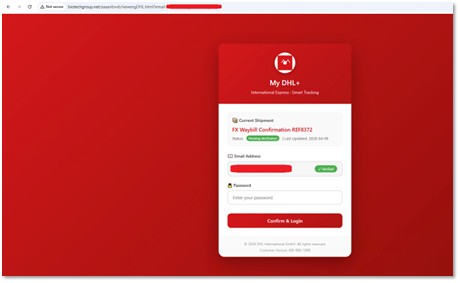
Forcepoint X-Labs uncovers a clever 11-step DHL phishing scam using a fake OTP interface to build trust and steal passwords. See how the trick works.
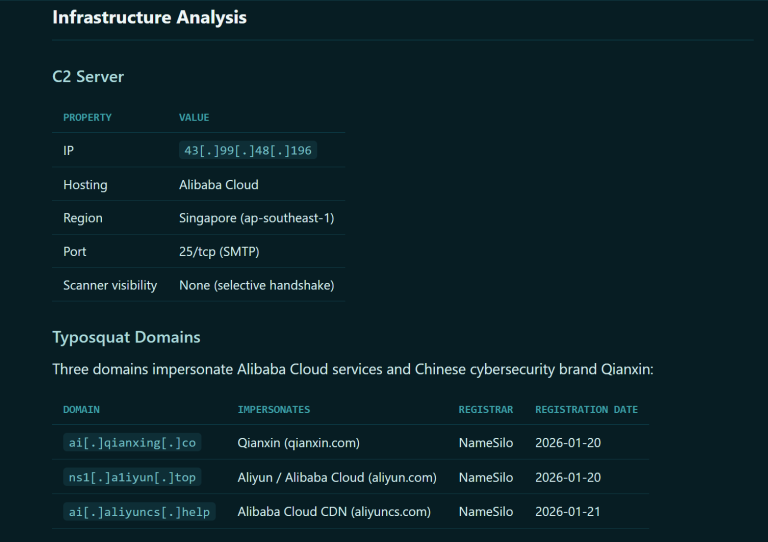
APT41's new zero-detection ELF backdoor uses SMTP (Port 25) to hijack Linux cloud workloads invisibly. Secure your credentials—audit your SMTP traffic today.

Cisco Talos exposes "Platform-as-a-Proxy" (PaaP). Hackers are abusing GitHub and Jira's trusted mail servers to bypass SPF/DKIM and deliver phishing lures.

HPE Aruba Networking patches a critical 8.8 CVSS open redirect in its Private 5G Core. Prevent credential harvesting—update to version 1.25.3.1 immediately.

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!
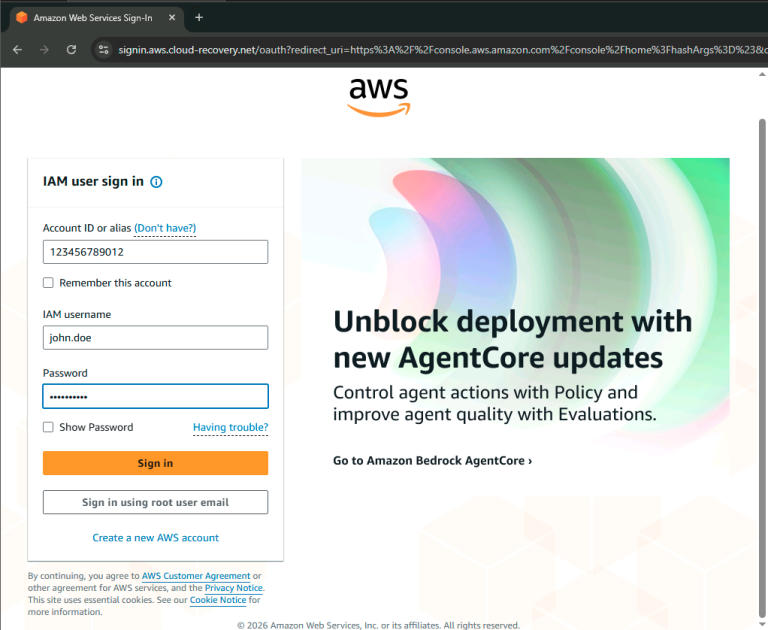
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.
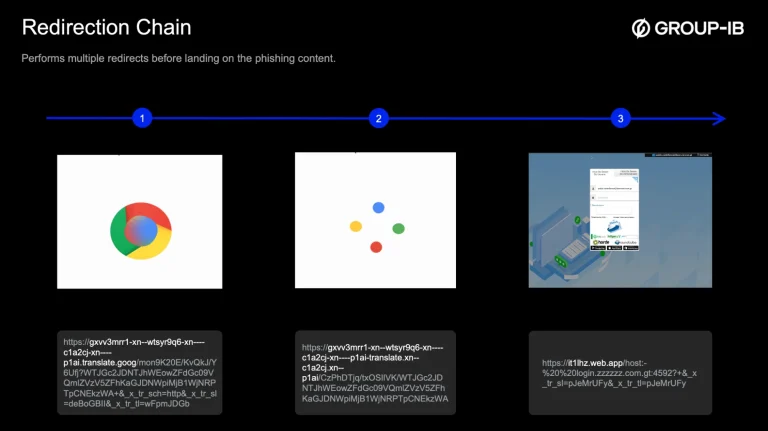
Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.

Sophisticated phishing abuses Vercel Blob & PDFs to bypass filters. Stolen credentials are exfiltrated via Telegram bots. Learn how to spot this attack.
Trellix warns: "Browser-in-the-Browser" phishing creates perfect fake Facebook login pop-ups. Learn how this invisible trap steals credentials.

Russian group BlueDelta targets energy researchers in Europe & Middle East. Learn how they abuse free web services for credential harvesting.

CVE-2025-67732 unmasks a high-severity flaw in Dify that exposes plaintext API keys to frontend users. Upgrade to v1.11.0 to secure your AI quotas.

A Russian APT is targeting Transnistria and NATO entities using blurred HTML attachments to harvest credentials. The 2025 campaign mimics official presidential decrees.

Socket’s Threat Research Team has uncovered a massive supply-chain abuse campaign leveraging npm’s public registry and unpkg.com’s...