
 Do Son
CERT Polska warns of a critical Roundcube XSS flaw (CVE-2024-42009) exploited by UNC1151 in spear phishing, stealing credentials and compromising Polish organizations.
Credential Theft

UNC6040 is using sophisticated vishing to breach Salesforce, tricking employees into granting access, exfiltrating data, and then pivoting to other cloud platforms.

Haozi, a Chinese Phishing-as-a-Service platform, is back, offering no-code phishing kits and full support. Learn how this service enables easy cybercrime.

Learn how interactive sandboxes like ANY.RUN can detect and analyze Microsoft 365 phishing attacks in real-time, preventing silent breaches and data exfiltration.
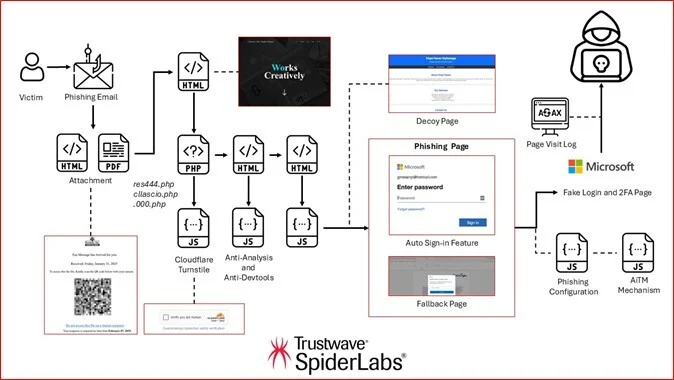
Trustwave uncovers Dadsec and Tycoon2FA, new Phishing-as-a-Service kits bypassing MFA to target Microsoft 365 users with advanced AiTM tactics.

The notorious Genesis Market is back! A new campaign deploys a malicious browser extension via Lumma Stealer to covertly harvest user data.

Learn about critical vulnerabilities in LLM-powered Browse agents like Browser Use, allowing domain bypass and prompt injection for data theft.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

Hackers exploited GovDelivery to send fake TxTag toll emails via Indiana government accounts. Learn how the phishing scam unfolded and how to stay protected.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

ThreatLabz reveals StealC V2—an evolving info-stealer with encrypted C2, MSI and PowerShell payloads, and a rule-driven control panel for targeted attacks.

Darktrace uncovers a SocGholish campaign using obfuscated loaders and legacy Windows exploits to harvest NTLM hashes and deliver ransomware payloads.

DFIR Report exposes the Fog ransomware group's sophisticated use of SonicWall exploits, Sliver C2, and credential theft across tech, retail, and education sectors.

Cisco Talos uncovers ToyMaker's IAB activity, paving the way for Cactus ransomware. Learn how LAGTOY backdoor & credential theft led to a major breach.
Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.

Hunt.io reveals a server-side phishing campaign that evades detection to steal employee credentials, bypassing 2FA.
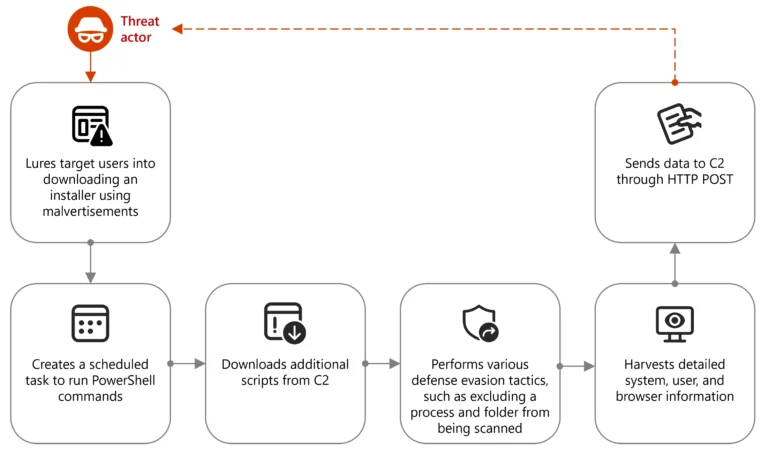
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

Phishing attacks using SVG files surged 1800%, exploiting JavaScript and PhaaS kits to bypass MFA and steal credentials, Trustwave warns.

Learn about Precision-Validated Phishing, a sophisticated technique where attackers use real-time email validation to target specific users, making credential theft more effective and harder to detect.

Learn about the ISP Infostealer Campaign and its severe impacts on ISP infrastructure through brute force and data exfiltration.