 Do Son
cPGuard supply chain attack: an update channel compromise pushed a backdoor in versions 5.88.12-5.88.19. Update to 5.88.25 and rotate credentials.
Credential Theft
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
Two Ivanti critical vulnerabilities rated CVSS 9.9 in Neurons Patch for Intune and Xtraction risk credential theft. Update Xtraction and rotate secrets.
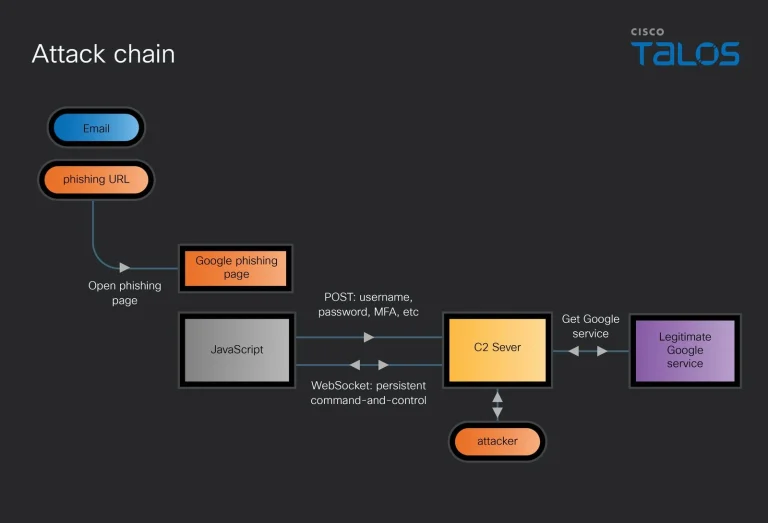
UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA.
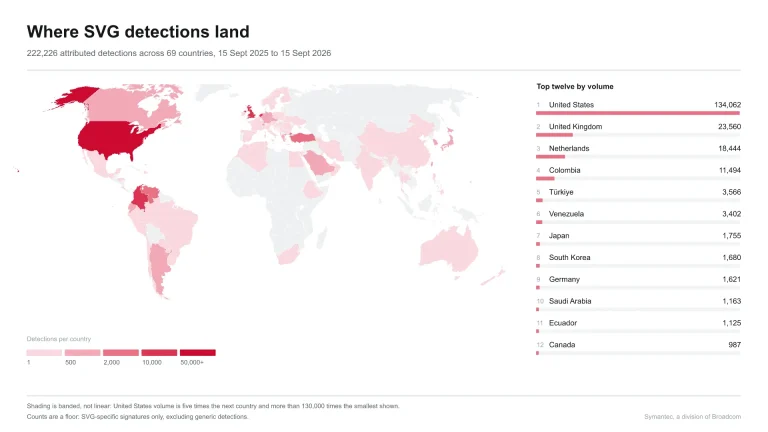
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
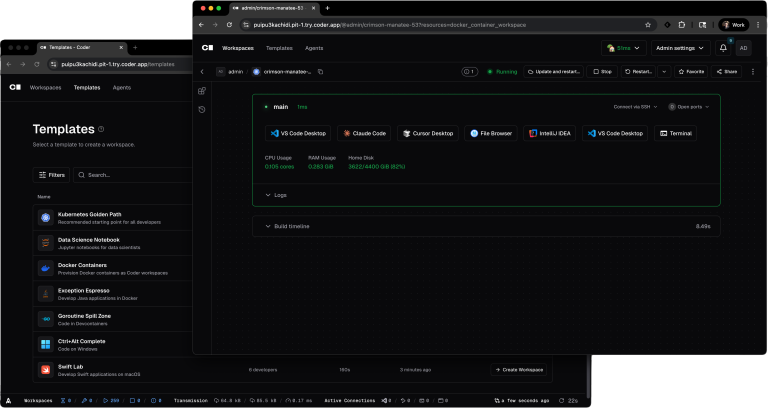
The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
Expel analyzed the SynkLoader malware attack chain. Discover how SynkLoader malware uses Teams phishing and fake lock screens to steal credentials.
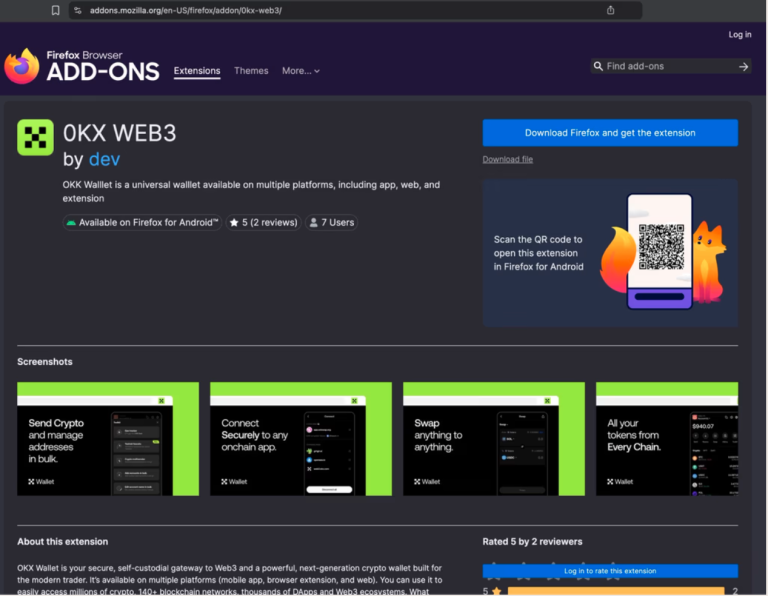
Socket tracked 77 malicious Firefox extensions that steal crypto wallet secrets and credentials. See how the Offside Wallet Theft Factory works.

CaptiveCrunch malware campaign hijacks hotel Wi-Fi captive portals worldwide. Microsoft ties Storm-2945 to Midnight Blizzard, Russia SVR-linked group.

A pgAdmin 4 RCE flaw, CVE-2026-17566, lets attackers run OS commands via psql. Two more critical bugs also got fixed in version 9.17.

A critical Veeam Service Provider Console flaw lets attackers steal agent credentials, while a second enables remote code execution. Update to 9.3 now.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.

A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.

The Hugging Face breach was driven end-to-end by an autonomous AI agent attack. Internal datasets and service credentials were exposed.

A CrySome RAT phishing attack used a fake freight rate confirmation to bypass AMSI, disable Defender, and steal browser credentials on Windows.
A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.
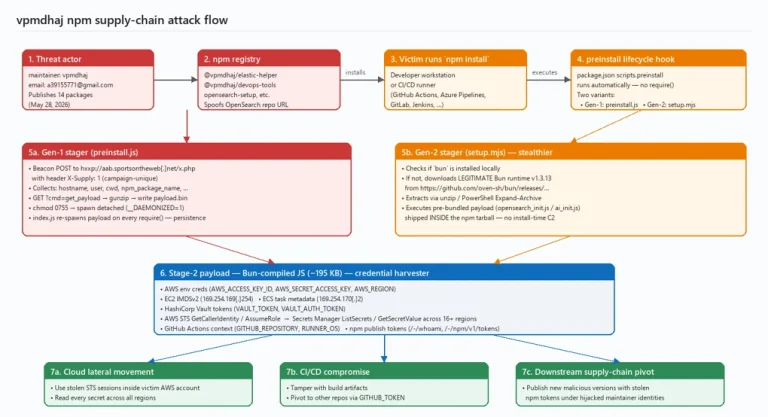
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.
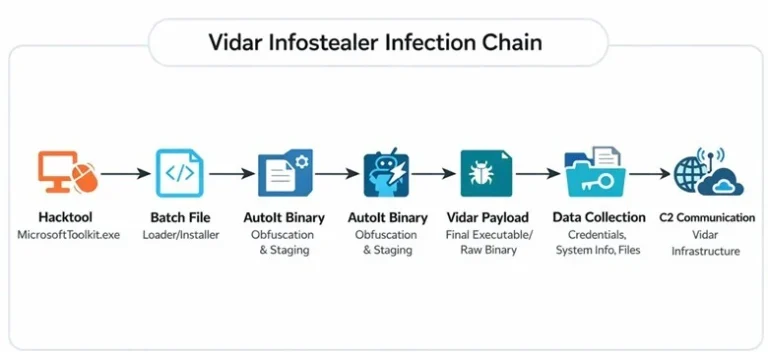
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?
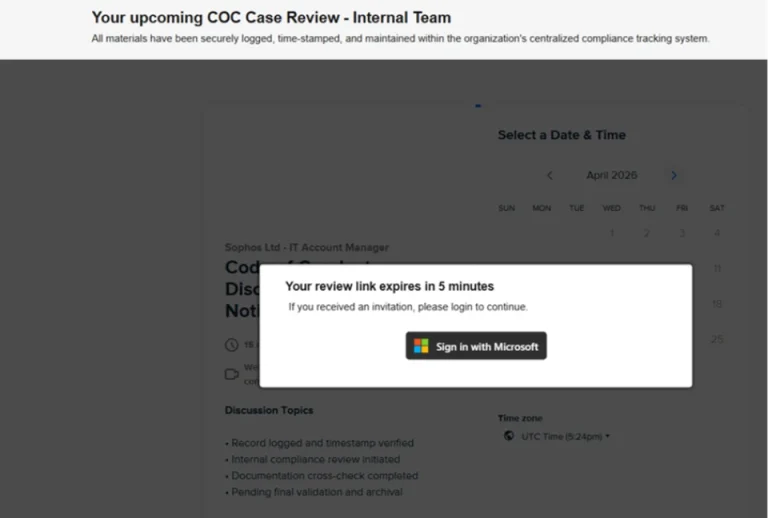
Microsoft warns of a massive AiTM phishing campaign targeting 13,000+ orgs. Using fake disciplinary lures, attackers bypass MFA to hijack active sessions.

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.