
 Do Son
Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.
Credential Theft
Meta Description (152 Characters)Securonix uncovers Deep#Door: a self-contained Python RAT that uses TCP tunneling and obfuscated scripts to bypass traditional defense. Secure your systems now.
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.

Cursor AI editor found storing API keys and tokens in an unprotected SQLite database, allowing extensions to steal credentials silently. CVSS 8.2. No patch yet.
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.
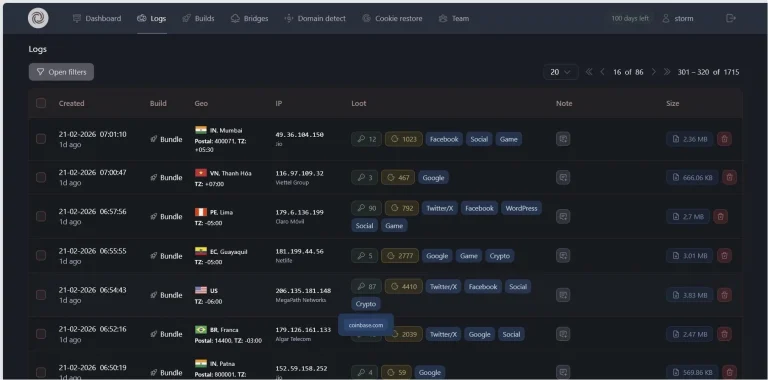
Storm malware bypasses Chrome security by shipping encrypted files for server-side decryption. Learn how it steals session cookies to defeat MFA in 2026.
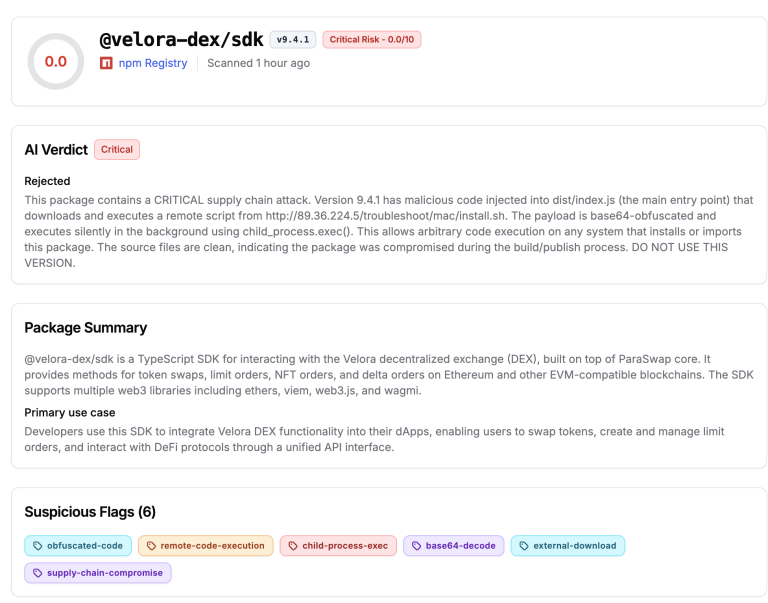
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.

Microsoft Defender Experts warn of Storm-2561 using SEO poisoning to distribute fake enterprise VPN clients like Pulse Secure, stealing user credentials.

Once a "Featured" tool, the ShotBird extension now delivers malware via "vibecoded" scripts and fake updates. Remove it now to protect your passwords and data.

Law enforcement from 14 countries just seized LeakBase.ws. With 142k accounts and 215k messages exposed, the DOJ sends a clear message: No hacker is anonymous.

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.

Ivanti patches critical EPM flaw CVE-2026-1603 allowing remote unauthenticated attackers to steal credentials. Update to 2024 SU5 immediately.

Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

A sophisticated new phishing campaign is targeting employees where they are most vulnerable—their paychecks—by leveraging QR codes...

iVerify exposes Cellik, a $150/mo Android RAT that wraps malicious code inside Play Store apps to grant attackers total device control.