 Do Son
CrowdStrike links the ARTEX AI tool to breaches at South Korean banks, run by a suspected Chinese-speaking, profit-driven attacker.
CrowdStrike
Europol and CrowdStrike disrupted the Sality botnet, a 20-year P2P network, using a peer-to-peer sinkhole to cut its operator off from infected machines.
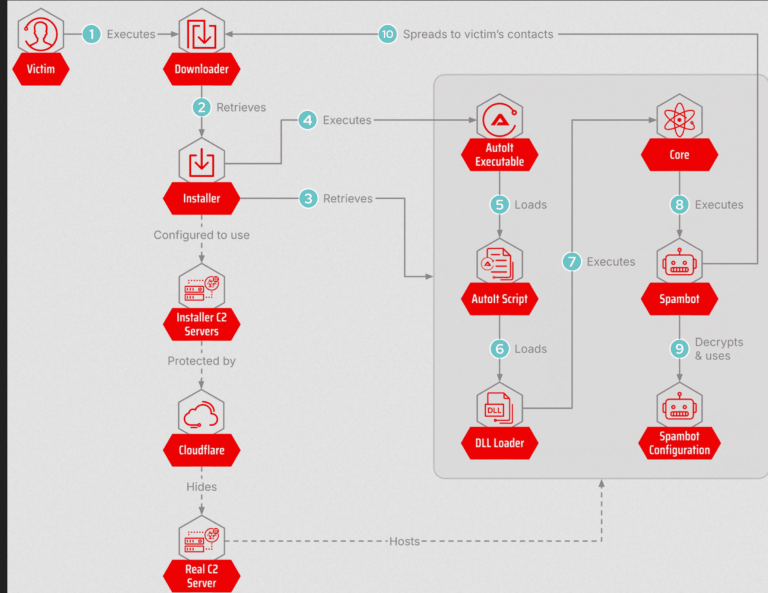
Astaroth's new WhatsApp spambot auto-messages every victim contact in Brazil using a hidden browser, quietly turning each victim into a malware distributor.
Discover how new prompt injection attacks threaten AI security. Hackers use prompt injection techniques to manipulate AI agents and bypass safety controls.

CrowdStrike reveals a critical 9.8 CVSS flaw in LogScale Self-Hosted. Unauthenticated attackers can read arbitrary server files. Patch to v1.235.1+ now!

Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.

Following major crashes, Microsoft will phase out OEM kernel-level driver privileges, forcing a shift to native drivers or user mode to prevent system-wide operating system failures.
CrowdStrike patched two flaws in Falcon Sensor for Windows (CVE-2025-42701). Attackers with local code execution can delete arbitrary files, risking system stability.

CrowdStrike warns that the Critical RCE zero-day (CVE-2025-61882) in Oracle E-Business Suite is being actively exploited by GRACEFUL SPIDER (Clop affiliate) for corporate data theft. Patch immediately.

A new worm, Shai-Hulud, has compromised CrowdStrike’s NPM packages. The malware steals credentials and can spread rapidly across the developer ecosystem.
The Shai-Hulud supply chain attack has compromised multiple CrowdStrike npm packages, injecting malware to steal credentials and data.

SCATTERED SPIDER targets U.S. airlines with ransomware, vishing, and VMware exploits—CrowdStrike warns of a rising threat across cloud identities.

Following the 2024 CrowdStrike BSOD incident, Microsoft's Windows Resiliency Initiative is moving security drivers out of the kernel into user mode to boost system stability.
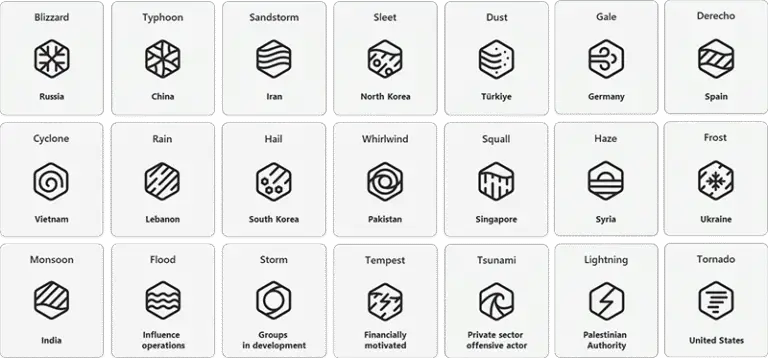
Microsoft, Google, and major cybersecurity firms are collaborating to unify hacker group naming, aiming for clearer threat intelligence across the industry.
Learn about CVE 2025-1146, a critical TLS vulnerability in CrowdStrike's Falcon Sensor that allows man-in-the-middle attacks.

Learn about the recent CrowdStrike phishing campaign that distributed the XMRig cryptominer through deceptive recruitment tactics.
Windows Endpoint Security Summit: Microsoft and CrowdStrike Unite to Protect Critical Infrastructure

Windows Endpoint Security Summit: Microsoft and CrowdStrike Unite to Protect Critical Infrastructure
Discover key insights from the CrowdStrike incident and the Windows Endpoint Security Ecosystem Summit. Learn about industry-wide measures to enhance security.

Learn about the recent cyber attack by Handala Hacking Team on Israeli targets and the significance of this intriguing incident.

Uncover the story behind Delta Air Lines' lawsuit against CrowdStrike and Microsoft. Discover how a software update impacted their operations and resulted in massive financial losses.

Learn about the staggering financial fallout of the CrowdStrike downtime. Fortune 500 companies report a direct loss of $5.4 billion.

CrowdStrike has not publicly responded to the alleged data leak. If the data is legitimate, the consequences could be severe