 Do Son
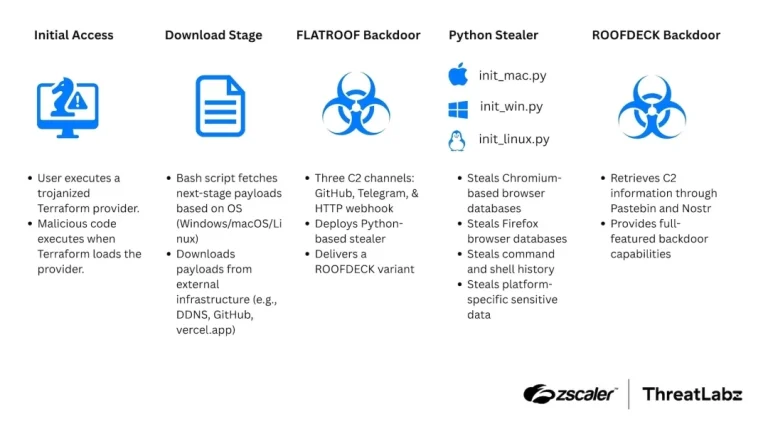
Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
Cryptocurrency Theft
A ClickFix browser attack uses Google Sheets C2 to inject a crypto web skimmer into Chrome. See how Cisco Talos traced the theft.

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.
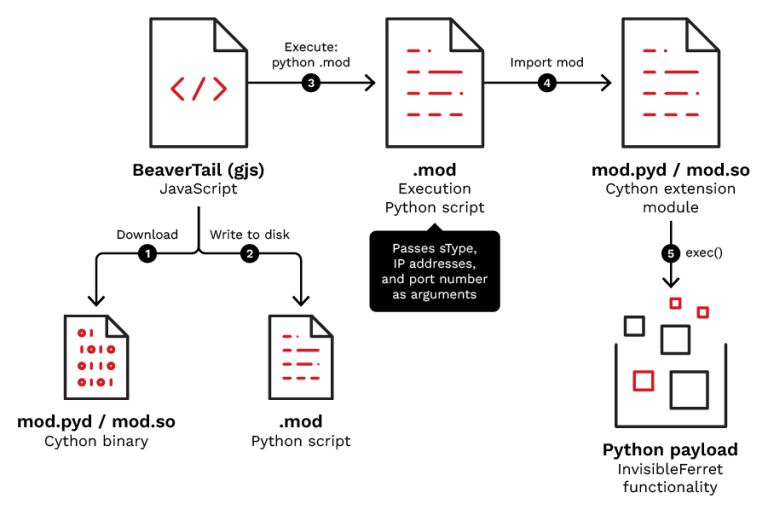
TrendAI Research exposes the new Void Dokkaebi Cython malware campaign. Learn how InvisibleFerret uses binary compilation to evade security teams.
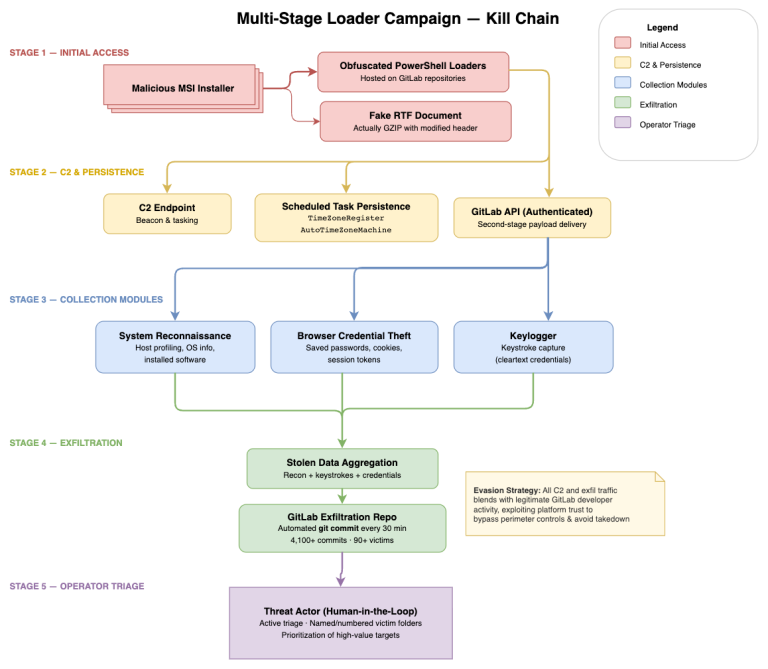
Velvet Chollima leaks its own backend infrastructure keys inside a malicious "Tralert FX" installer signed with a valid EV certificate.

Tyler Buchanan pleads guilty in US court for an $8M cyber heist. Discover how SMS phishing and SIM swapping bypassed 2FA to drain corporate & crypto assets.
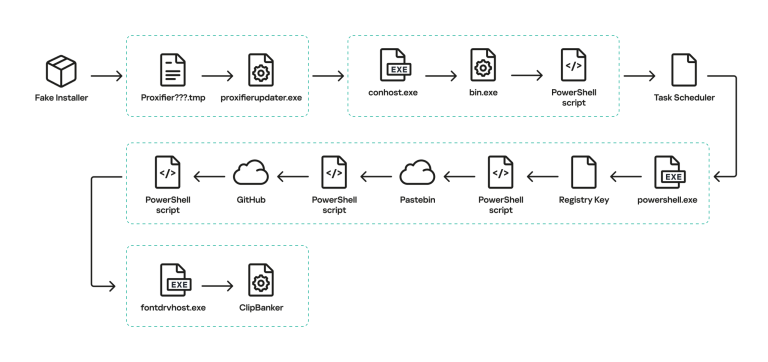
Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.
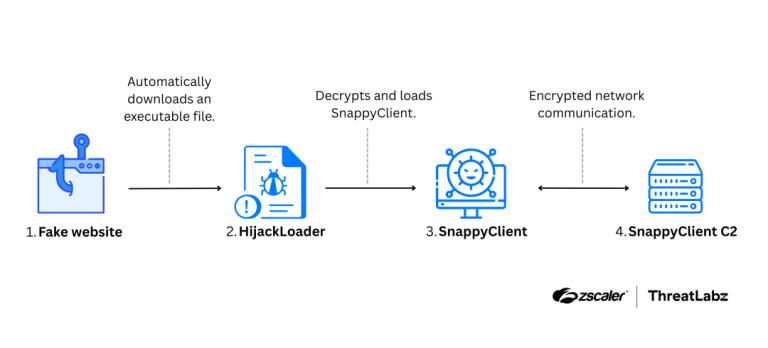
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.
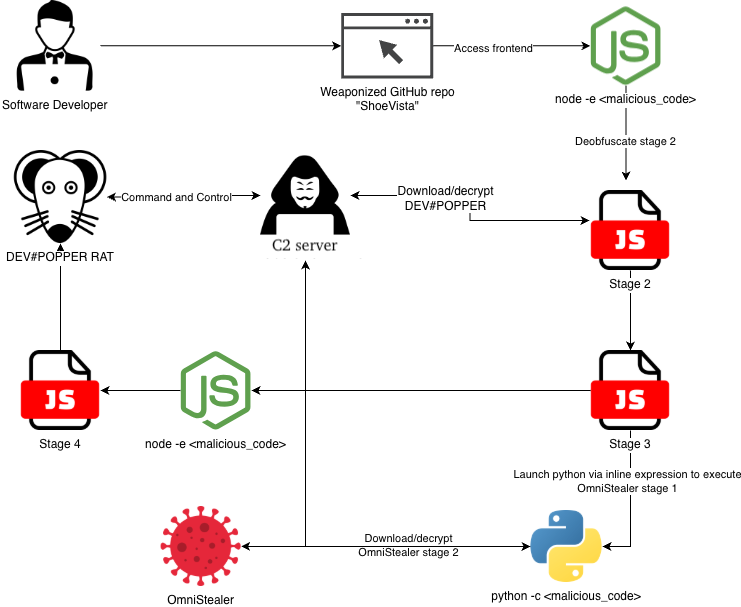
eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.
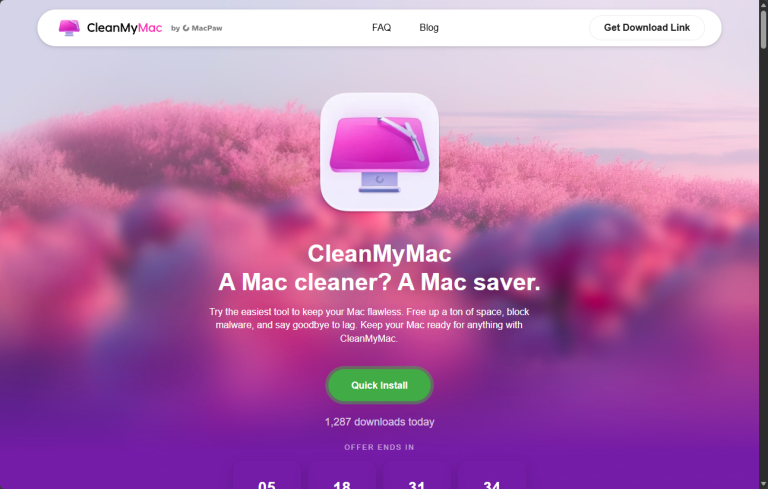
A fake CleanMyMac website is using ClickFix tactics to trick macOS users into installing SHub Stealer, a potent malware targeting passwords and crypto.
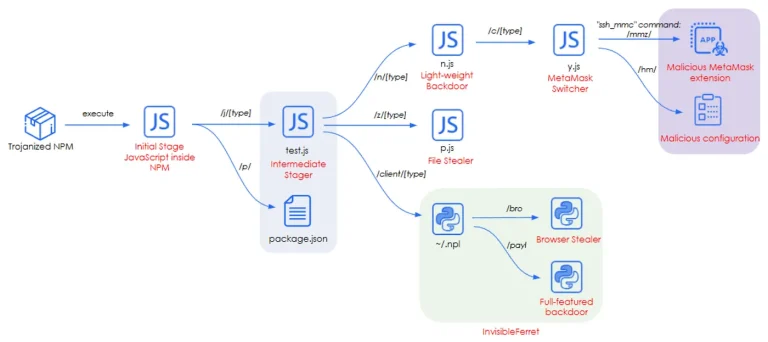
North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.
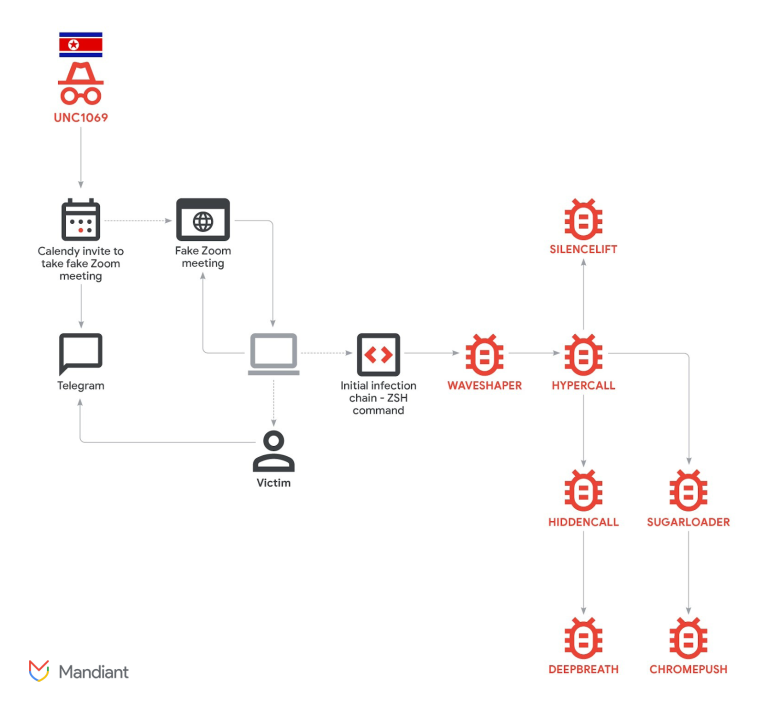
North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.

Zscaler detects NodeCordRAT, a new malware in malicious npm packages. It uses Discord as a C2 server to loot crypto wallets and Chrome data.

ASEC warns of EtherRAT, a multi-stage crypto-stealer exploiting the React2Shell flaw. It uses Node.js and Ethereum for stealthy C2. Patch now!

ReversingLabs uncovered Nethereum.All, a malicious NuGet package with 10M+ fake downloads designed to drain crypto wallets and steal API secrets.

A new macOS stealer (Nova) uses LaunchAgents to install a modular backdoor. Its main function is replacing legitimate Ledger/Trezor apps with phishing clones that exfiltrate seed phrases as users type.

Australia imposed sanctions and travel bans on four entities and one individual for engaging in cybercrime to fund North Korea's WMD and missile programs. The regime stole $1.9B in crypto in 2024.

Datadog exposed MUT-4831, a cluster that deployed Vidar Infostealer via 17 malicious npm packages. The malware uses postinstall scripts to download and execute the payload, stealing credentials and crypto wallets.

Koi Security exposed GlassWorm, the first VSCode worm that spreads autonomously, using invisible Unicode to hide malicious code. It uses Solana blockchain and Google Calendar for a resilient C2.