
 Do Son
CloudFlare had mitigated thousands of volumetric HTTP Distributed DDoS attacks that exploited the disclosed vulnerability known as HTTP/2 Rapid Reset
CVE-2023-44487
Alarmingly, this vulnerability is already being exploited in the wild. All HTTP/2 server users in active release lines 18.x and 20.x are susceptible.

CISA has added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation in the wild
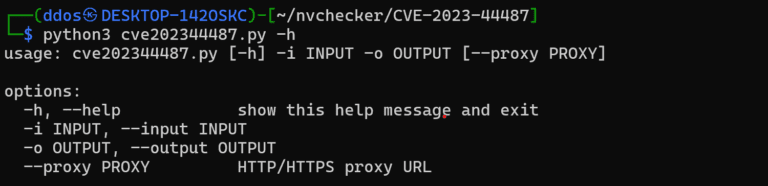
Basic vulnerability scanning to see if web servers may be vulnerable to CVE-2023-44487. The tool checks if a web server accepts HTTP/2 requests

In one audacious instance, an attacker dispatched an astonishing 398 million requests within a singular second

One of the Message Queuing vulnerabilities that was patched in October Patch Tuesday (CVE-2023-35349) has a CVSS severity score of 9.8/10

Leading internet giants, Cloudflare, Google, and Amazon AWS, have announced the discovery of a zero-day flaw, the "HTTP/2 Rapid Reset" attack