 Do Son
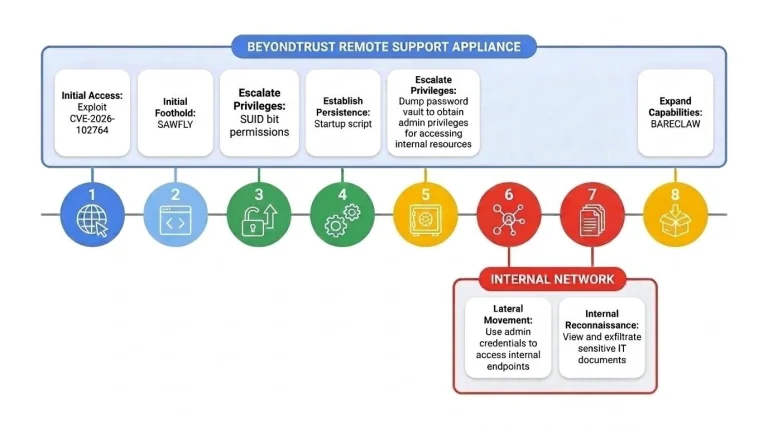
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
CVE-2023-46805
The malware file named “.redtail” confirmed the presence of the RedTail cryptominer, previously reported by Cyber Security Associates (CSA)

Attackers are weaponizing two critical vulnerabilities, CVE-2023-46805 and CVE-2024-21887, to spread the notorious Mirai botnet malware

The attackers then deployed a Perl-based web shell, dubbed ROOTROT, which is linked to the China-based hacking group UNC5221

Magnet Goblin is a financially motivated threat actor demonstrating proficiency in swiftly exploiting 1-day software vulnerabilities

Security researchers from NVISO have uncovered two sophisticated TLS-based backdoors, dubbed SparkCockpit and SparkTar

QuoIntelligence has uncovered a previously unknown and undetected variant of the WIREFIRE web shell, a Python-based implant

A key discovery in Volexity's investigation was the GIFTEDVISITOR webshell. Over 1,700 compromised Ivanti Connect Secure VPN devices

Ivanti has revealed two critical zero-day vulnerabilities (CVE-2024-21887, CVE-2023-46805) in its Connect Secure and Policy Secure products