 Do Son
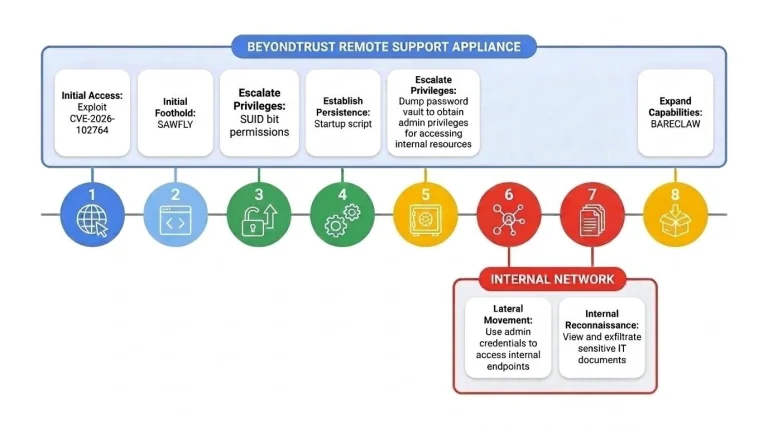
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
CVE-2024-21887
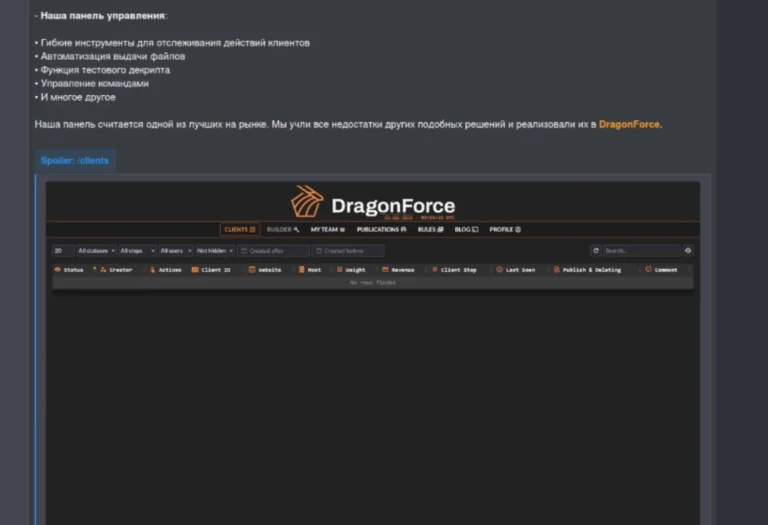
DragonForce ransomware cartel targets UK retailers with Conti-based payloads, RansomBay leaks, and phishing attacks, warns SentinelOne report.

Learn about the DragonForce ransomware group's first major attack in Saudi Arabia, exposing 6 TB of sensitive data.

Learn about the Earth Estries APT group, a significant cyber espionage actor targeting critical sectors and industries worldwide.
The malware file named “.redtail” confirmed the presence of the RedTail cryptominer, previously reported by Cyber Security Associates (CSA)

Attackers are weaponizing two critical vulnerabilities, CVE-2023-46805 and CVE-2024-21887, to spread the notorious Mirai botnet malware

The attackers then deployed a Perl-based web shell, dubbed ROOTROT, which is linked to the China-based hacking group UNC5221

Security researchers from NVISO have uncovered two sophisticated TLS-based backdoors, dubbed SparkCockpit and SparkTar

A key discovery in Volexity's investigation was the GIFTEDVISITOR webshell. Over 1,700 compromised Ivanti Connect Secure VPN devices

Ivanti has revealed two critical zero-day vulnerabilities (CVE-2024-21887, CVE-2023-46805) in its Connect Secure and Policy Secure products