 Do Son
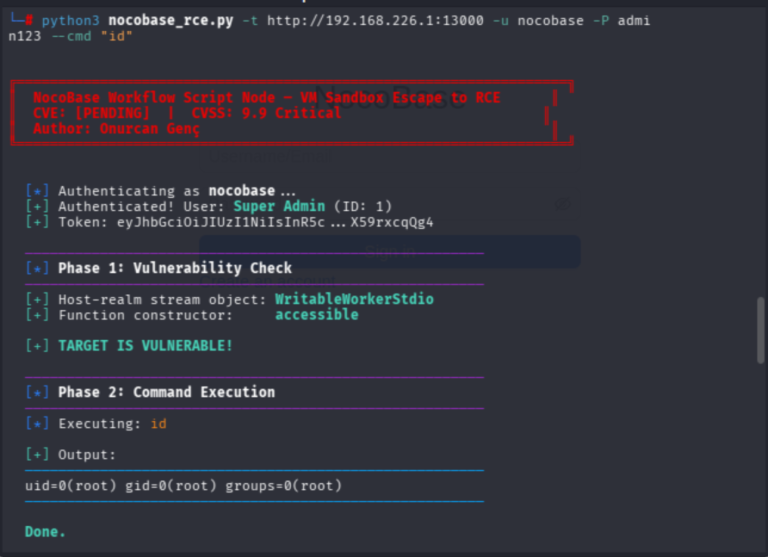
NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!
CVSS 10
A critical 10.0 CVSS logic flaw in File Browser (CVE-2026-32760) grants unauthenticated users automatic admin rights upon signup. Update to 2.62.0 now.
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.

Winter CMS urgently patches a critical 10.0 CVSS privilege escalation flaw (CVE-2026-27591) allowing low-level backend users to gain full system control.

HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!

CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.

Oracle patches CVE-2026-21962 (CVSS 10) in Fusion Middleware. This critical flaw allows unauthenticated server takeover. Update immediately.

Critical Cal.com flaw (CVE-2026-23478) allows full account takeover via a single API call. CVSS 10.0. Update self-hosted instances to v6.0.7 immediately.

Urgent: Siemens Edge flaw CVE-2025-40805 (CVSS 10) allows remote account takeover. Update SIMATIC & IOT2050 devices immediately to secure ops.

Urgent! DNN Platform has a Critical CVSS 10.0 flaw allowing unauthenticated users to overwrite files, leading to site defacement & XSS. Update to 10.1.1.

Arista patches CVE-2025-0505, a CVSS 10 flaw in CloudVision ZTP that allows admin privilege escalation—on-premise users urged to upgrade.

Critical CVE-2024-11186 in Arista CloudVision Portal allows authenticated users broader network actions. Patch or mitigate now.

Microsoft patched critical Azure & Power Apps security flaws before exploitation. No user action needed. Stay informed on cloud security.

CVE-2025-32433 in Erlang/OTP SSH server enables unauthenticated RCE. Patch now to prevent full system compromise across all affected versions.