
 Do Son
Progress patched a critical Chef Automate vulnerability tracked as CVE-2026-80462. Fix this Chef Automate vulnerability to stop DevOps account takeovers.
CVSS 10

GitLab patched critical GitLab vulnerabilities, led by CVE-2026-85706 with a CVSS 10.0 score. Update your server now to protect source code from exposure.
ServiceNow patched CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820, code injection and SQL injection flaws rated CVSS 10, plus a CVSS 8.7 bug.
A critical Veeam ONE vulnerability, CVE-2026-64633, allows remote unauthenticated code execution at CVSS 10.0. Update to build 13.1.0.7034 now.
Eleven Adobe ColdFusion vulnerabilities include six CVSS 10 arbitrary code execution flaws. Patch ColdFusion 2025 and 2023 now.
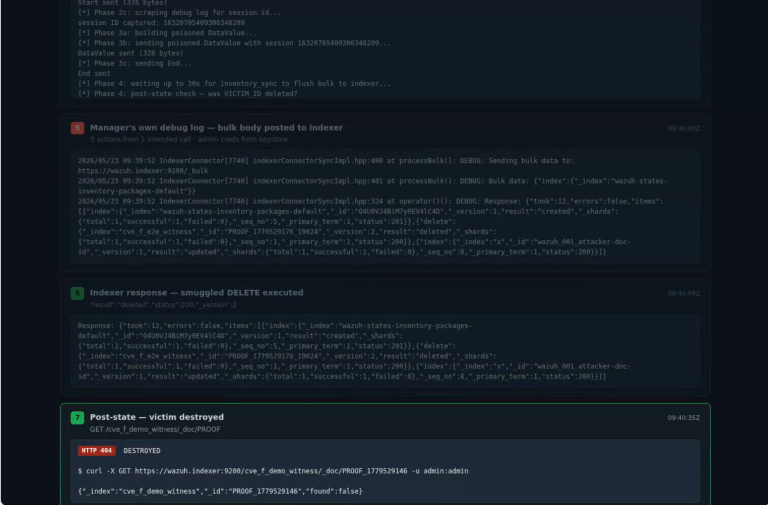
Public details and PoC exploit code expose a critical Wazuh CVSS 10 vulnerability allowing attackers to smuggle OpenSearch bulk operations.
Read about new Jupyter Gateway vulnerabilities and critical CVSS 10 flaws that allow remote code execution and full Kubernetes cluster takeover.
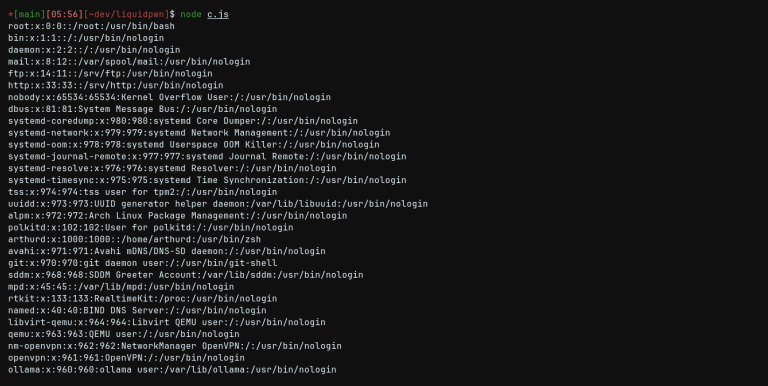
A maximum-severity Liquidjs remote code execution flaw impacts millions. Learn about this template engine vulnerability and update now.
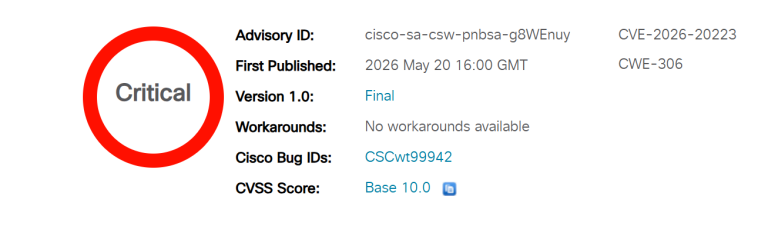
Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.
Quest KACE SMA CVE-2025-32975 (CVSS 10) exploited in the wild. Attackers bypass auth to seize admin control. Patch to version 14.1.101 or 14.0.341 now!
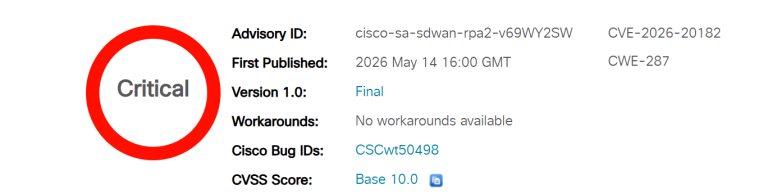
Cisco Catalyst SD-WAN CVE-2026-20182 (CVSS 10) exploited in the wild. Attackers bypassing auth to seize admin control. Upgrade your network fabric now!
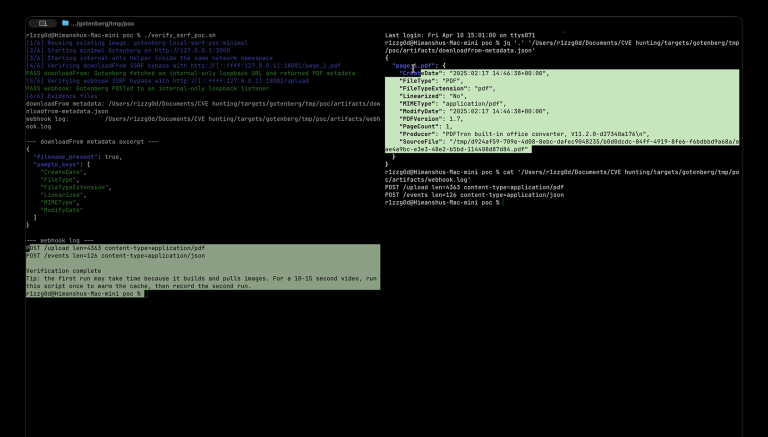
Gotenberg PDF API hit with a rare CVSS 10 flaw. Unauthenticated RCE, file overwrites, and SSRF bypasses discovered. Upgrade to version 8.32 immediately.
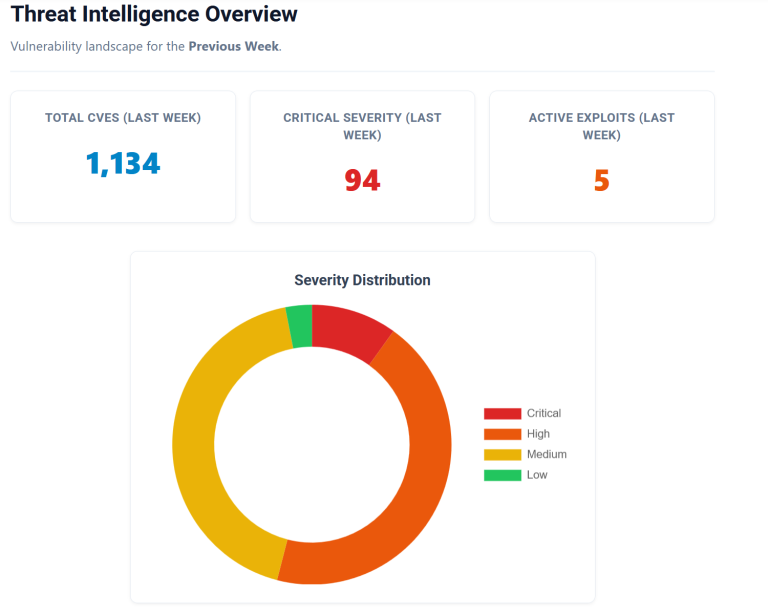
Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.
Critical CVSS 10 update for Gemini CLI (@google/gemini-cli). Fixes headless RCE and --yolo prompt injection risks. Upgrade to v1.83.7 to secure your pipelines.
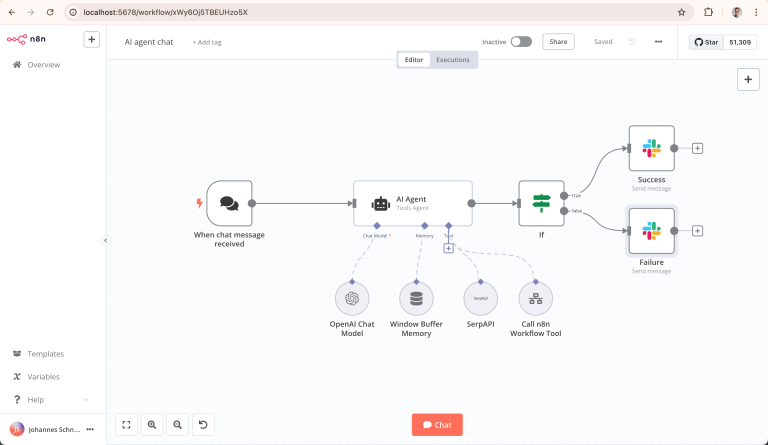
Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.
ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.
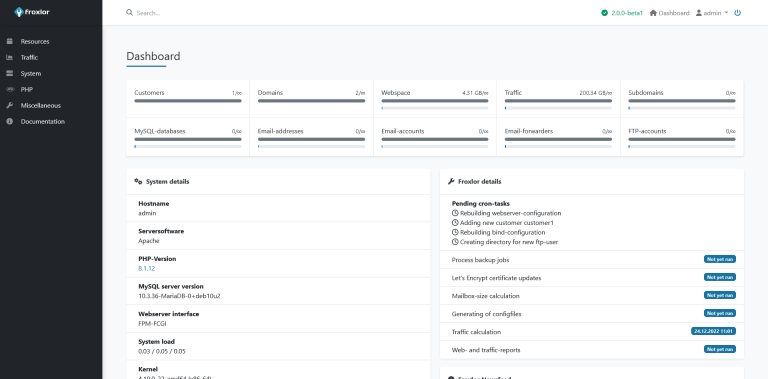
Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!
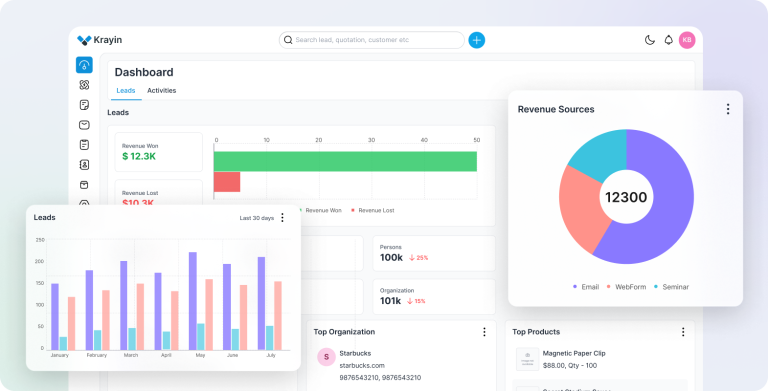
Krayin CRM faces a critical CVSS 10 RCE flaw in its TinyMCE upload endpoint. Authenticated users can seize server control. Patch version 2.2.x immediately!
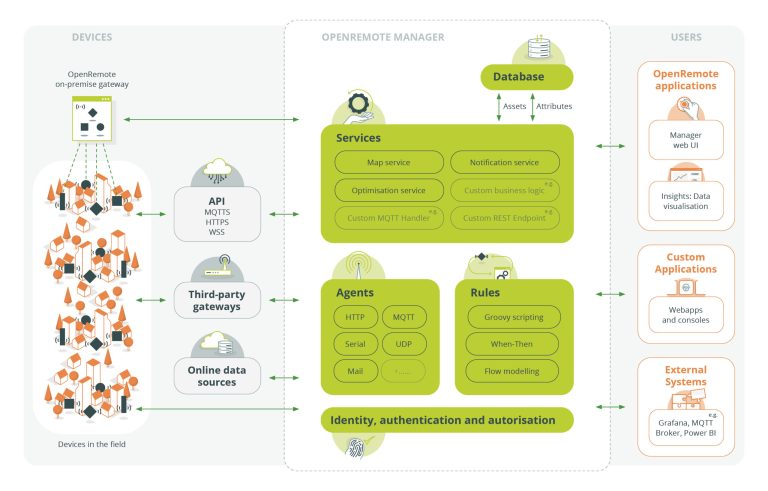
OpenRemote CVE-2026-39842 is a critical CVSS 10 flaw allowing RCE via JavaScript and Groovy injection. Secure your IoT assets—upgrade to v1.22.0 now!
AVideo’s YPTSocket plugin faces a critical CVSS 10 vulnerability. Unauthenticated attackers can hijack every active session at once. No patch is available.
Juju's critical CVSS 10 flaw (CVE-2026-5412) allows low-level users to steal master cloud credentials. Secure your AWS/Azure/GCP environments—upgrade now!
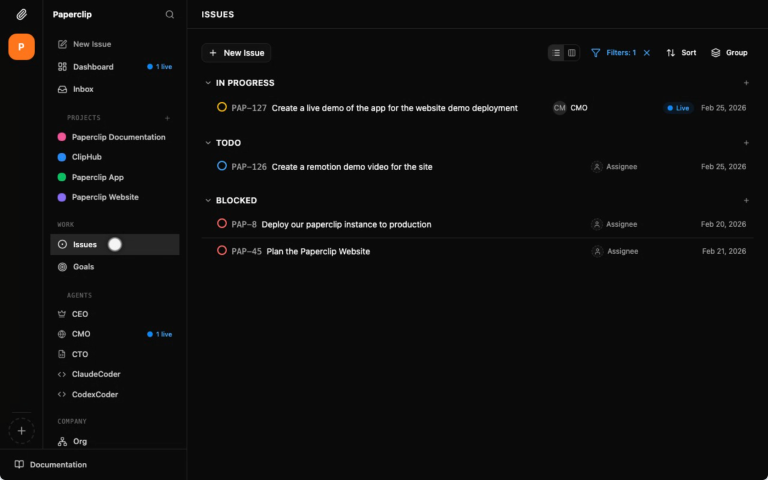
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!