 Do Son
Sentry reveals a critical 9.1 CVSS flaw (CVE-2026-42354) in SAML SSO. Multi-org instances are at risk of account takeover via identity linking. Patch now!
CVSS 9.1
New Spring Boot flaws (CVSS 9.1) bypass security filters and enable RCE via timing attacks. Impacting versions 2.7.x to 4.0.x—secure your Java apps now.

Clerk reveals a critical 9.1 CVSS flaw in createRouteMatcher. Crafted requests can bypass middleware gating in Next.js, Nuxt, and Astro. Patch your apps now!
A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.
Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!
Scriban’s 9.1 CVSS flaw allows sandbox escapes in .NET apps via a cache bypass. Over 40M downloads affected. Update to version 7.0.0 to secure your templates.
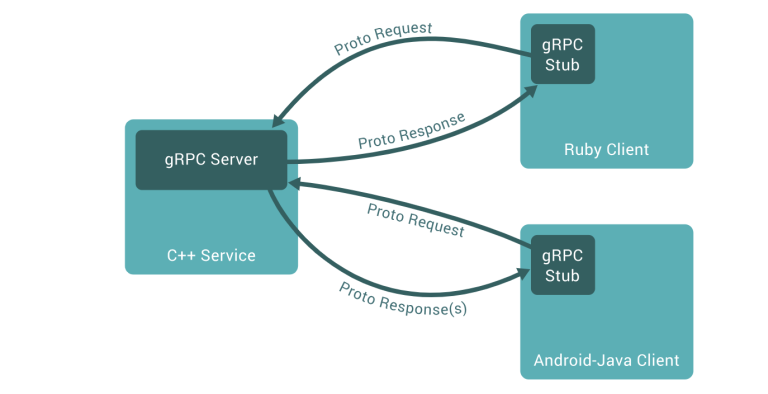
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.

A critical 9.1 CVSS flaw in Spring Security (CVE-2026-22732) fails to write HTTP headers, exposing Java apps to severe data leaks. Update immediately.

Fortinet warns of critical SQL injection CVE-2026-21643 in FortiClient EMS 7.4.4. Unauthenticated attackers can execute code. Update to v7.4.5 now.

ManageEngine patches critical ADSelfService Plus flaw CVE-2025-11250 (CVSS 9.1). Update to Build 6519 immediately to secure your Active Directory.

Lexmark CVE-2025-1127 flaw allows remote code execution via embedded web server. Affects many printer models—patch firmware to version .240.206+ now.

A CVE-2025-43859 vulnerability in Python’s h11 library may lead to request smuggling attacks when paired with buggy proxies. Patch to version 0.15.0 now.