
 Do Son
CVE-2026-63455 and CVE-2026-63456 let attackers bypass web authentication on HPE EdgeConnect Orchestrator. CVSS 9.8. Patch now.
CVSS 9.8
A critical Windows DNS Client RCE vulnerability (CVE-2026-41096) with a 9.8 CVSS has public PoC exploit code. Learn how to detect and patch it.

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.
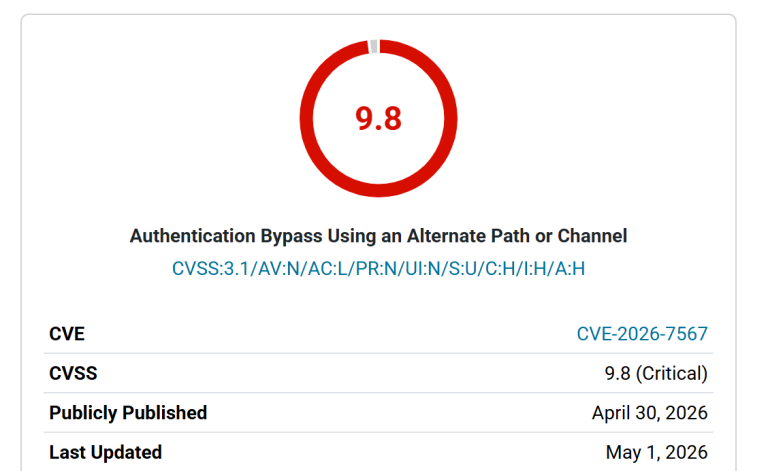
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
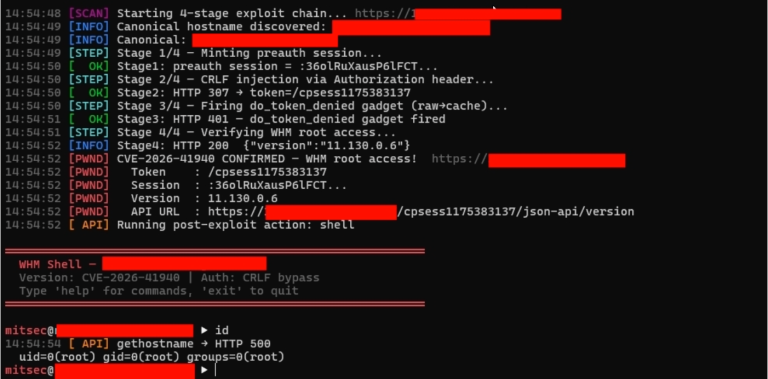
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!
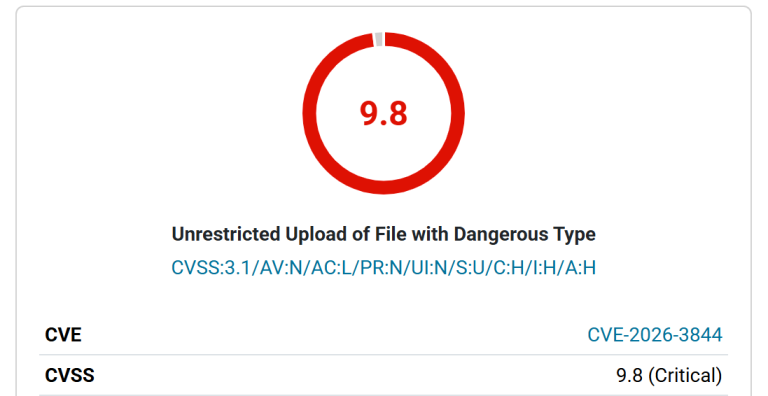
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
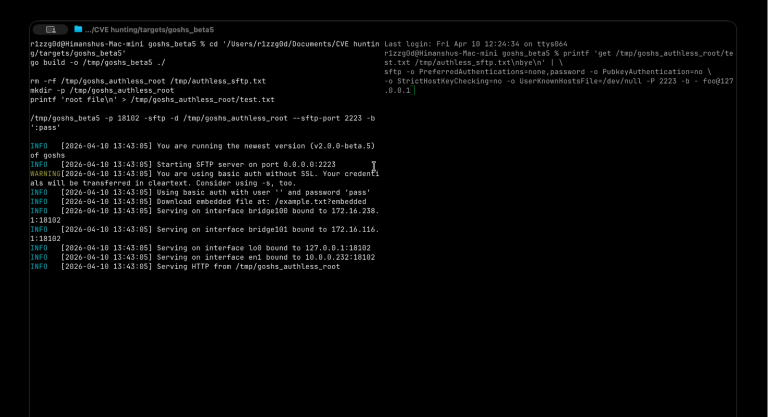
Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!

Juniper warns of a critical 9.8 CVSS flaw in JSI vLWC. A default password allows unauthenticated attackers to take full device control. Update to 3.0.94 now!

CISA alerts to a 9.8 CVSS flaw in Anritsu Spectrum Monitors (CVE-2026-3356). No patch is coming for this authentication bypass. Secure your network now!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20093) in IMC. Unauthenticated attackers can change admin passwords and seize full control. Update now!

Oracle warns of a critical 9.8 CVSS vulnerability (CVE-2026-21992) allowing unauthenticated attackers to take over Fusion Middleware and Identity Manager.
A critical 9.8 CVSS vulnerability (CVE-2026-21994) in Oracle's Edge Cloud Infrastructure Toolkit allows unauthenticated remote attackers a total takeover.
A critical 9.8 CVSS vulnerability (CVE-2026-32136) in AdGuard Home lets unauthenticated attackers hijack network DNS settings. Update to v0.107.73 now.
CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.

Critical Unstructured library flaw CVE-2025-64712 (CVSS 9.8) allows RCE via malicious .msg files. 4M+ downloads affected. Update to v0.18.18 now.

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.
Zenitel TCIV-3+ intercoms face critical, unauthenticated command injection and XSS flaws (CVSS 9.8). Update to v9.3.3.0 immediately to patch.

CISA warned of a Critical Auth Bypass flaw (CVE-2025-12108, CVSS 9.8) in Survision LPR Cameras. The lack of password enforcement allows unauthenticated attackers to gain full system access.

Urgent patch for Post SMTP plugin. A CVSS 9.8 flaw lets unauthenticated attackers read email logs and steal password reset links to take over accounts.

Urgent patch for WP Freeio plugin (v.< 1.2.22). Unauthenticated attackers can gain admin control instantly via a registration flaw. Update immediately to v.1.2.22.

A critical flaw in the Case Theme User WordPress plugin (CVSS 9.8) allows unauthenticated attackers to hijack admin accounts. The vulnerability is under active exploitation.

Sophos has patched a critical authentication bypass flaw (CVE-2025-10159) with a CVSS 9.8 score in its AP6 wireless access points. Admins are urged to update now.