
 Do Son
HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!
cybersecurity alert

CISA adds critical DrayTek router, Chrome, and SAP NetWeaver flaws to its KEV list after in-the-wild exploitation. Federal agencies face a June 5th patch deadline.

Hackers exploited GovDelivery to send fake TxTag toll emails via Indiana government accounts. Learn how the phishing scam unfolded and how to stay protected.

Rancher patches CVE-2024-22031, a privilege escalation flaw allowing cross-cluster access. Update to v2.11.1, v2.10.5, or v2.9.9 to stay protected.
JPMorgan Chase CISO urges software providers to prioritize security in SaaS delivery, warning of rising risks to global infrastructure and supply chains.
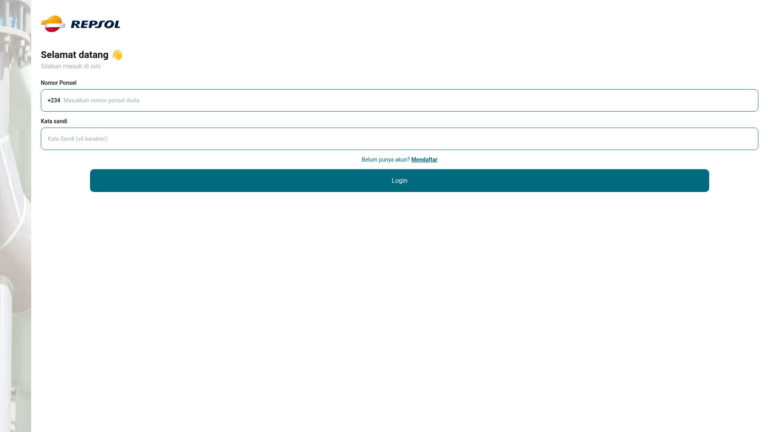
Power Parasites targets users with job and investment scams using fake domains mimicking Siemens, Repsol, Netflix, and more, Silent Push reports.

A new phishing campaign targets WooCommerce users with fake security alerts. Learn how attackers use IDN homographs and malicious plugins to compromise stores.
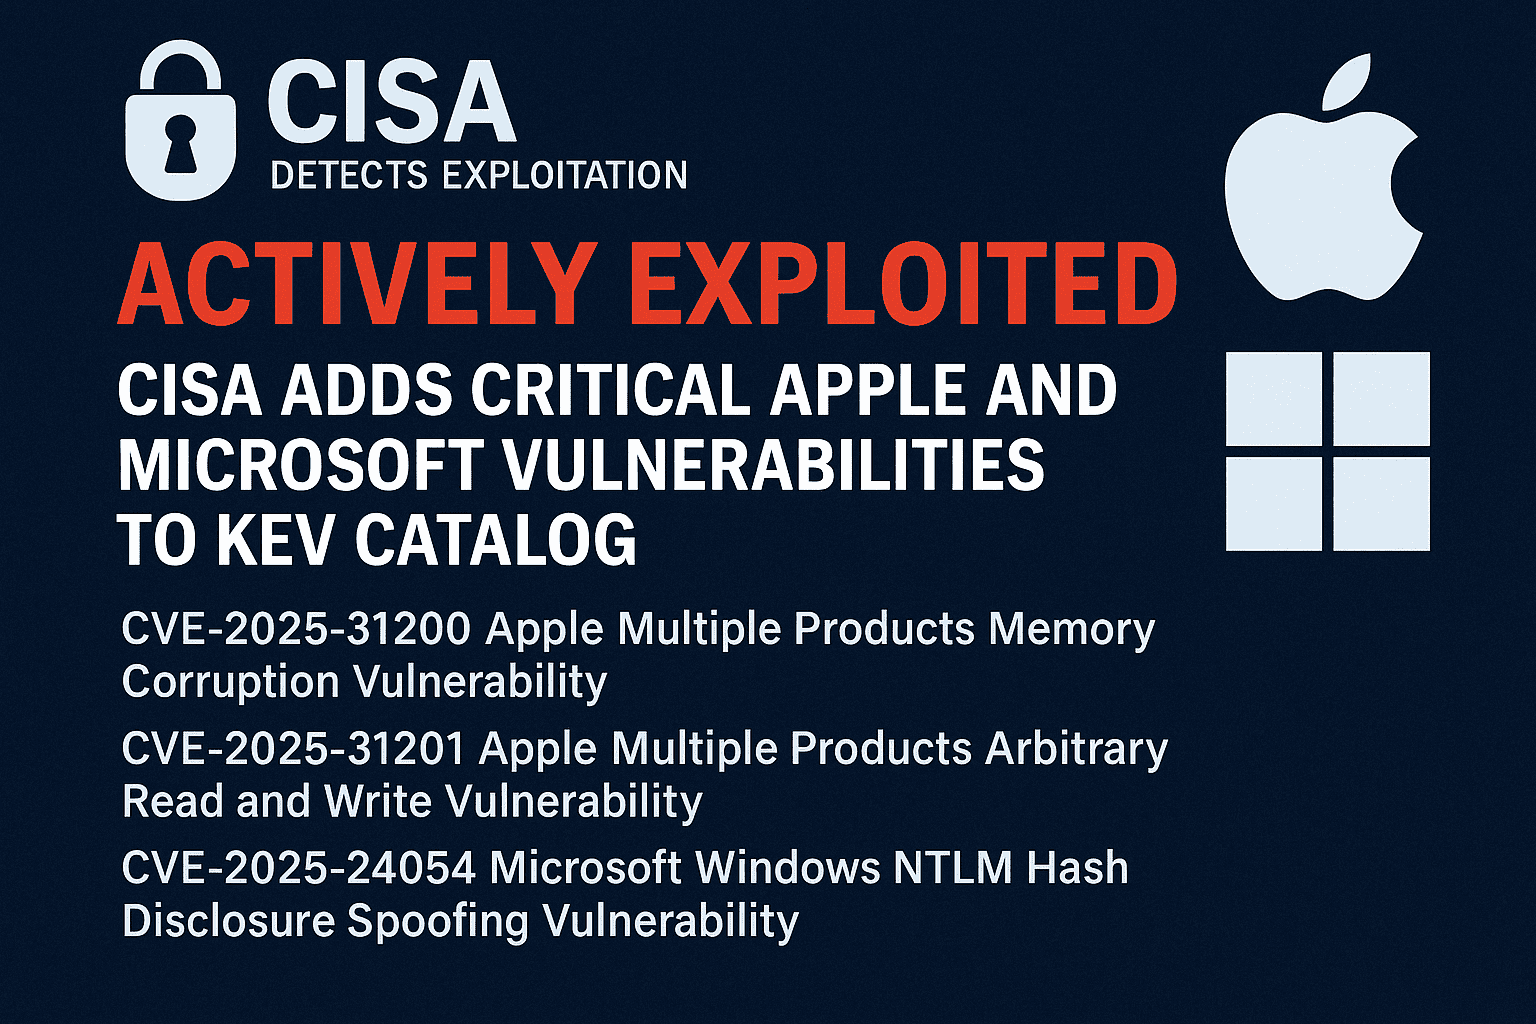
CISA warns of actively exploited vulnerabilities in Apple and Microsoft products. Urgent patching is required to mitigate risks from these attacks.

CISA warns of potential risks from Oracle cloud credential exposure. Urges password resets, MFA, and vigilance against phishing attacks.