 Do Son
Tenable exposes "LeakyLooker"—9 cross-tenant flaws in Google Looker Studio that let hackers manipulate and exfiltrate GCP data. Google has patched them.
data exfiltration
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.
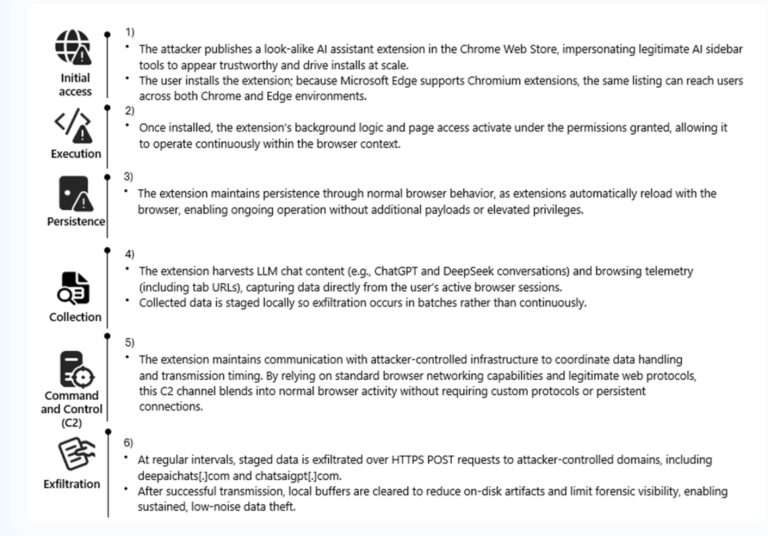
Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?

New "Exfil Out&Look" attack uses OWA add-ins to steal emails without leaving logs. Microsoft has no immediate fix for this blind spot.

Microsoft patches "Reprompt," a critical Copilot flaw. Attackers could steal sensitive data with just one click on a legitimate link.

CVE-2025-68428 reveals a 9.2 critical flaw in jsPDF's Node.js build, allowing arbitrary file reads from servers. Upgrade to version 4.0.0 now!

Koi Security uncovers lotusbail, a malicious npm package with 56k downloads that functions perfectly while stealing WhatsApp credentials and chats.

LangChain patches a critical 9.3 CVSS flaw (CVE-2025-68664) where unescaped "lc" keys allow attackers to steal API secrets via prompt injection.

PCPcat exploited Next.js/React flaws to hijack 59,128 servers in just 48 hours. Protect your cloud credentials and patch CVE-2025-55182 now!

A malicious Go package typosquat (bpoorman/uuid) operated for four years, using a hidden Valid function to silently encrypt and exfiltrate sensitive data to dpaste.com.

Malicious packages across npm, PyPI, and RubyGems are exploiting Discord webhooks as stealthy, resilient C2 endpoints to exfiltrate developer config files and sensitive host data.
Rapid7 identified the Crimson Collective using TruffleHog to find leaked AWS IAM keys. The group achieves Admin access to steal data from RDS/S3 and extort victims.

A new XCSSET variant targets macOS developers by infecting Xcode projects. It now steals Firefox data, hijacks clipboards for crypto theft, and enhances its persistence.

A new report reveals The Gentlemen ransomware group is using legitimate drivers and Group Policy to bypass defenses and deploy highly tailored malware.

A critical XXE flaw in Apache Tika's PDF parser could allow attackers to access sensitive data and pivot into internal networks via crafted PDF files.

Trend Micro research exposes Crypto24, a coordinated ransomware operation that uses legitimate tools, custom malware, and advanced evasion tactics to breach and extort victims.

Trellix uncovers 0bj3ctivityStealer, a sophisticated info-stealer using phishing, custom PowerShell, and steganography to evade detection and exfiltrate sensitive data.

Cyfirma reveals Raven Stealer, a new, lightweight MaaS infostealer built in Delphi/C++, using reflective process hollowing and Telegram bots for stealthy data exfiltration from browsers.

BlackSuit, a rebranded Royal/Conti ransomware, unleashes destructive multi-stage attacks. It uses Cobalt Strike, rclone for data exfil, and deletes shadow copies for stealth and speed.