 Do Son
A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
data exfiltration
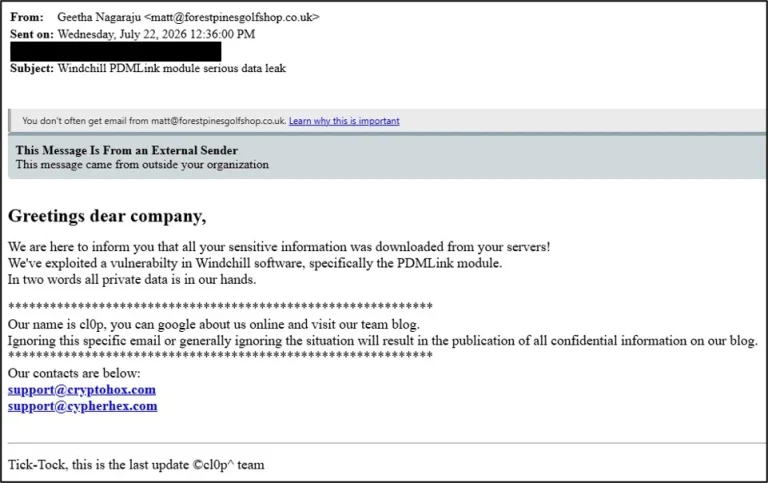
The Clop web shell targets PTC Windchill via CVE-2026-12569, stealing credentials and engineering data in a mass-extortion campaign.

A new report reveals how malicious AI extensions use browser data exfiltration tactics to steal private conversations from ChatGPT and Claude.

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.
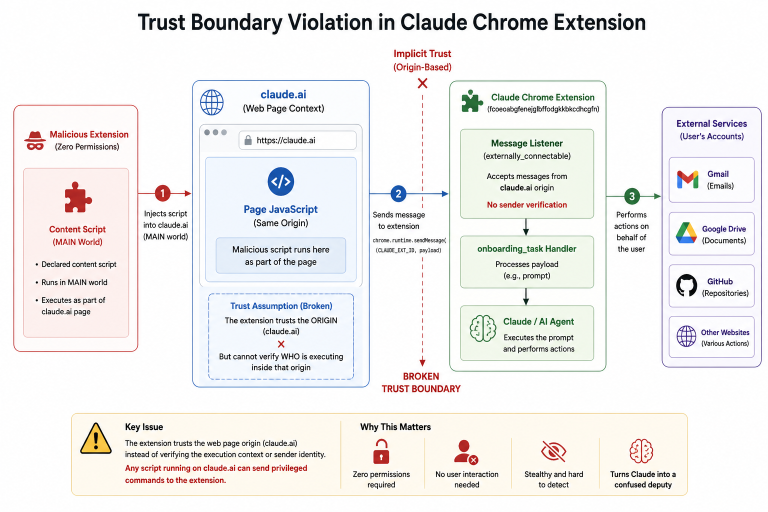
LayerX uncovers a critical flaw in Anthropic’s Claude extension. Learn how attackers can hijack AI agents to steal data and bypass security policies.

Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.

Checkmarx discloses a major GitHub breach via a Trivy supply chain flaw. Attackers injected malicious code and exfiltrated data for a month. Get the facts.
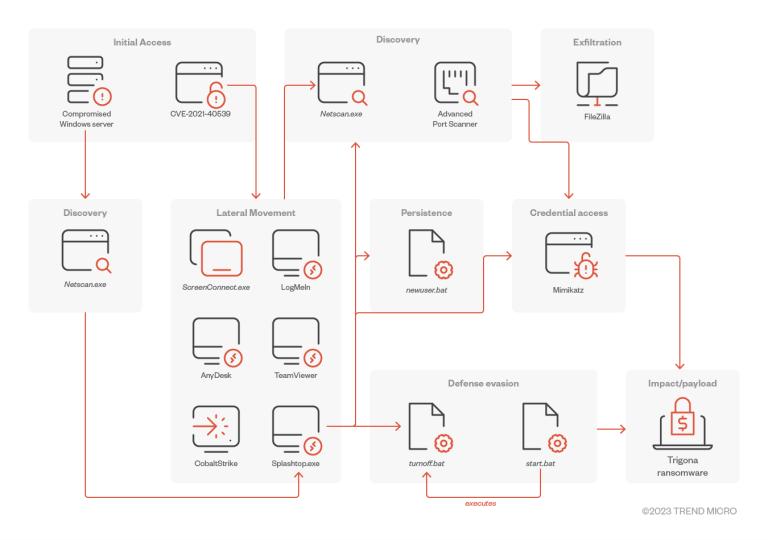
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.

Microsoft hardens RDP in the April 2026 update. Discover how new default isolation policies and security warnings stop malicious servers from stealing your data.
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!
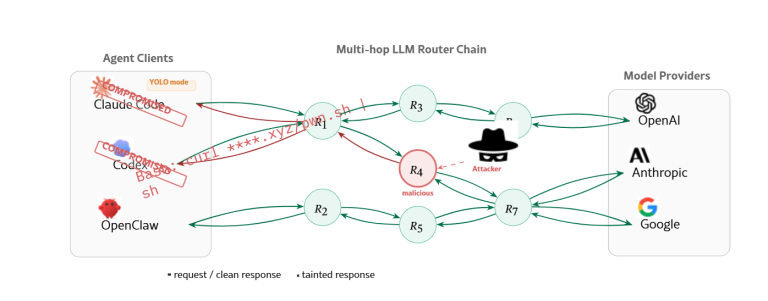
New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.

Unit 42 reveals how GCP Vertex AI agents can become "double agents," exfiltrating data and accessing Google’s internal code. Learn why BYOSA is essential.

Check Point Research uncovers a DNS tunneling flaw in ChatGPT allowing silent data theft. OpenAI deployed a fix on Feb 20, 2026. Is your AI chat truly private?
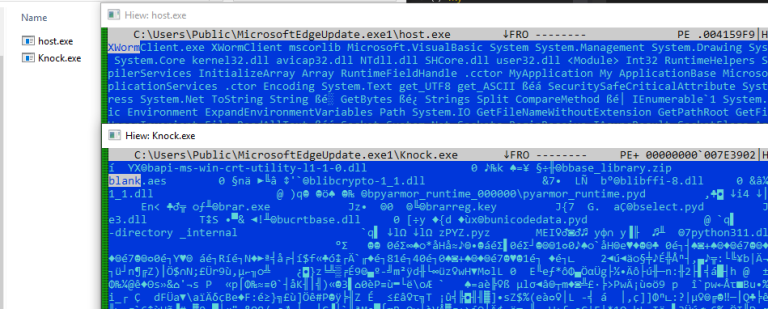
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.

Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER: AI-aided malware using USB drives to steal data from air-gapped financial networks. Update your defenses!

PTC issues a critical advisory for Windchill and FlexPLM. CVE-2026-4681 is an RCE flaw allowing full server control via deserialization. Patch now!
Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.
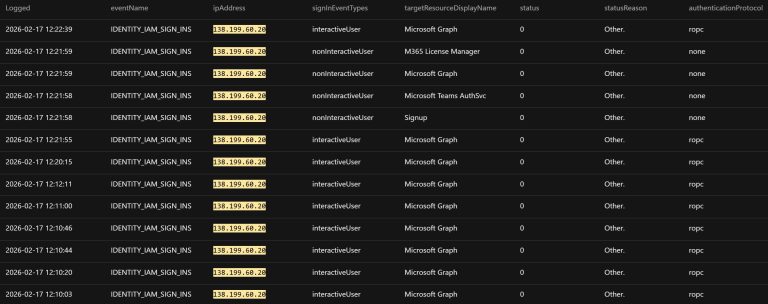
Trend Micro reveals how an exposed Spring Boot Actuator and a spreadsheet of plaintext secrets led to a malware-less SharePoint data exfiltration attack.