 Do Son
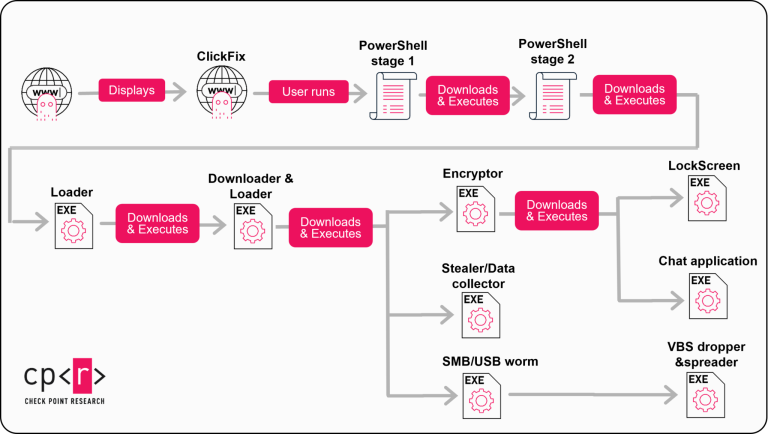
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.
Data Theft

Unpatched CVE-2026-5756 in DRC INSIGHT allows unauthenticated hijacking of student exam responses and traffic manipulation. Secure your school's network now.
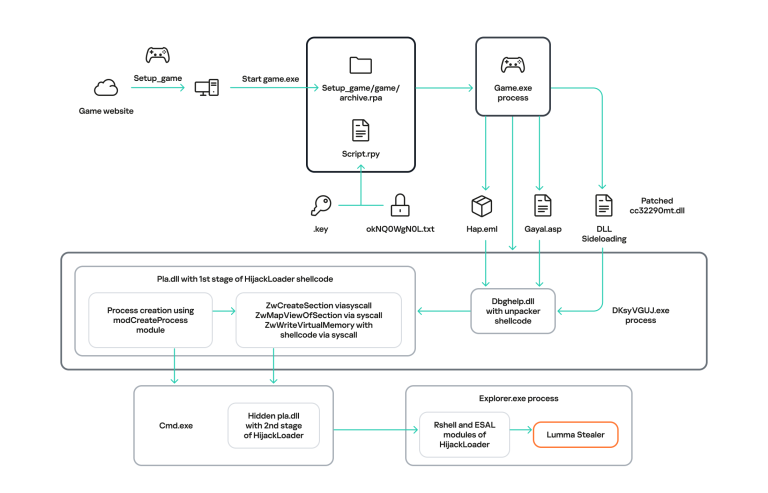
Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.

Scammers target PNB MetLife users via mobile phishing. Attackers use Telegram bots to steal data & manipulate clipboards for UPI fraud.

Gen Digital uncovers AuraStealer, a new infostealer using TikTok "Scam-Yourself" tactics to trick users into infecting their own Windows PCs.
CISA added a critical XXE flaw (CVE-2025-58360) in OSGeo GeoServer to the KEV Catalog. The actively exploited bug allows attackers to read arbitrary files and perform SSRF on internal networks. Patch immediately.

Kaspersky exposed the Mysterious Elephant APT targeting South Asia. The group uses MemLoader and custom tools (BabShell) to steal sensitive WhatsApp desktop data and exfiltrate documents.

Red Hat confirmed a breach of its consulting arm's GitLab instance. Hackers stole 570 GB of data, including Customer Engagement Reports that detail client network infrastructure.

A new report shows LAPSUS$, Scattered Spider, and ShinyHunters have formed a collaborative alliance, sharing tactics like social engineering and MFA bypass to launch global attacks.

The FBI has issued a FLASH Alert warning about UNC6040 and UNC6395, two groups actively compromising Salesforce via vishing and malicious OAuth apps to steal data.

A hacker group is extorting an art platform with a new threat: if the ransom isn't paid, they will feed the stolen artworks to AI training models.

A new report reveals a widespread data theft campaign targeting Salesforce instances. Attackers used compromised OAuth tokens from a third-party app to steal data and credentials.

Anthropic's new Claude AI extension for Chrome allows it to read websites, but the tool also introduces a risk of prompt injection attacks that could lead to data theft.

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.
Splunk exposes a campaign weaponizing Inno Setup installers to deploy RedLine Stealer, using obfuscated Pascal scripts and HijackLoader to steal browser/crypto data.

A Chinese student was jailed in London for running a smishing campaign with an "SMS Blaster" hidden in his car, spoofing texts to steal data.

CoinMarketCap suffered a client-side attack on June 20, 2025, using a fake "doodle" graphic to deliver Inferno Drainer, stealing over $43,000 from user wallets.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.

CyberEye, a modular .NET RAT, offers widespread data theft and surveillance using a builder, Telegram C2, and anti-analysis features, making it a new threat.

Beware 'imad213,' a fake Instagram booster stealing credentials via social engineering and bot services. Learn how to protect your account.

Katz Stealer, a new MaaS infostealer, targets browsers, crypto wallets, and Discord using advanced evasion and UAC bypass techniques.

AppleProcessHub, a new macOS infostealer, uses an Objective-C dropper and AES-decrypted C2 to steal sensitive files like SSH keys and Keychain.