 Do Son
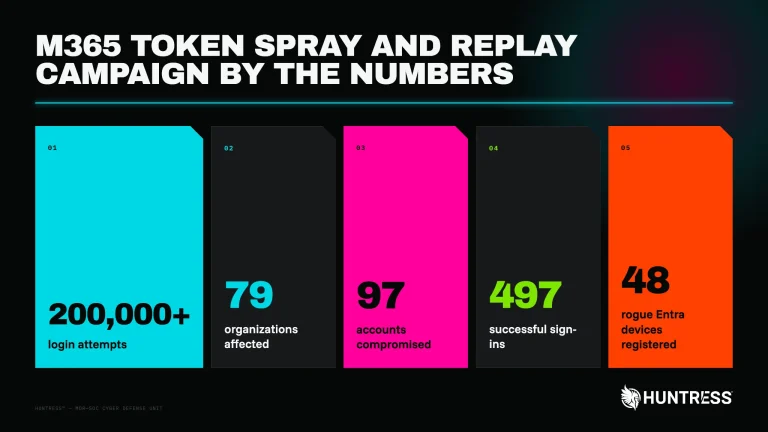
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
Device Code Phishing
Microsoft led a coalition disrupting EvilTokens cybercrime platform. Learn how the EvilTokens cybercrime platform used AI and device code phishing.
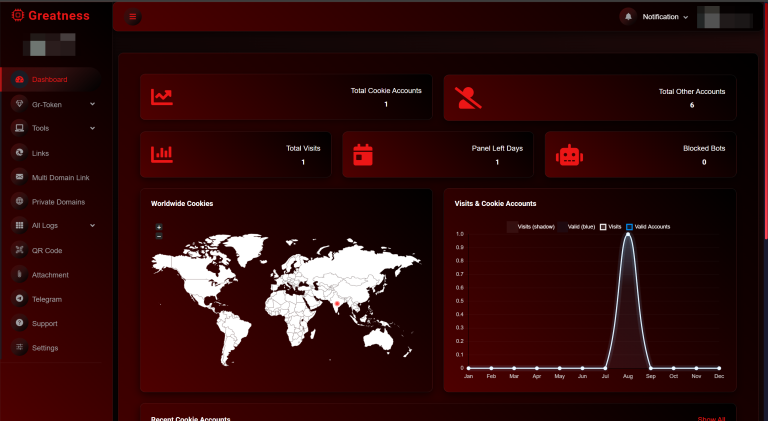
Researchers expose the Greatness PhaaS platform, an AiTM phishing kit sold on Telegram that steals Microsoft 365 tokens past MFA.
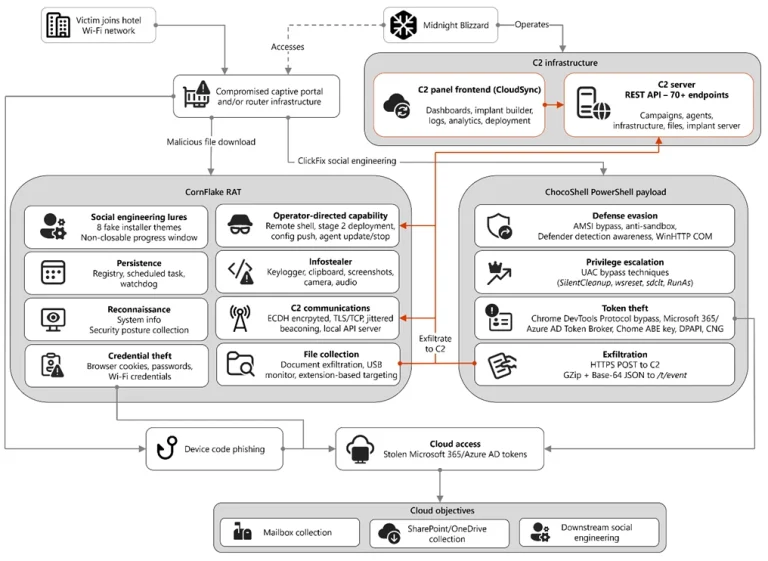
CaptiveCrunch malware campaign hijacks hotel Wi-Fi captive portals worldwide. Microsoft ties Storm-2945 to Midnight Blizzard, Russia SVR-linked group.
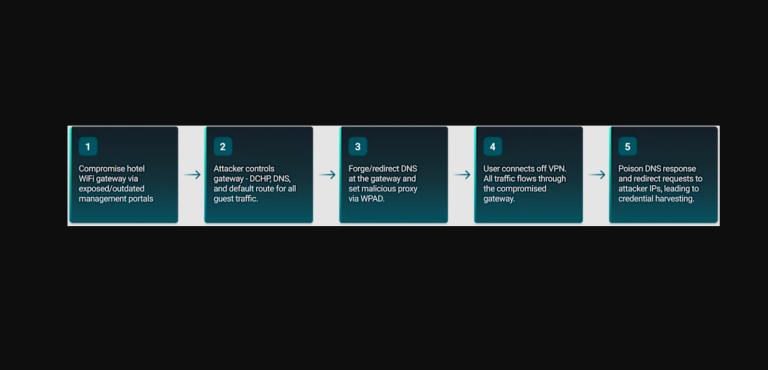
ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
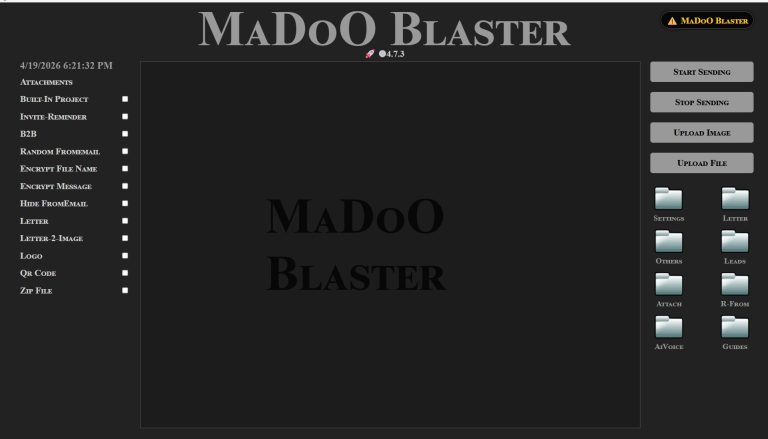
A misconfigured server exposed three AiTM phishing operators running Evilginx MFA bypass and Device Code attacks on Microsoft 365 accounts.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.
Cisco Talos exposes ARToken, a phishing platform using device code phishing to steal Microsoft 365 tokens and bypass MFA.
A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.
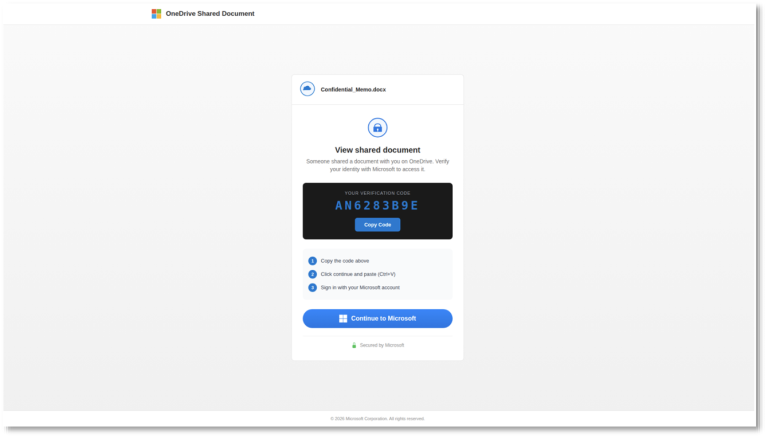
AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!
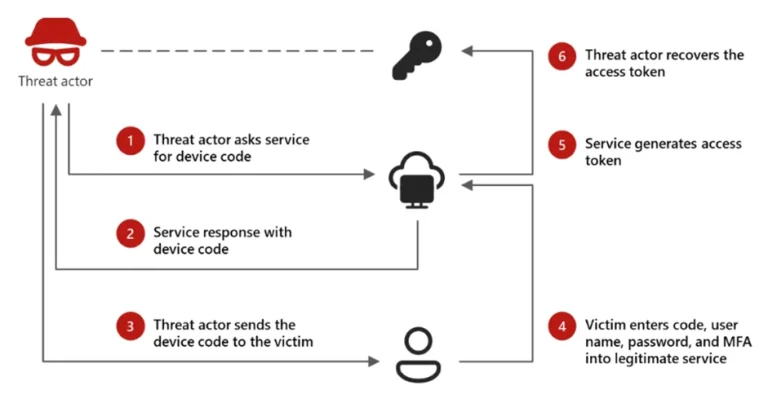
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!