
 Do Son
Progress patched a critical Chef Automate vulnerability tracked as CVE-2026-80462. Fix this Chef Automate vulnerability to stop DevOps account takeovers.
DevOps Security
The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
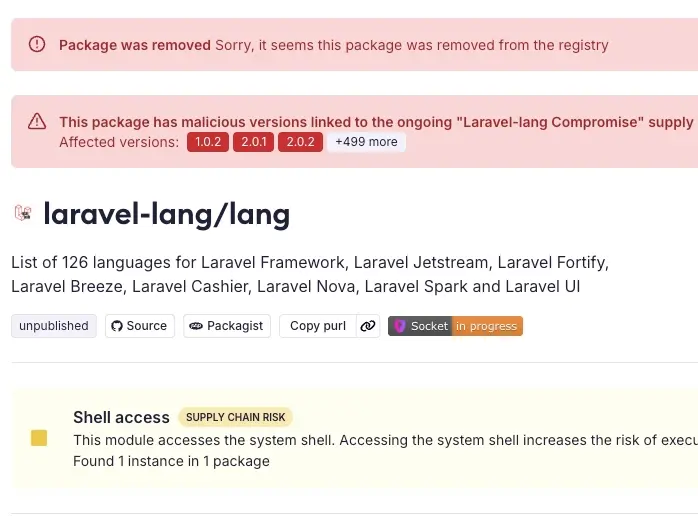
DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.

GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!

Trend Micro uncovers QLNX, a fileless Linux RAT targeting AWS, NPM, and Kubernetes keys. Learn how its eBPF rootkit hides from even the deepest system scans.

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!

Anthropic's Boris Cherny confirms a "human error" leaked Claude Code's source via MAP files. Discover how manual steps led to 8,100+ GitHub repository purges.

Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.
Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.

GitLab fixes critical CVE-2025-7659 (CVSS 8.0). Unauthenticated attackers can steal tokens via Web IDE. Update to v18.8.4 now to secure your code.

GitLab patches high-severity 2FA bypass (CVE-2026-0723) & DoS flaws. Update to 18.8.2, 18.7.2, or 18.6.4 immediately to secure your instance.

New "cloud-first" malware VoidLink targets Linux & containers with advanced stealth. Written in Zig, it mimics Cobalt Strike to evade EDR. Check your cloud.

Zscaler detects NodeCordRAT, a new malware in malicious npm packages. It uses Discord as a C2 server to loot crypto wallets and Chrome data.
Critical GitLab updates (18.6.1/18.5.3) fix severe CI/CD credential theft (CVE-2024-9183) & unauthenticated DoS flaws. Upgrade immediately.