 Do Son
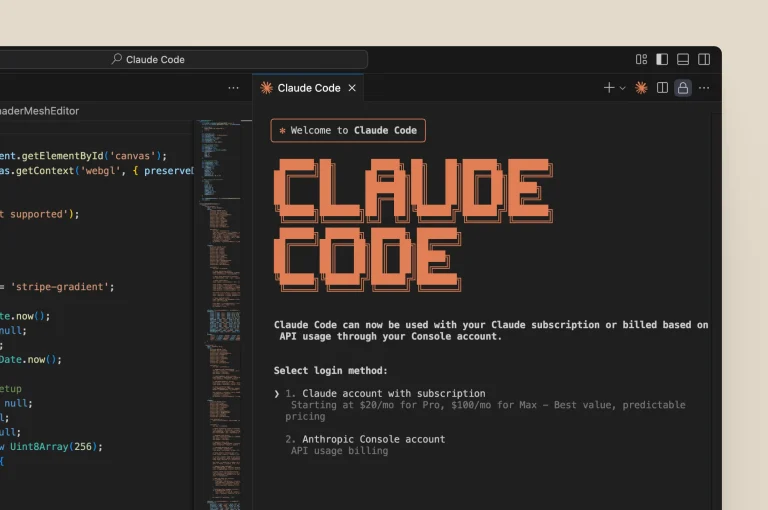
Anthropic updated Claude Code permission modes with a toggle to suppress confirmation prompts for dangerous deletion commands during automated workflows.
DevOps
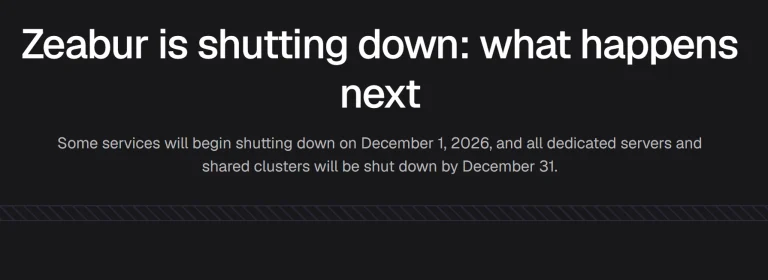
The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.
Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!

Urgent: Apache CloudStack patches critical flaws (CVE-2026-25199, CVE-2026-25077) enabling VM hijacking and KVM host RCE. Secure your cloud environment now.

SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!
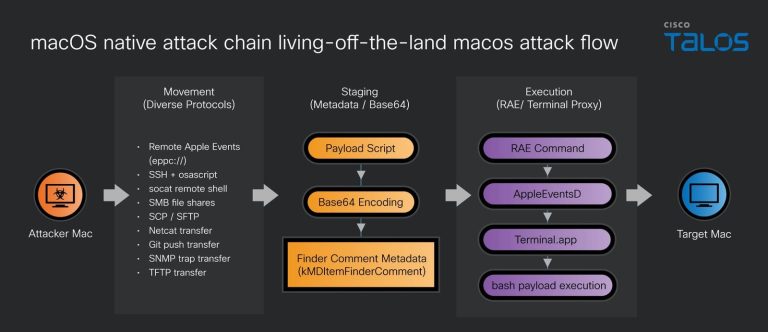
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.

Atlassian Bamboo Data Center hit by critical 9.4 RCE (CVE-2026-21571). Attackers can hijack your build pipeline. Secure your supply chain—patch now!
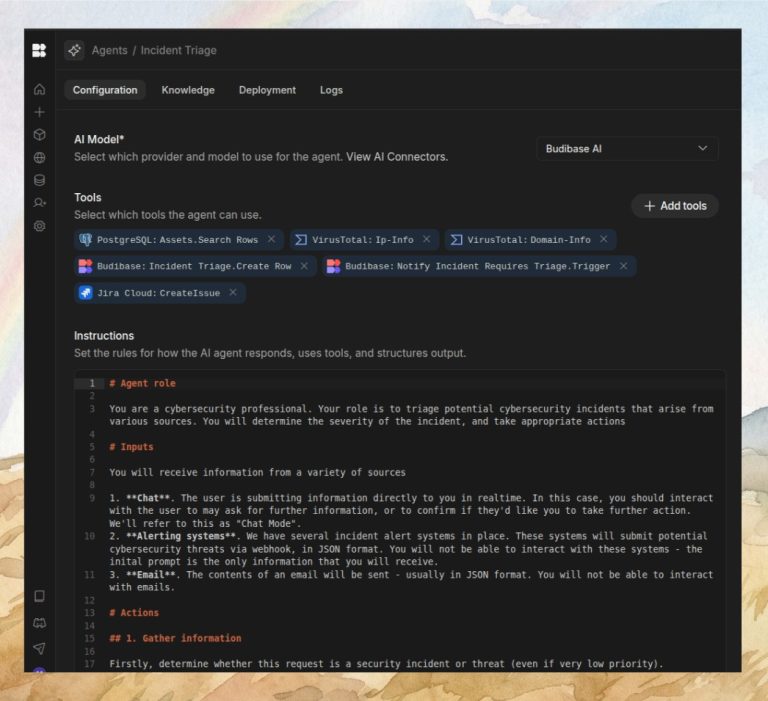
A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.

Google launches the Android CLI for agent-centric workflows. Reduce LLM token usage by 70% and accelerate app development 3x with official AI-ready tools.

CVE-2026-34612: A critical 10.0 flaw in Kestra allows RCE via SQL injection in label searches. Protect your orchestration server—update to v1.3.7 now!
OpenTelemetry patches a critical 9.3 RCE flaw (CVE-2026-33701) in its Java agent. Unfiltered RMI deserialization allows full system takeover. Update to 2.26.1.

Apache NiFi flaw CVE-2026-25903 allows unauthorized users to modify restricted components. Update to version 2.8.0 immediately to secure data pipelines.

HAProxy patches high-severity QUIC flaws CVE-2026-26080 & 26081. Remote attackers can crash servers via malformed packets. Update to v3.0.16 now.
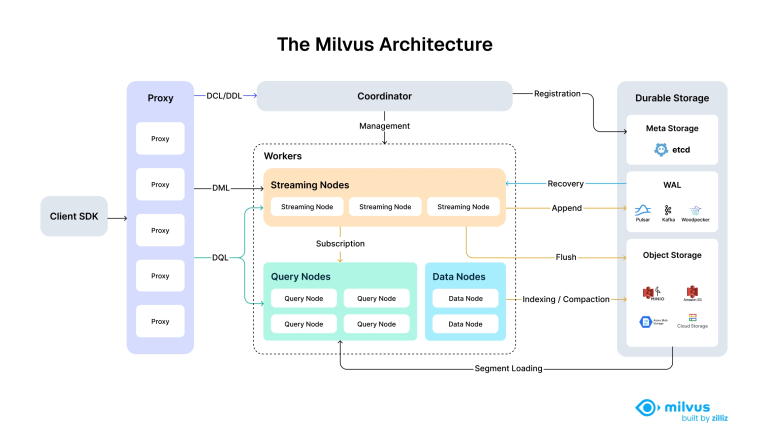
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

Apache HertzBeat flaw CVE-2026-24343 allows DoS via XPath injection. Vulnerable versions 1.7.1-1.7.9. Update to v1.8.0 immediately.

High-severity Rancher CLI flaw (CVE-2025-67601) exposes credentials via MitM attacks when using --skip-verify. Update or use -cacert immediately.

Critical PHPUnit flaw CVE-2026-24765 (CVSS 7.8) allows RCE via unsafe deserialization in coverage files. Vulnerability hits CI/CD pipelines. Update now.
Critical Coolify flaws (CVE-2025-64419+) expose 52k instances to root RCE and SSH key theft. Patch immediately to secure your self-hosted apps.

Aikido Security uncovers the first sophisticated malware on Maven Central: a "prefix swap" attack on the Jackson library used to steal data.

n8n warns of a CVSS 10.0 RCE (CVE-2025-68613) in its expression system. Attackers can seize total server control. Upgrade to v1.122.0 immediately.