
 Do Son
CoreDNS 1.14.3 addresses 5 critical flaws in DoH, DoQ, and gRPC. Fix authentication bypasses and DoS risks by upgrading your DNS infrastructure today.
DoH

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.
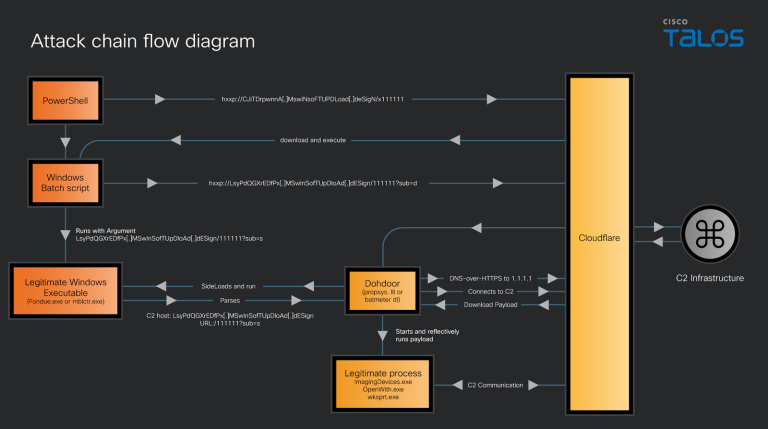
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.

China-nexus WARP PANDA APT targets VMware/Azure with BRICKSTORM, a Golang backdoor using DoH for stealth. The group creates "ghost VMs" and conducts session replay attacks for long-term espionage.

CISA/NSA exposed BRICKSTORM, a Chinese state-sponsored backdoor targeting VMware vCenter/ESXi and ADFS servers. The self-restarting malware used DoH and nested TLS for 18 months of persistent espionage.

NCSC reveals SHOE RACK, a stealthy post-exploitation malware using reverse SSH tunneling, DoH, and protocol abuse to maintain remote access on FortiGate 100D firewalls.

Critical DoS vulnerability (CVE-2025-30194) impacts PowerDNS DNSdist 1.9.0-1.9.8 with DoH. Upgrade to 1.9.9 or use h2o provider.