 Do Son
Elastic Security Labs uncovered a CyberStrikeAI AWS intrusion and CyberStrikeAI AWS CloudTrail intrusion that pulled 56 EC2 scripts in 141 milliseconds.
Elastic Security Labs
A fake Web3 accelerator used malicious npm packages to drop stealers on macOS and Windows and reroute AI coding agent traffic to its servers.
Learn how Brazilian KREMLIN banking malware steals credentials using fake browser extensions. Elastic Security Labs details the KREMLIN banking malware.

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.

Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.

An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.
Elastic Security Labs exposes TCLBANKER, an advanced banking trojan that hijacks WhatsApp to spread while blinding defenders with invisible WPF overlays.
Elastic Security Labs unmasks REF1695, a threat actor using the CNB Bot and custom XMRig loaders for Monero mining and CPA fraud. Is your server a silent miner?

Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER: AI-aided malware using USB drives to steal data from air-gapped financial networks. Update your defenses!

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.
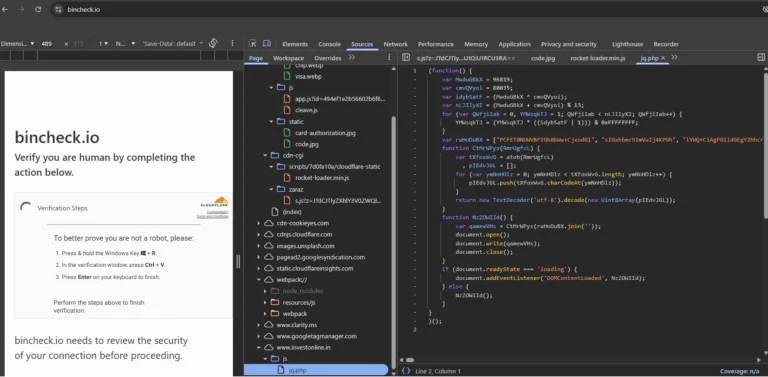
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.
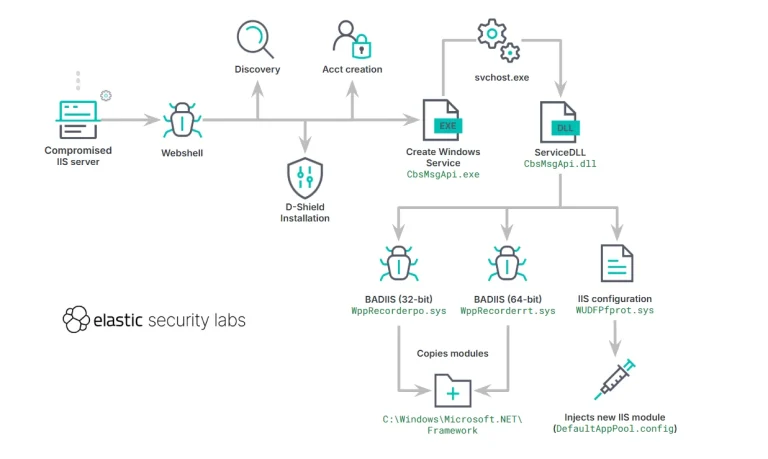
Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.
WARMCOOKIE has resurfaced post-Operation Endgame with new execution handlers, a MaaS model, and evasive techniques like disguised scheduled tasks using company names.

Elastic Security Labs reveals SHELLTER Elite v11.0 is being abused to deploy LUMMA, RHADAMANTHYS, and ARECHCLIENT2 infostealers, leveraging advanced evasion techniques to bypass AV/EDR
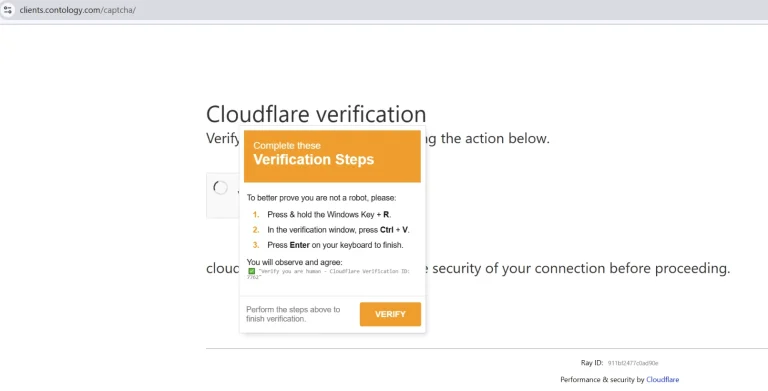
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.