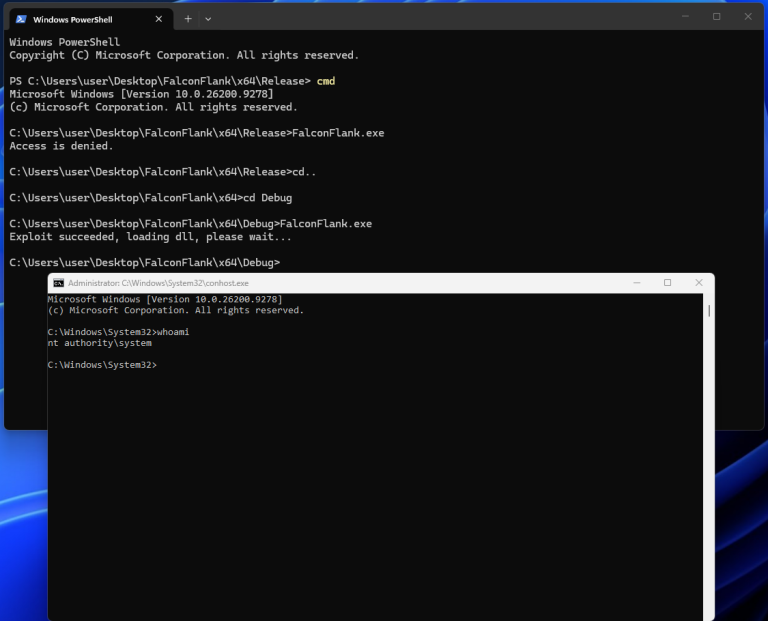
 Do Son
A researcher claims a CrowdStrike Falcon vulnerability enabling privilege escalation and published a PoC. CrowdStrike has not confirmed it; no CVE exists.
endpoint security
Two critical WatchGuard Agent flaws (CVE-2026-57909, CVE-2026-57910) allow unauthenticated remote code execution. Update to 1.25.13.0000 now.

Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.
Trend Micro issues a critical patch for Apex One to fix 9.8 severity vulnerabilities (CVE-2025-71210) that allow remote code execution. Update your console now!

Fortinet warns of critical SQL injection CVE-2026-21643 in FortiClient EMS 7.4.4. Unauthenticated attackers can execute code. Update to v7.4.5 now.

CrowdStrike patched two flaws in Falcon Sensor for Windows (CVE-2025-42701). Attackers with local code execution can delete arbitrary files, risking system stability.

BeyondTrust patches two high-severity LPE flaws (CVE-2025-2297, CVE-2025-6250) in Privilege Management for Windows, allowing local attackers to gain SYSTEM privileges via user profile manipulation and WMIC exploit.

Sophos has patched three high-severity LPE vulnerabilities in Intercept X for Windows (CVE-2024-13972, CVE-2025-7433, CVE-2025-7472), allowing local users to gain SYSTEM privileges.

NetSPI uncovered CVE-2025-4660 in Forescout SecureConnector, allowing unauthenticated attackers to hijack endpoints remotely via a misconfigured named pipe.

IGEL OS suffers from a critical privilege escalation vulnerability affecting OS 11 and OS 12. Users are urged to patch immediately.