 Do Son
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.
Espionage
Acronis reveals Khmer Shadow, a new espionage campaign using NIGHTFORGE loader and DLL sideloading to target Cambodian government entities with Havoc Demon.

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!
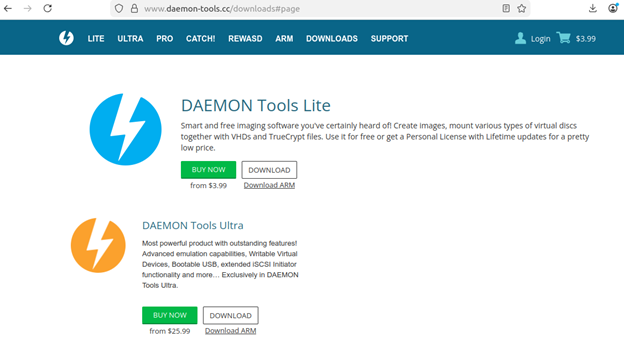
Kaspersky warns that DAEMON Tools installers (v12.5) are trojanized with the QUIC RAT. Signed binaries are being used for global espionage. Update and audit now!
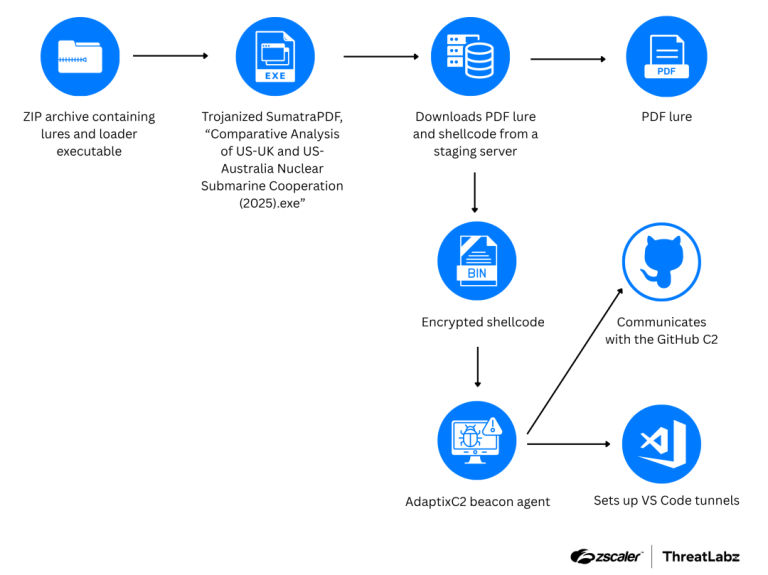
Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.

Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.

NANOREMOTE, a new Windows backdoor, leverages the Google Drive API for covert C2 and data exfiltration using OAuth 2.0 tokens. The malware shares a hard-coded AES key with the FINALDRAFT family, linking it to seasoned espionage actors.
React2Shell: Max-Score RCE (CVSS 10.0) Triggers Widespread Exploitation by Espionage Groups & Miners

React2Shell: Max-Score RCE (CVSS 10.0) Triggers Widespread Exploitation by Espionage Groups & Miners
A critical RCE (CVSS 10.0) in React Server Components (CVE-2025-55182) is under widespread exploitation by China-nexus groups deploying MINOCAT and HISONIC backdoors, plus XMRig miners.
FortiGuard exposed UDPGangster, a custom UDP backdoor deployed by MuddyWater APT. The malware evades network defenses and analysis by using UDP for C2 and checking for single-core CPUs/low RAM.

Sekoia exposed Russian Calisto APT (FSB-linked) targeting RSF and NGOs with spear-phishing. The attack uses a custom AiTM kit and a "missing file" lure to steal credentials and 2FA codes.
Bloody Wolf APT is targeting Central Asia using custom Java droppers to deploy the NetSupport RAT. The group uses geo-fencing and fake Ministry of Justice lures to achieve stealthy, persistent access for espionage.

Mandiant exposed UNC1549, an Iranian APT, using DLL search order hijacking on Citrix/VMware to deploy TWOSTROKE and DCSYNCER.SLICK. The group performs VDI breakouts for long-term espionage.

A China-linked APT targeted a U.S. policy nonprofit for weeks in April 2025. The group used DLL sideloading via a VipreAV binary and msbuild.exe scheduled tasks to achieve SYSTEM persistence for espionage.

Kimsuky APT is using a Themes.js JavaScript loader and certutil LOLBIN to gain minute-by-minute persistence via a Windows Scheduled Task. The APT is targeting think tanks for espionage.

Proofpoint exposed UNK_SmudgedSerpent, an APT using RMM tools (PDQConnect) and M365 spoofs in targeted phishing campaigns against academics and foreign policy experts with complex Iranian political lures.

Microsoft exposed SesameOp, an espionage backdoor that uses the OpenAI Assistants API for a covert C2 channel. The malware bypasses network defenses by blending encrypted commands with legitimate HTTPS traffic.

Seqrite exposed Silent Lynx APT targeting Central Asia and Russia with Operation Peek-A-Baku. The group uses LNK files and GitHub to deploy Laplas reverse shells and SilentSweeper for espionage intelligence.

Arctic Wolf exposed Chinese APT UNC6384 exploiting the ZDI-CAN-25373 Windows LNK flaw to target European diplomats. The multi-stage attack uses DLL sideloading via a Canon binary to deploy the PlugX RAT.

Unit 42 exposed Airstalk, a suspected nation-state malware that abuses VMware AirWatch (MDM) APIs for a covert C2 dead drop. The tool is used to steal credentials and browser data in supply chain attacks.