 Do Son
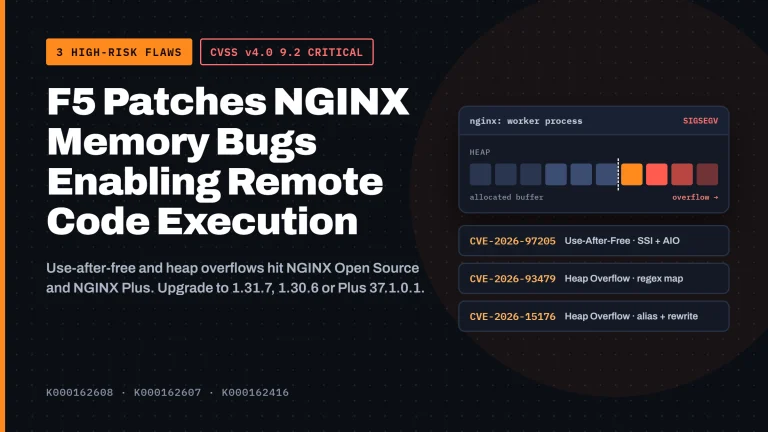
F5 patched three NGINX vulnerabilities (CVE-2026-97205, CVE-2026-93479, CVE-2026-15176) rated 9.2 Critical in F5 NGINX Plus and Open Source. Upgrade today.
F5
An exploited BIG-IP APM vulnerability tracked as CVE-2026-94127 allows RCE attacks. Secure your BIG-IP APM vulnerability deployments with new F5 hotfixes.
F5 patched the NGINX code execution flaw CVE-2026-42533, along with CVE-2026-60005 and CVE-2026-56434. Update NGINX Plus and Open Source builds now.

Two critical NGINX vulnerabilities, CVE-2026-42530 and CVE-2026-42055, let remote attackers crash workers and possibly run code. Patch NGINX now.

An NGINX heap buffer overflow vulnerability known as poolslip allows remote code execution. Learn how to secure your network servers now.
CISA adds F5 BIG-IP RCE (CVE-2025-53521) to its KEV Catalog. With a 9.8 CVSS score and active exploits, federal agencies must patch by March 30, 2026.
F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!

F5 warns of NGINX flaw CVE-2026-1642 (CVSS 8.2). MITM attackers can inject data into upstream TLS responses. Update to v1.29.5 immediately.

PoC for CVE-2025-31644 shows how admin users can exploit F5 BIG-IP Appliance Mode to gain root access via command injection.
Stay informed about CVE-2024-45844, a vulnerability in F5 BIG-IP that allows authenticated attackers to gain unauthorized access and control the system.

Critical security vulnerabilities in F5's NGINX Plus and BIG-IP Next Central Manager. Learn about CVE-2024-39809 & CVE-2024-39792

Recently, the F5 issued a security bulletin, disclosing a remote code execution vulnerability (CVE-2022-1388) in F5 BIG-IP