 Do Son
The active DriveSurge threat cluster is compromising thousands of websites. Discover how its customized Traffic Distribution System redirects victims.
FakeUpdates

Silent Push exposes SocGholish as a MaaS platform for Initial Access Brokers. The malware, disguised as fake updates, fuels top-tier Russian ransomware groups like Evil Corp.
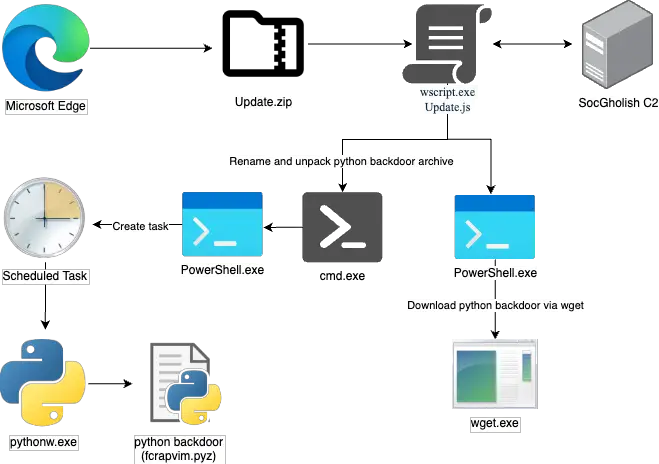
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

Huntress has recently uncovered a new wave of malicious activities involving the well-known SocGholish or FakeUpdates malware.