
 Do Son
APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
Fancy Bear
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.
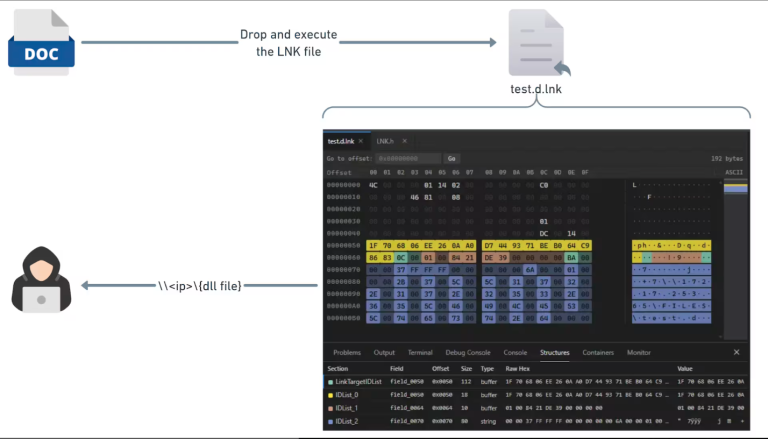
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.
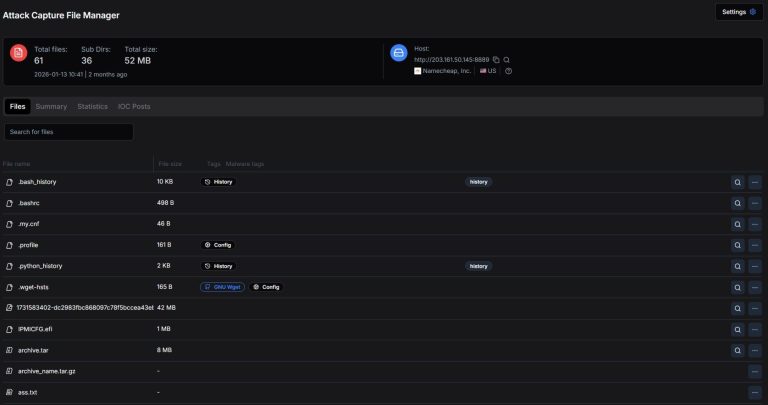
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.
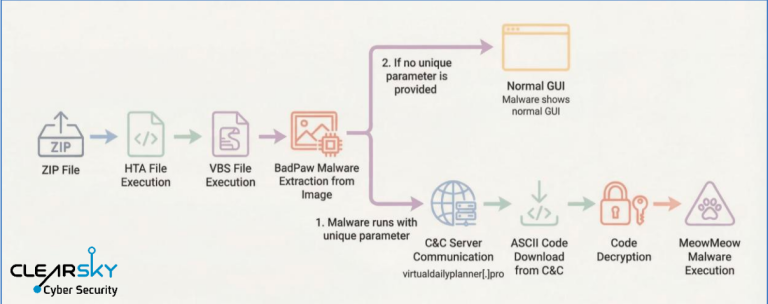
ClearSky uncovers a Russian campaign targeting Ukraine with BadPaw and MeowMeow malware, using steganography and feline decoys for stealthy espionage.
APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.

APT28 (Fancy Bear) weaponized CVE-2026-21509 in 24 hours to target NATO. New "BeardShell" and "NotDoor" malware steals emails. Patch Office now.
APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

BlueDelta (APT28) is targeting UKR.NET users with a sophisticated phishing campaign using ngrok and Mocky to bypass security and steal 2FA codes.

A new report reveals GONEPOSTAL, a backdoor by Russia's APT28 that hides in Outlook macros and uses email itself as a covert command-and-control channel for espionage.

A new report reveals NotDoor, a backdoor by Russia's APT28 that hides in Microsoft Outlook macros and uses specific email triggers to exfiltrate data and execute commands.

Russia-linked APT28 (Sednit/Fancy Bear) targets vulnerable webmail with XSS in Operation RoundPress, stealing data from global entities.

ANSSI reveals sustained cyber espionage by APT28 (Fancy Bear) targeting French institutions since 2021. Learn about their tactics and targets.

Discover the Nearest Neighbor Attack, a novel cybersecurity technique used by the Russian APT group GruesomeLarch. Learn how Wi-Fi networks can be compromised without direct physical proximity.

Uncover the evolving cyberwarfare tactics of Russian state-backed hackers. Find out how they exploit mobile devices for espionage and data theft.
The United States has formally denounced a series of cyberattacks orchestrated by Russia’s GRU, commonly identified as APT28

Forest Blizzard has leveraged GooseEgg to exploit a critical vulnerability in the Windows Print Spooler service, identified as CVE-2022-38028

APT28 has been assailing governmental entities, businesses, universities, research institutions, and analytical centers in France

The security company Palo Alto Networks threat intelligence unit Unit 42 said last week that they observed...