 Do Son
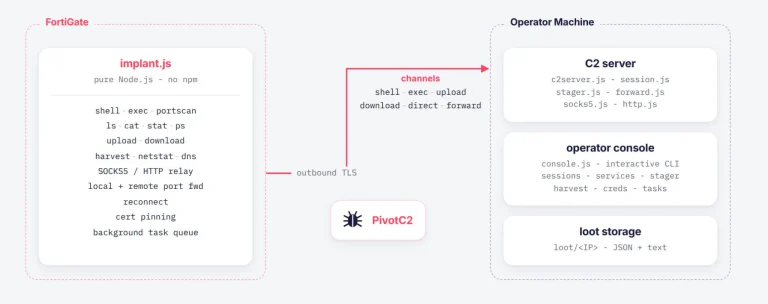
Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
FortiGate

The FortiBleed campaign exposed working logins for 30,791 Fortinet firewalls across 194 countries. This Fortinet credential leak hits every sector.

SentinelOne DFIR reveals how attackers exploit FortiGate NGFW flaws to extract credentials, abuse Active Directory, and establish persistent network access.

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

Arctic Wolf warns of automated FortiGate SSO attacks stealing configs and creating backdoors. Disable admin-forticloud-sso-login immediately.

Fortinet warns of active exploits for CVE-2020-12812, where attackers bypass 2FA on FortiGate firewalls by simply changing username capitalization.

A critical FortiGate SSO flaw (CVSS 9.1) is under active exploitation, letting unauthenticated attackers bypass login via crafted SAML. The flaw is armed by default registration, risking config exfiltration. Patch immediately.

NCSC reveals SHOE RACK, a stealthy post-exploitation malware using reverse SSH tunneling, DoH, and protocol abuse to maintain remote access on FortiGate 100D firewalls.
NCSC reveals "UMBRELLA STAND" malware targeting Fortinet FortiGate 100D firewalls. It establishes stealthy backdoors for long-term cyber-espionage

Fortinet warns of a novel persistence exploit using symbolic links in FortiGate SSL-VPNs. Upgrade to patched FortiOS versions to mitigate the threat.

Discover the shocking FortiGate leak exposing over 15,000 firewall configurations and VPN credentials. Learn more about the vulnerability and its impact on cybersecurity.

Proof-of-concept (PoC) code is now available for a critical severity vulnerability (CVE-2024-21762) in FortiOS SSL VPN