 Do Son
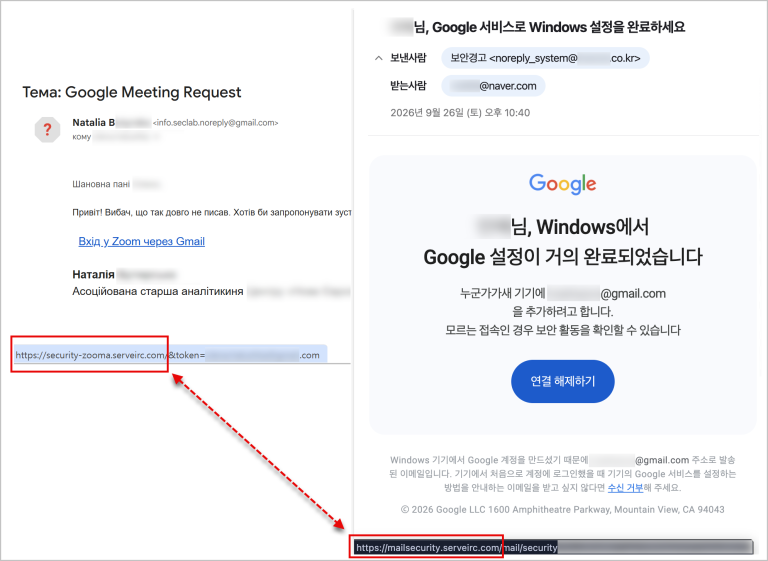
Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
Genians
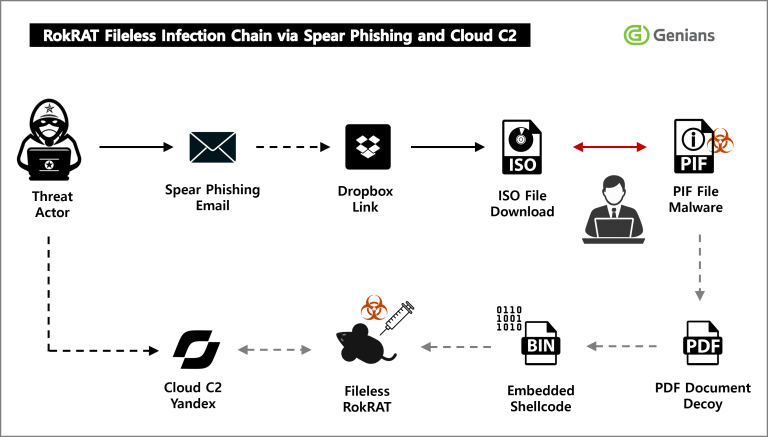
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.
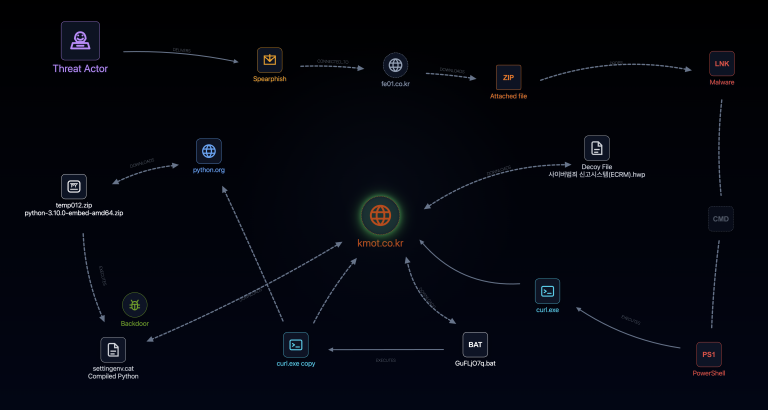
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.

Genians reveals "Operation Poseidon": Konni APT exploits Google & Naver ad redirects to bypass defenses and deploy EndRAT.

A new report reveals that the North Korean Kimsuky APT is using social engineering on Facebook and Telegram to deliver AppleSeed malware to targets in South Korea.

APT37, a North Korea-linked group, is using a new RoKRAT backdoor to target South Korea. The malware uses stealthy LNK files and steganography to evade detection.

Kimsuky's AppleSeed campaign targets Korean Facebook, email, and Telegram users with evolved social engineering and stealthy malware.