
 Do Son
Netskope uncovers Sainbox RAT (Gh0stRAT variant) and Hidden rootkit delivered via fake software installers to Chinese users, leveraging DLL sideloading and sRDI for stealth.
Gh0stRAT

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.
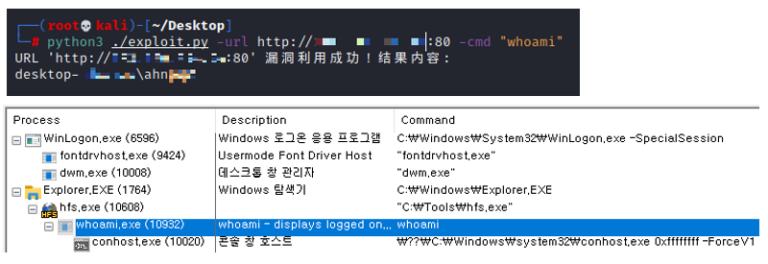
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware