 Do Son
Update to Git 2.56.1 now to fix six Git security vulnerabilities, including CVE-2026-111760 and CVE-2026-105437 for code execution and heap bugs.
git
Update self-managed servers to 19.5.4 now to fix the critical GitLab heap overflow flaw CVE-2026-105437 that allows command execution in Gitaly.
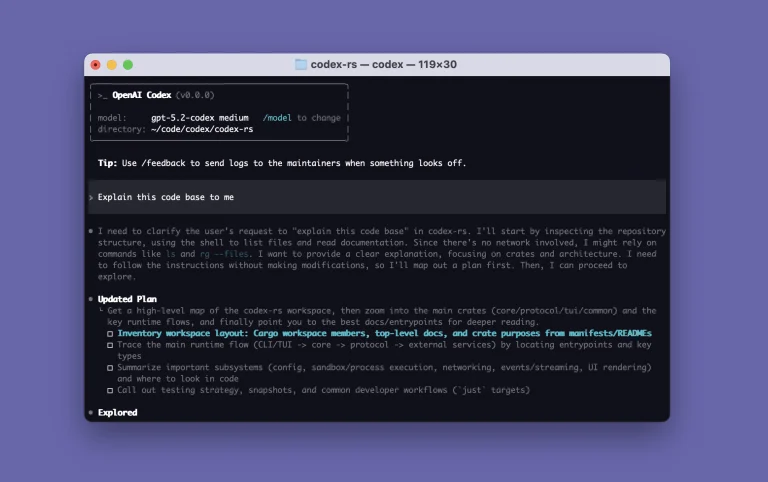
Codex SSH agent forwarding can overwrite active sockets on shared remote hosts, creating credential collisions and security risks for remote developers.
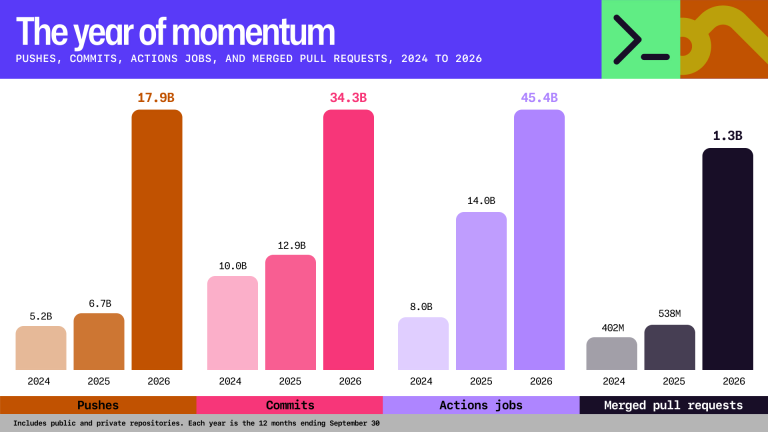
GitHub code activity reached historic highs in 2026, with over 7.3 billion monthly commits and 40% of pull requests drafted by AI coding agents.
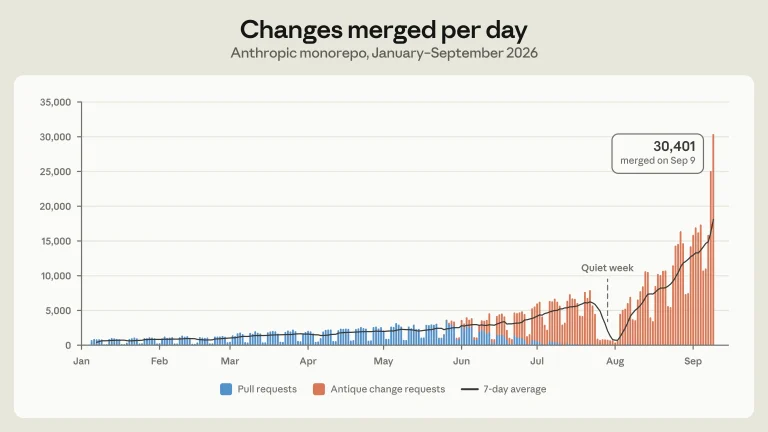
Anthropic developed the Scion version control system to replace Git for its massive monorepo and high-frequency Claude AI coding workflows.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.

A critical Forgejo remote code execution flaw, tracked as CVE-2026-89094, threatens Git servers. Patch this Forgejo remote code execution bug today.

Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.

OpenSSH (before 10.1) has a flaw (CVE-2025-61984) that allows RCE when ProxyCommand is used. Attackers exploit control characters in usernames to inject commands.
CISA has added two Citrix and one critical Git vulnerability to its KEV Catalog, warning that all three flaws are being actively exploited by malicious actors.

The Git Project has released updates addressing three significant vulnerabilities impacting Git versions up to v2.50.0, including...
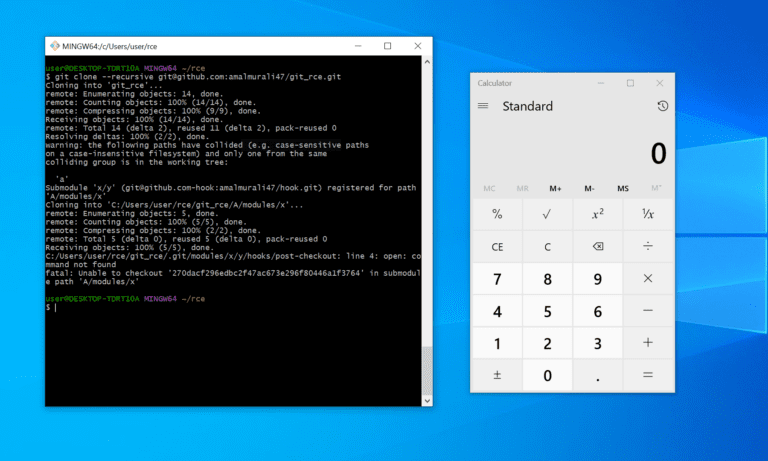
In addition to the technical details, Murali crafted a proof-of-concept (PoC) exploit for CVE-2024-32002 to demonstrate the RCE.

Tracked as CVE-2022-41903 (CVSS 9.9/10 severity), the security flaw can be exploited by sending specially-crafted input.

The main basic differences: 1.GIT is distributed, SVN is not: This is the core difference between GIT and...

In the case of project management with Git, there are some frequently encountered problems that are complicated...