 Do Son
Learn how to detect malicious Terraform providers. New malicious Terraform providers spread Graphalgo Go malware through typosquatted packages.
Go malware

Akamai SIRT uncovers a new P2P cryptominer malware threat. Learn how Ollama endpoint attacks use decentralized libp2p networks to evade detection.
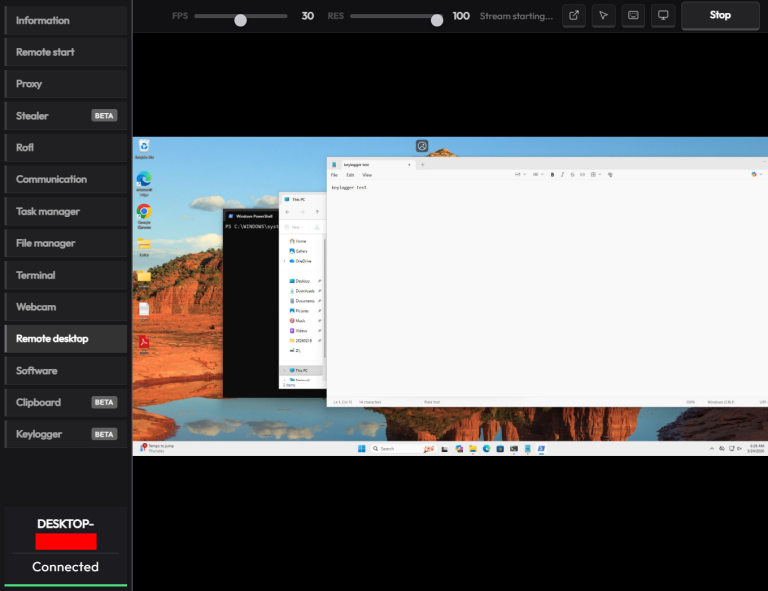
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!
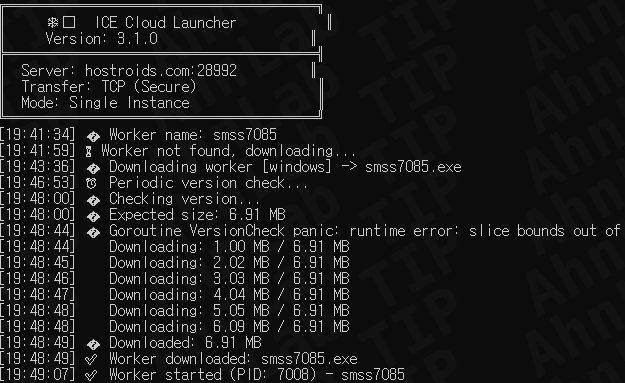
Larva-26002 strikes again with "ICE Cloud," a Go-based scanner using AI-assisted code to hijack MS-SQL servers. Discover the technical breakdown and defense.
China-linked APT UNC5174 is using a Go-based backdoor that abuses the Discord API as a covert C2 channel. This method allows the lightweight malware to execute arbitrary commands and evade traditional firewall monitoring.

ASEC exposed a VPN supply chain attack deploying NKNShell, a Go-based backdoor that uses P2P NKN and MQTT for stealthy C2. The installer bypasses AMSI using AI-generated code and grants full remote access (MeshAgent, gs-netcat).

GTIG reveals BRICKSTORM, a stealthy Go backdoor linked to China-nexus UNC5221, targeting US legal/SaaS firms to steal IP and establish long-term espionage access.

Darktrace uncovers PumaBot, a stealthy Linux botnet using Go binaries, SSH brute-force, and rootkits to compromise IoT devices, aiming for persistent, undetected access.