 Do Son
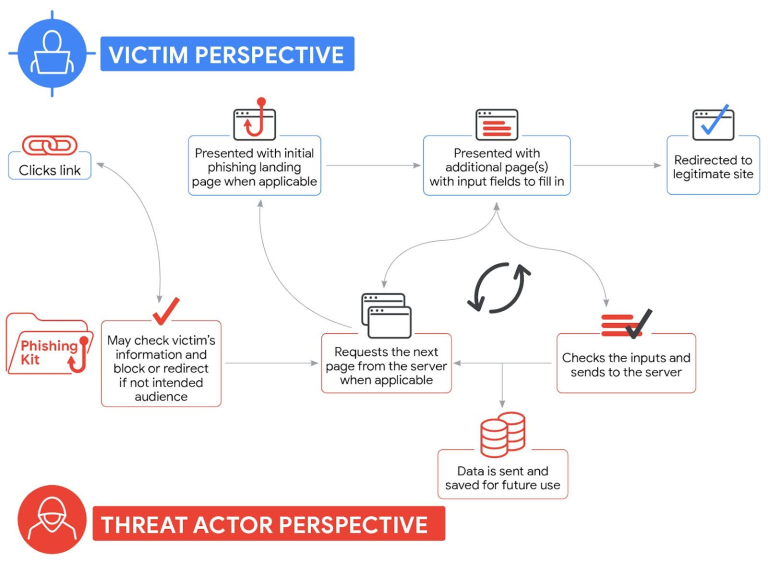
Discover how the Chinese PhaaS ecosystem uses real-time interception and AI automation to bypass MFA and exploit digital wallets.
Google Threat Intelligence
Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.
Vimeo metadata and customer emails were exposed via a breach at third-party vendor Anodot. Internal systems remain secure. Learn how to manage vendor risk.
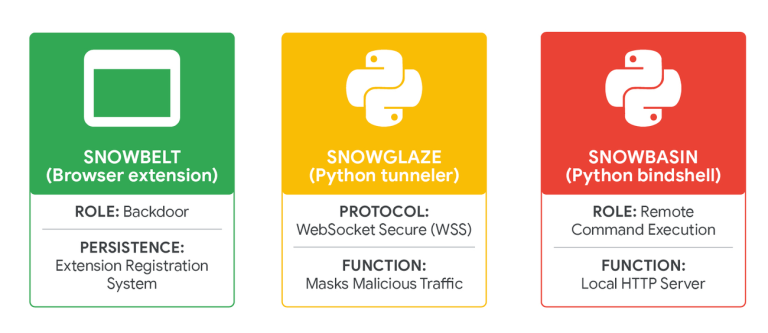
UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.
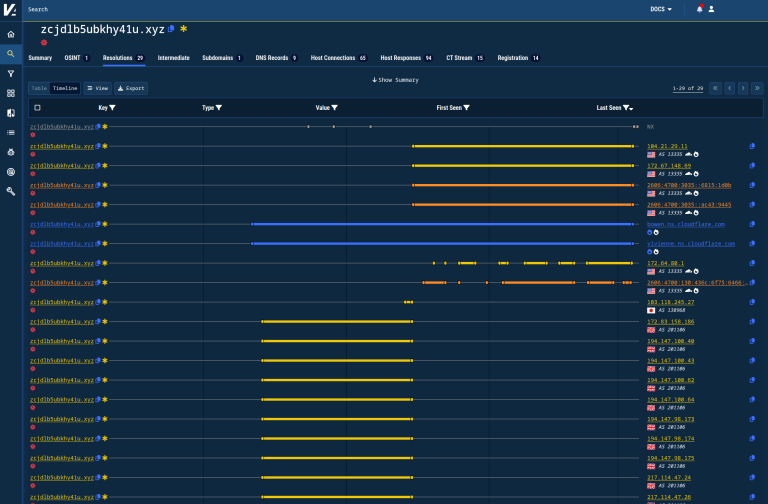
Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.
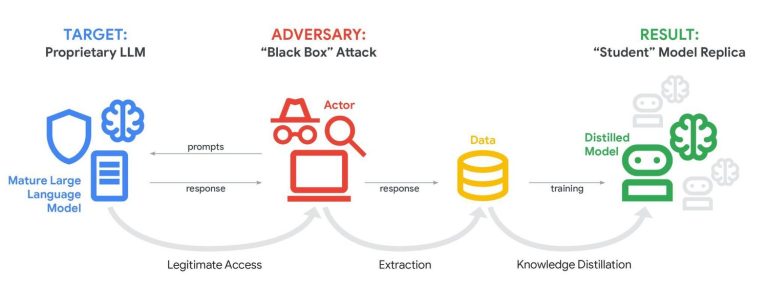
Google Threat Intelligence reports a surge in "model extraction" attacks. Private entities are cloning AI models & stealing API keys. Stay alert.

GTIG report: Defense Industrial Base faces "constant siege" from Russian drone hackers & North Korean IT insiders. Learn the new threats.
Google disrupts IPIDEA proxy network. Fake VPNs and hijacked apps turned millions of devices into unwitting exit nodes. Play Protect is removing them.

Google exposed UNC6229, a Vietnam-based group running "Fake Career" phishing on job boards. They use fake lures to compromise digital advertising accounts and corporate credentials for profit.

Google exposes a vast phishing campaign hijacking Booking.com reservation chats to steal credit card details from travelers, impacting thousands globally since Nov 2023.

A Russian state-sponsored APT, UNC6293 (likely APT29), is exploiting Google Application-Specific Passwords in a sophisticated phishing campaign targeting critics of Russia

APT41 is exploiting Google Calendar as a covert C2 channel in the TOUGHPROGRESS cyberespionage campaign, targeting government entities with stealthy malware.