 Do Son
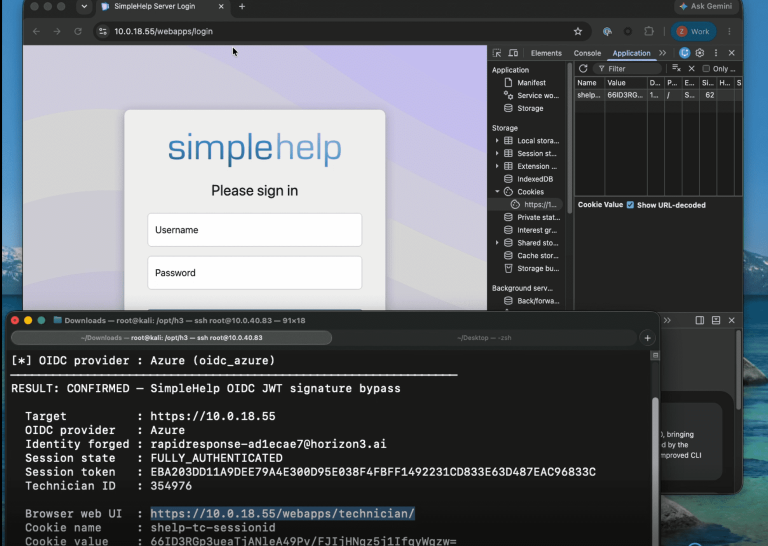
A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.
Horizon3.ai

Critical SolarWinds Web Help Desk flaws (CVSS 9.8) allow unauthenticated RCE and auth bypass. Hardcoded credentials also found. Patch immediately.

PoC exploit code released for critical FortiSIEM flaw CVE-2025-64155 (CVSS 9.4). Unauthenticated RCE allows root access. Upgrade to v7.4.1 now.

CISA alerts to active exploitation of CVE-2025-3248 in Langflow. Unauthenticated RCE vulnerability poses high risk. Upgrade to 1.3.0 immediately.