 Do Son
Six Apache Syncope vulnerabilities, including CVE-2026-82232, expose severe identity management flaws. Patch your Apache Syncope servers immediately.
Identity Management
Apache Syncope patches an SQL injection (CVE-2026-57308) and a privilege escalation flaw (CVE-2026-62183). Update to 4.0.7 or 4.1.2 to stay safe.
Critical Casdoor authentication bypass flaws allow cross organization privilege escalation. Learn how to secure your identity infrastructure today.
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!
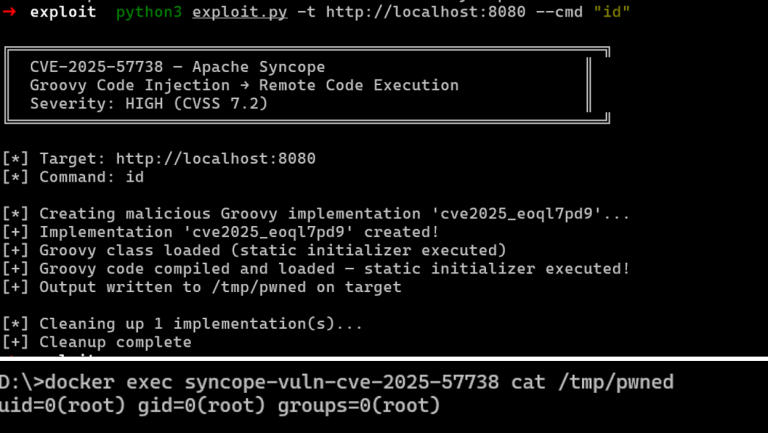
Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.
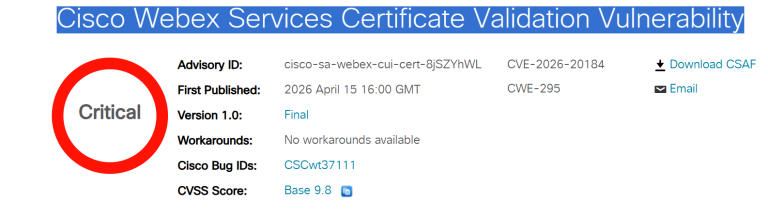
Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!

OpenStack Keystone vulnerability allows disabled LDAP users to authenticate. Logic flaw in attribute mapping affects releases up to 2026.1. Patch now!

OpenStack Keystone CVE-2026-33551 allows low-privilege users to bypass role restrictions and seize full S3 bucket control. Patch your cloud environment now!
IBM patches critical flaws in Verify Identity Access, including a 9.3 CVSS root escalation and 8.1 auth bypass. Secure your identity gateway—update now!

Apache patches XSS (CVE-2026-23794) & XXE flaws in Syncope. Vulnerability allows session hijacking via login page. Update to v3.0.16 or v4.0.4 now.

ZITADEL patched three high-severity flaws. Critical SSRF (9.3) allows internal breach via x-forward-host; XSS and Host Header Injection risk account hijack. Update to v4.7.1 immediately.
Apache warned of a Critical flaw (CVE-2025-65998) in Syncope. When AES is enabled for password storage, a hard-coded key allows attackers with database access to decrypt all user passwords. Update immediately.

A critical flaw (CVE-2025-7493) in FreeIPA allows authenticated users to exploit Kerberos alias checks to gain full domain administrator privileges. Patch to v4.12.5 now.

A critical flaw (CVE-2025-4404, CVSS 9.1) in FreeIPA allows authenticated users to escalate privileges to domain admin via Kerberos impersonation.